Обнаружение Trojan.Malware.300983.Susgen
Trojan.Malware.300983.Susgen — это название и обозначение эвристического обнаружения. Trojan.Malware.300983.Susgen предназначен для обнаружения неуказанного вредоносного ПО типа «троянский конь».
Обнаружение не соответствует какому-то одному конкретному типу троянского коня или какому-то конкретному.
Что такое эвристические обнаружения в программном обеспечении для защиты от вредоносных программ?
Эвристические обнаружения в программном обеспечении для защиты от вредоносных программ относятся к методу выявления и обнаружения потенциально вредоносного кода или поведения на основе набора правил или шаблонов. Вместо того, чтобы полагаться исключительно на известные сигнатуры вредоносного ПО, эвристическое обнаружение пытается идентифицировать ранее невидимые угрозы, анализируя их поведение и характеристики.
Программное обеспечение для защиты от вредоносных программ, использующее эвристический анализ, проверяет файлы, процессы и сетевую активность в системе на наличие подозрительного поведения, которое может указывать на присутствие вредоносного ПО. Например, он может обнаружить файл, который пытается изменить системные файлы, создать новые процессы или подключиться к подозрительным сетевым адресам.
Эвристические обнаружения могут быть очень эффективными при выявлении новых и ранее неизвестных вредоносных программ, которые могут не иметь известной сигнатуры. Однако существует также риск ложных срабатываний, когда законные программы или действия могут быть помечены как подозрительные. В результате большинство программ для защиты от вредоносных программ будут использовать комбинацию эвристического анализа и обнаружения на основе сигнатур, чтобы обеспечить наилучшую возможную защиту от вредоносных программ.
Trojan.Malware.300983.susgen
Trojan.malware.300983.susgen is a malware detection that could potentially indicate that there’s a Trojan Horse virus located on the computer. Trojan.malware.300983.susgen gets detected by the Ad-aware security tool in various types of files downloaded from the web.
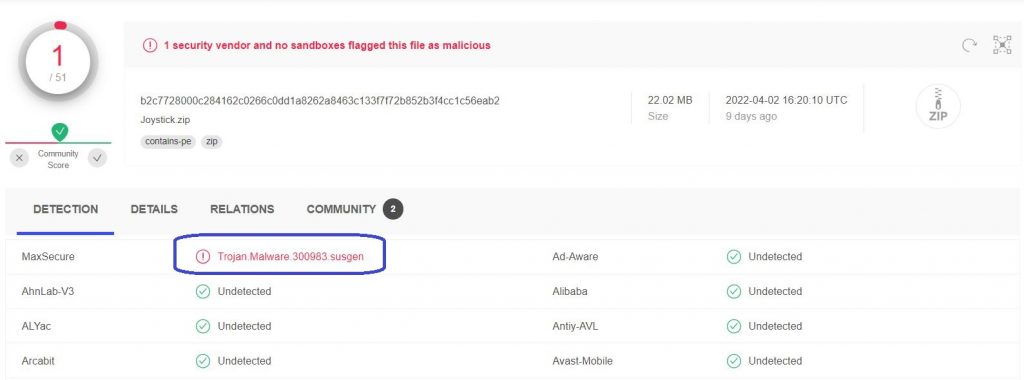
Most users who have reported that the trojan.malware.300983.susgen virus was detected on their computers have scanned a certain questionable file with the VirusTotal malware-detection tool. VirusTotal uses a number of different malware scanners to give detailed results about the files users scan with it, and in the case of trojan.malware.300983.susgen, this detection comes only from the Ad-Aware scanner, which is included in VirusTotal. None of the other scanners included in VirusTotal show this detection, which has led a lot of users to believe that the trojan.malware.300983.susgen detection might be a false positive. Though there’s certainly a chance that this could indeed be a false positive, if you have a file on your computer that triggers the trojan.malware.300983.susgen detection, then you should be careful with it. If you don’t need that file for any particular reason, it’s best to delete it. It would also be a good idea to perform a thorough check of your computer for other questionable data and potentially unwanted/harmful software that may need to be removed, especially if you’ve already interacted with the suspicious file.
What is trojan.malware.300983.susgen?
Trojan.malware.300983.susgen is a potential malware detected by the Ad-Aware security tool in various files. Though there’s a chance that the trojan.malware.300983.susgen detection is a false positive, users who’ve encountered it are still advised to check their systems for malware.
If the file in which trojan.malware.300983.susgen gets detected is something that you need, and now you are wondering whether to risk opening the file in spite of the malware warning, our recommendation is to not interact with the file without at least making sure that anything malicious that might be in it is prevented from harming your PC. Basically, what you can try is to use a sandbox environment to run the file and see if it’s safe before you start using it. Many security tools and antivirus suites offer sandbox features that give you the option to safely run and test files in an isolated environment before you decide whether they are safe for your system. This is what we think should be done with any files shown to contain the trojan.malware.300983.susgen virus. Of course, this is only relevant if you actually need to access and use the file. If you do not, deleting the suspicious piece of data is always the best option.
Trojan.malware.11973.susgen
Trojan.malware.11973.susgen is a variation of the trojan.malware.300983.susgen malware that’s typically detected by Ad-Aware in archives downloaded from file-sharing sites. The trojan.malware.11973.susgen detection is often a false positive, but it could also be a serious malware threat.
The reason it’s often assumed that trojan.malware.11973.susgen is a false positive is that only one out of the dozens of security tools included in VirusTotal detects this malware. Indeed, this could truly mean that there’s no actual threat in the scanned file. However, we believe that safety should come first, which is why it’s important to not overlook such warnings and instead try to do everything you can to ensure that your system is indeed safe. As mentioned, trojan.malware.11973.susgen gets detected in different archive files and other pieces of data that come from the Internet, while some of them may be perfectly safe, others may contain potentially unwanted or even dangerous components. For this reason, if you have one or more files on your PC that trigger the trojan.malware.11973.susgen detection, we strongly recommend completing the guide we’ve shown on this page in order to ensure that there’s truly no malware located on your PC
Trojan.malware.12132270.susgen
Trojan.malware.12132270.susgen is a trojan.malware.300983.susgen variant, which Ad-Aware detects in various .zip files. Although other security tools may not detect trojan.malware.12132270.susgen in the same files, users shouldn’t ignore this detection and should delete the flagged files.
Trojans, in general, can be very dangerous and if there’s a hidden Trojan virus in a file on your computer that gets detected as trojan.malware.12132270.susgen or trojan.malware.300983.susgen, you shouldn’t ignore and overlook the warning. Although false positives are not uncommon, you shouldn’t rely on that possibility and open the flagged file/files without a safety net. As mentioned earlier in the guide, suspicious files that may contain Trojan Horse or other malware components should only be run in sandbox environments or, better yet, should be directly deleted if they aren’t necessary to the user.
SUMMARY:
Remove Trojan.malware.12132270.susgen
If you are looking for a way to remove Trojan.malware.12132270.susgen you can try this:
- Click on the Start button in the bottom left corner of your Windows OS.
- Go to Control Panel -> Programs and Features -> Uninstall a Program.
- Search for Trojan.malware.12132270.susgen and any other unfamiliar programs.
- Uninstall Trojan.malware.12132270.susgen as well as other suspicious programs.
Note that this might not get rid of Trojan.malware.12132270.susgen completely. For more detailed removal instructions follow the guide below.
If you have a Windows virus, continue with the guide below.
If you have a Mac virus, please use our How to remove Ads on Mac guide.
If you have an Android virus, please use our Android Malware Removal guide.
If you have an iPhone virus, please use our iPhone Virus Removal guide

Some of the steps will likely require you to exit the page. Bookmark it for later reference.

WARNING! READ CAREFULLY BEFORE PROCEEDING!
 We get asked this a lot, so we are putting it here: Removing a malware manually may take hours and damage your system in the process. We recommend downloading SpyHunter to see if it can detect the malware for you.
Press CTRL + SHIFT + ESC at the same time and g o to the Processes Tab . Try to determine which processes are dangerous.
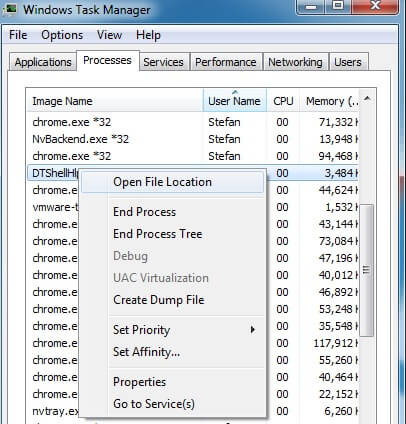
Right click on each of them and select Open File Location . Then scan the files with our free online virus scanner:

A fter you open their folder, end the processes that are infected, then delete their folders.
Note: If you are sure something is part of the infection – delete it, even if the scanner doesn’t flag it. No anti-virus program can detect all infections.

Hold together the Start Key and R . Type appwiz.cpl –> OK.
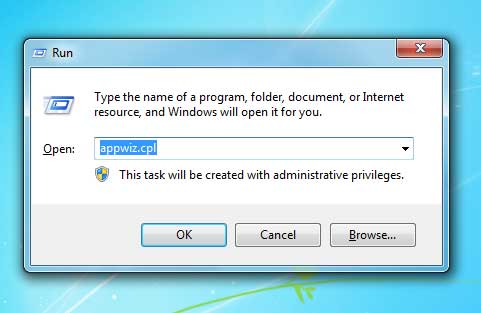
You are now in the Control Panel . Look for suspicious entries. Uninstall it/them . If you see a screen like this when you click Uninstall , choose NO:
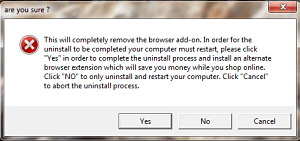

To remove parasite on your own, you may have to meddle with system files and registries. If you were to do this, you need to be extremely careful, because you may damage your system.
If you want to avoid the risk, we recommend downloading SpyHunter
a professional malware removal tool.
Type msconfig in the search field and hit enter. A window will pop-up:
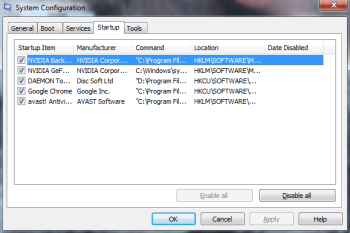
Startup —> Uncheck entries that have “Unknown” as Manufacturer or otherwise look suspicious.
- Remember this step – if you have reason to believe a bigger threat (like ransomware) is on your PC, check everything here.
Hold the Start Key and R – copy + paste the following and click OK:
notepad %windir%/system32/Drivers/etc/hosts
A new file will open. If you are hacked, there will be a bunch of other IPs connected to you at the bottom. Look at the image below:
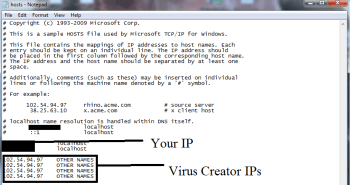
If there are suspicious IPs below “Localhost” – write to us in the comments.

Type Regedit in the windows search field and press Enter.
Once inside, press CTRL and F together and type the virus’s Name. Right click and delete any entries you find with a similar name. If they don’t show up this way, go manually to these directories and delete/uninstall them:
- HKEY_CURRENT_USER—-Software—–Random Directory. It could be any one of them – ask us if you can’t discern which ones are malicious.
HKEY_CURRENT_USER—-Software—Microsoft—-Windows—CurrentVersion—Run– Random
HKEY_CURRENT_USER—-Software—Microsoft—Internet Explorer—-Main—- Random
If the guide doesn’t help, download the anti-virus program we recommended or try our free online virus scanner. Also, you can always ask us in the comments for help!
About the author
Brandon Skies
Brandon is a researcher and content creator in the fields of cyber-security and virtual privacy. Years of experience enable him to provide readers with important information and adequate solutions for the latest software and malware problems.
Как удалить Trojan.Malware.300983.susgen
Trojan.Malware.300983.susgen — это вирусный файл, заражающий компьютеры. Trojan.Malware.300983.susgen захватывает компьютер, собирает личные данные или пытается манипулировать компьютером, чтобы хакеры могли получить к нему доступ.
Если ваш антивирус отображает уведомление о Trojan.Malware.300983.susgen, значит, остались лишние файлы. Эти файлы, связанные с Trojan.Malware.300983.susgen, следует удалить. К сожалению, зачастую Антивирусу удается лишь частично удалить остатки Trojan.Malware.300983.susgen.
Вирус Trojan.Malware.300983.susgen может быстро распространяться по вашему компьютеру. Он делает это путем копирования файлов, изменения файлов и отключения критических Windows компоненты. После того, как вирус достиг вашего компьютера, он может распространиться дальше по компьютерной сети или Интернету.
Если вирус распространяется по компьютерной сети, вирус Trojan.Malware.300983.susgen сначала ищет жертв. Найдя других жертв, он копирует вирус и запускает процесс заново.
После захвата компьютера Trojan.Malware.300983.susgen ищет личные данные. Затем эти личные данные могут быть украдены и использованы для рассылки спама или мошенничества с идентификацией.
Таким образом, необходимо удалить все остатки Trojan.Malware.300983.susgen. Эта статья расскажет вам, как полностью удалить Trojan.Malware.300983.susgen с вашего компьютера. Все программное обеспечение, рекомендованное в этой статье, можно установить и использовать вместе с установленным антивирусным программным обеспечением без какой-либо пробной версии.
Как удалить Trojan.Malware.300983.susgen
Malwarebytes — важный инструмент в борьбе с вредоносными программами. Malwarebytes может удалить многие типы вредоносных программ Trojan.Malware.300983.susgen, которые другие программы часто пропускают. Malwarebytes абсолютно ничего вам не стоит. Когда дело доходит до очистки зараженного компьютера, Malwarebytes всегда был бесплатным, и я рекомендую его как важный инструмент в борьбе с вредоносными программами.
Нажмите Scan чтобы запустить вредоносное ПОscan.
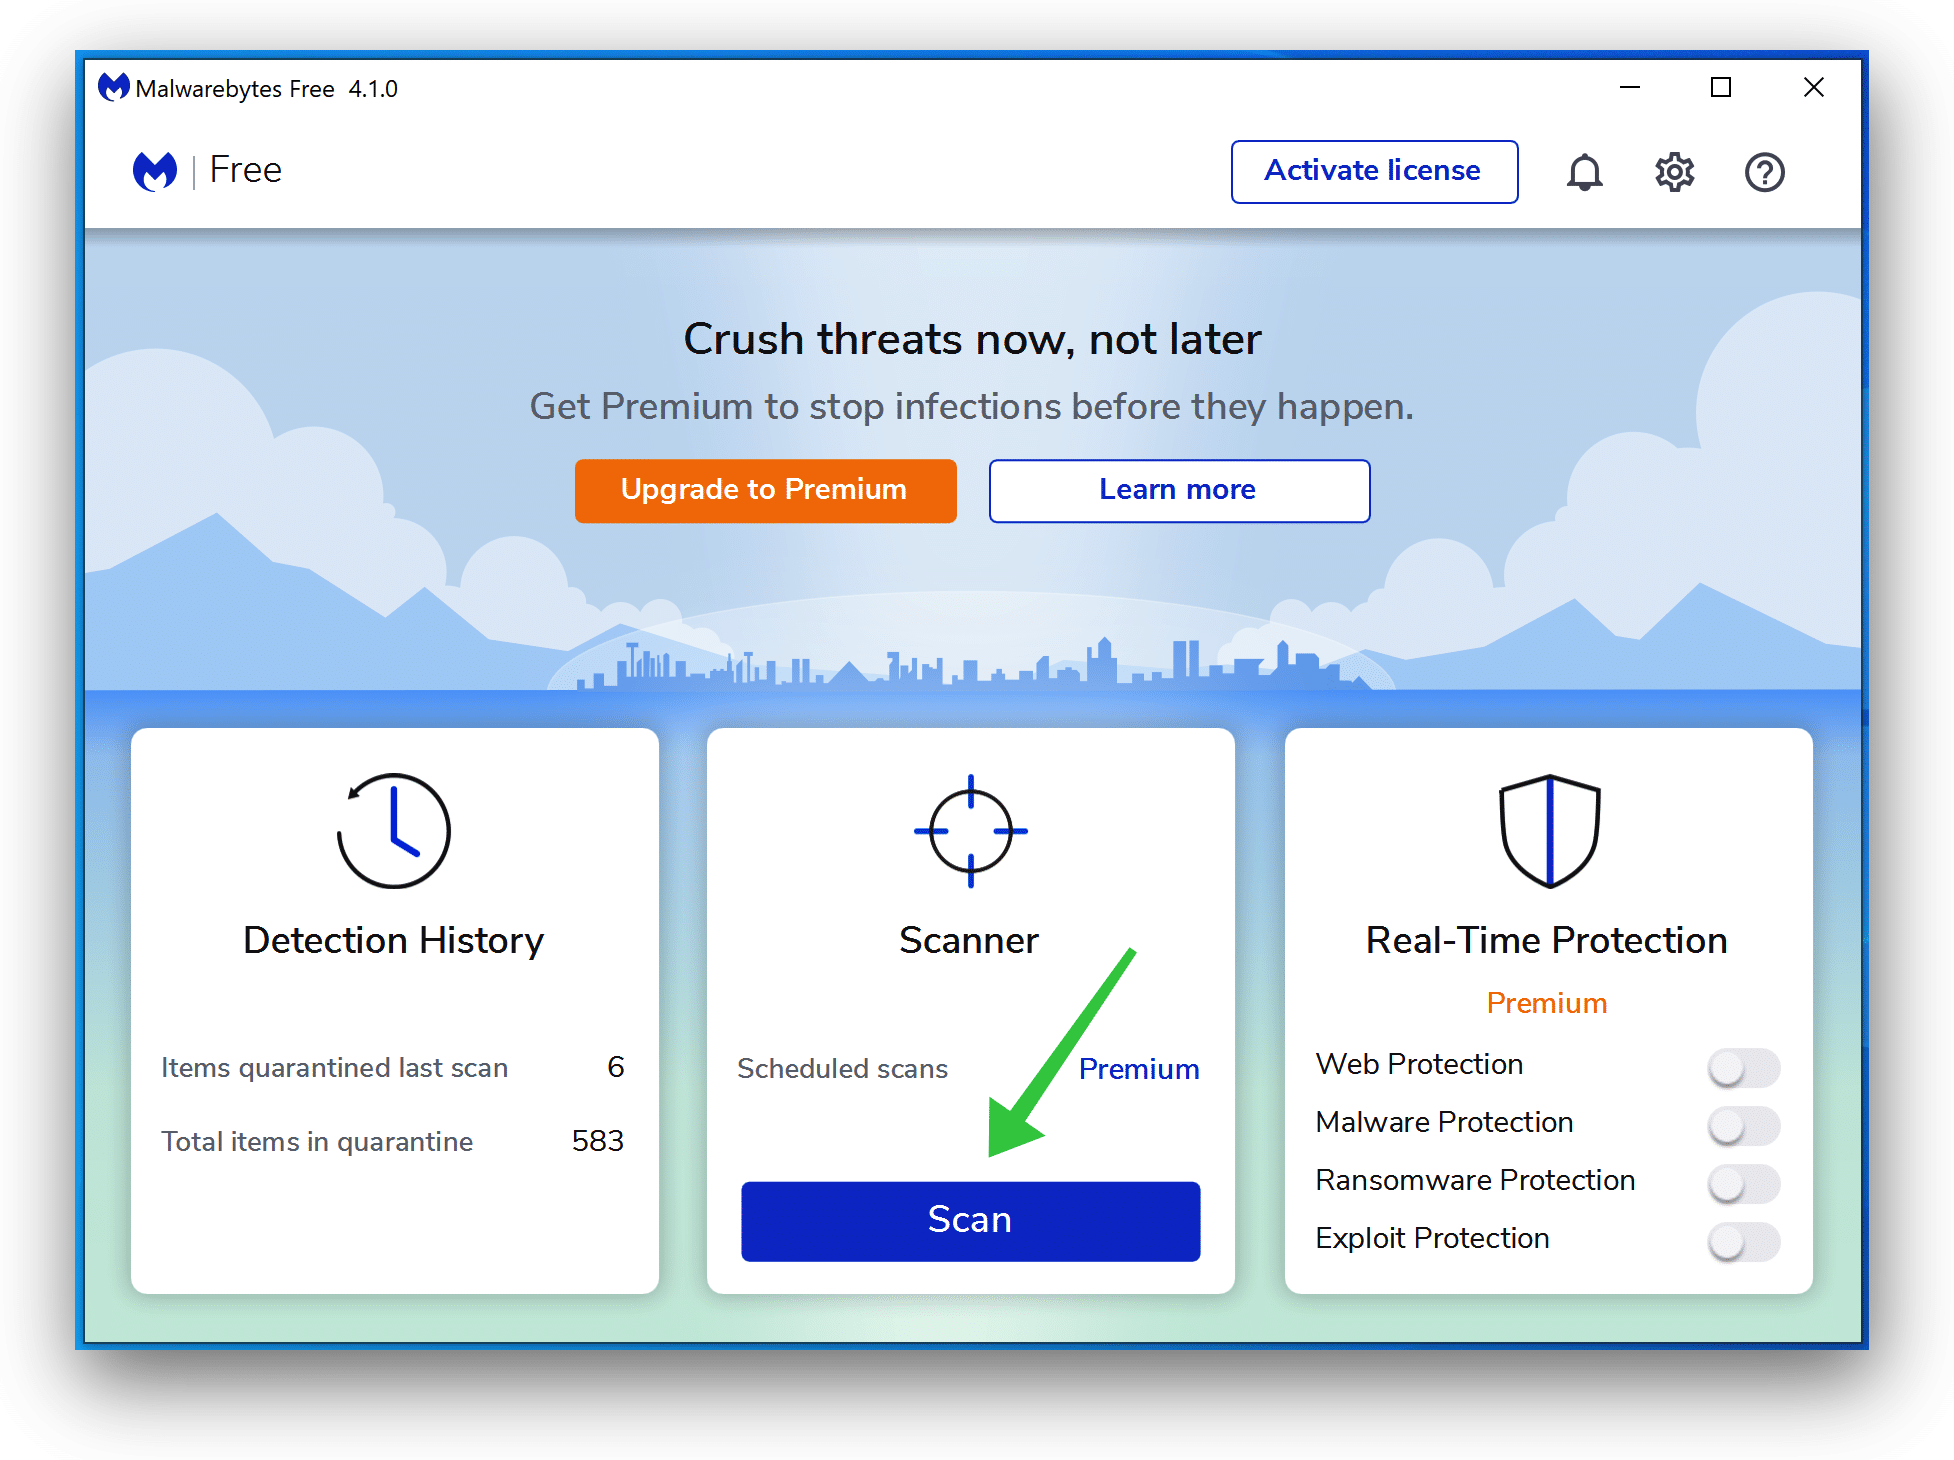
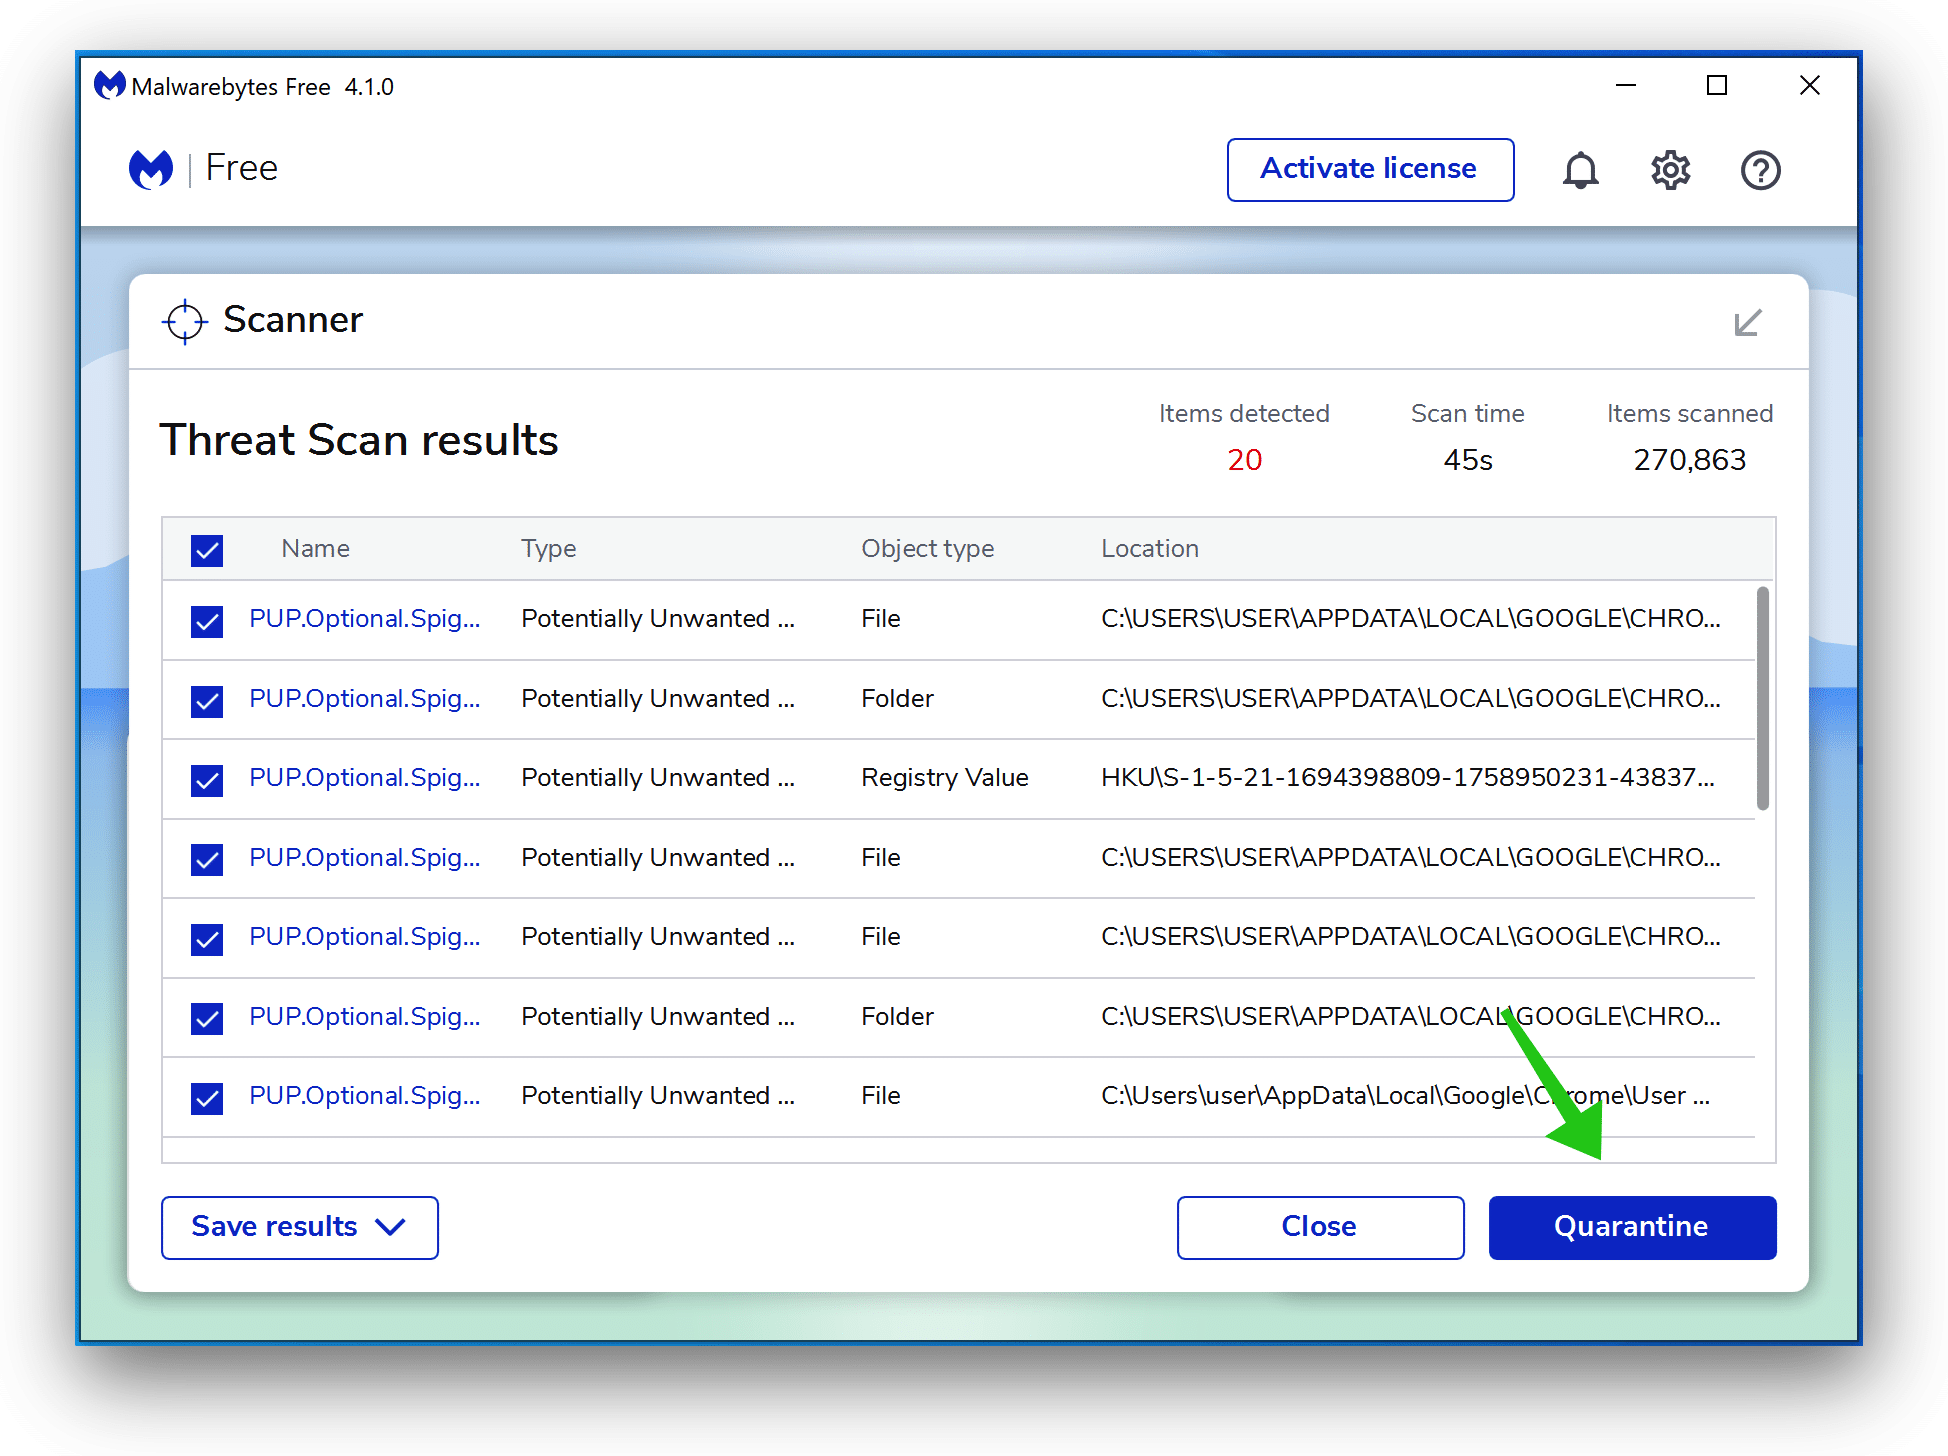
Подождите, пока Malwarebytes scan заканчивать. После завершения просмотрите обнаружение рекламного ПО Trojan.Malware.300983.susgen.
Нажмите Карантин для продолжения.
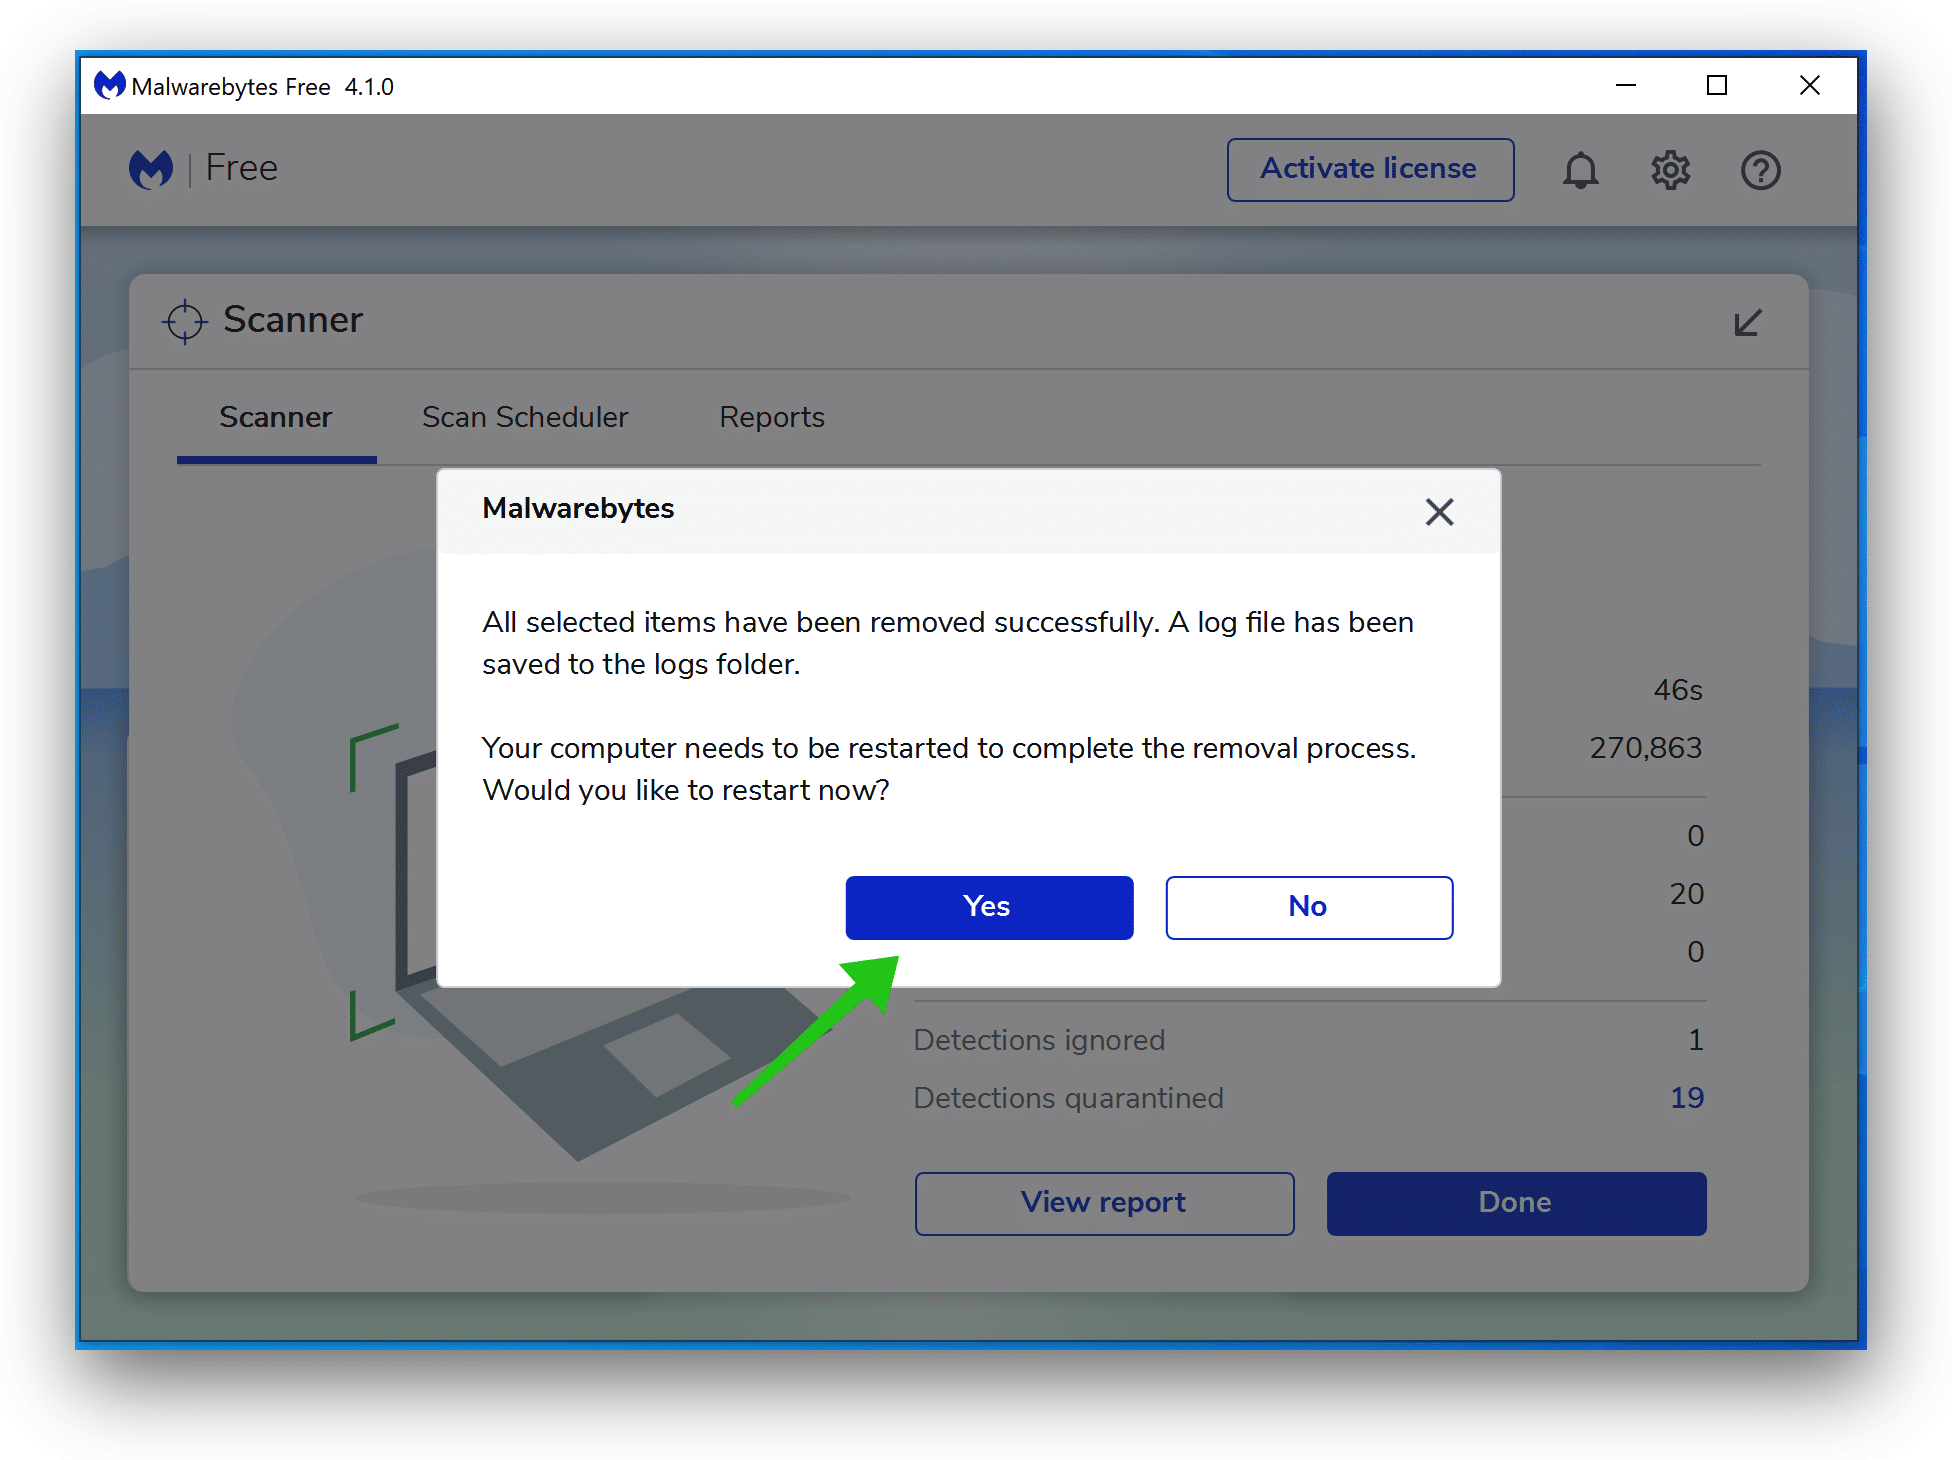
Перезагружать Windows после того, как все обнаруженные рекламные программы будут перемещены в карантин.
Переходите к следующему шагу.
Удалите нежелательные программы с помощью Sophos HitmanPRO
На этом втором этапе удаления вредоносных программ мы начнем второй scan чтобы убедиться, что на вашем компьютере не осталось остатков вредоносного ПО. HitmanPRO — это cloud scanнер это scans каждый активный файл на предмет вредоносной активности на вашем компьютере и отправляет его в Sophos cloud для обнаружения. В Софосе cloud как антивирус Bitdefender, так и антивирус Касперского scan файл для злонамеренных действий.
После загрузки HitmanPRO установите 32-разрядную версию HitmanPro или HitmanPRO x64. Загрузки сохраняются в папке «Загрузки» на вашем компьютере.
Откройте HitmanPRO, чтобы начать установку, и scan.
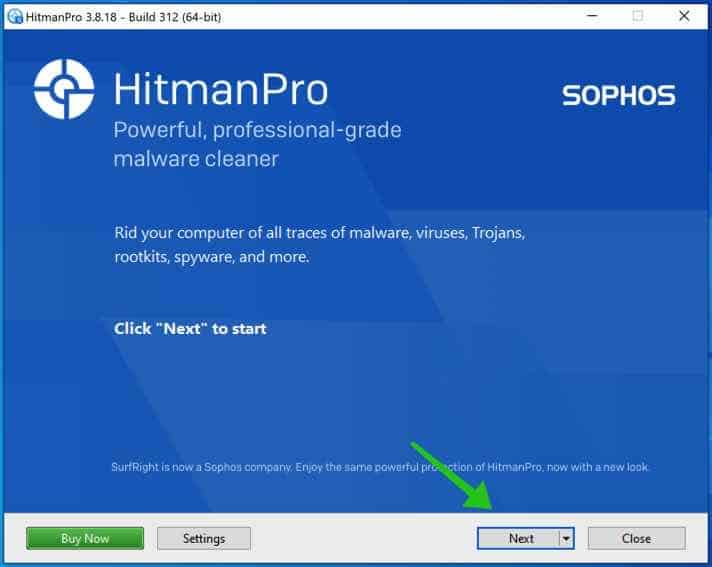
Примите лицензионное соглашение Sophos HitmanPRO, чтобы продолжить. Прочтите лицензионное соглашение, установите флажок и нажмите Далее.
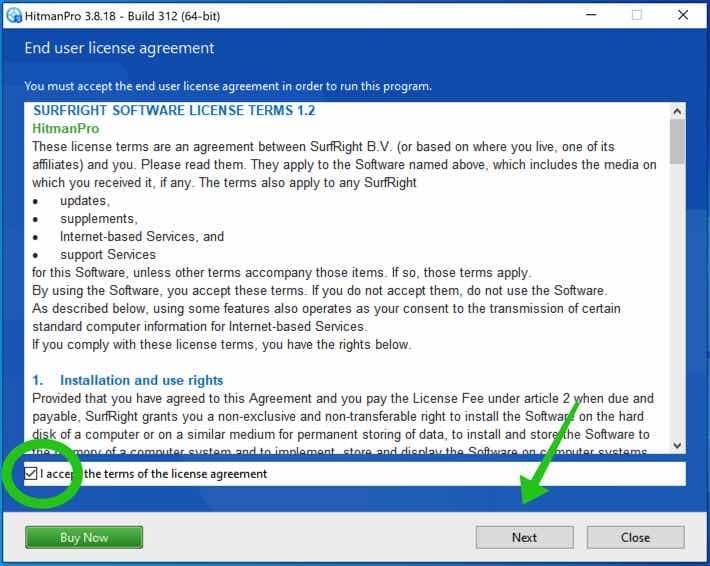
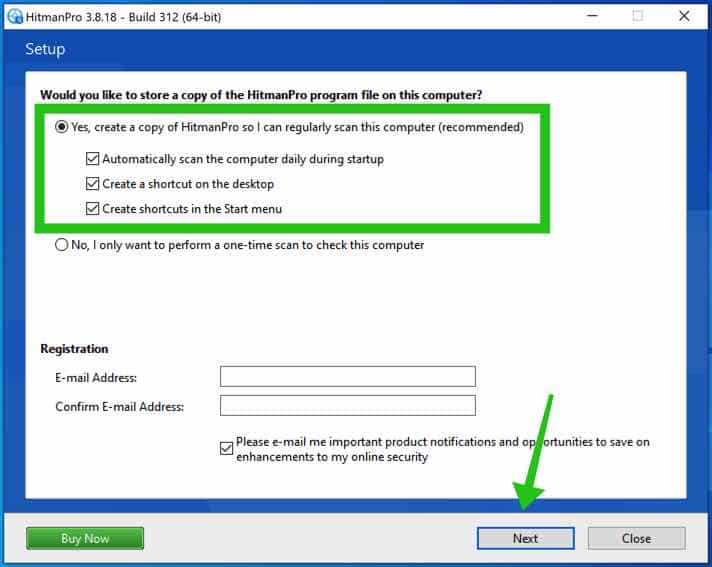
Нажмите кнопку «Далее», чтобы продолжить установку Sophos HitmanPRO. Обязательно создайте копию HitmanPRO для регулярного использования. scans.
HitmanPRO начинается с scan, дождитесь антивируса scan результаты.
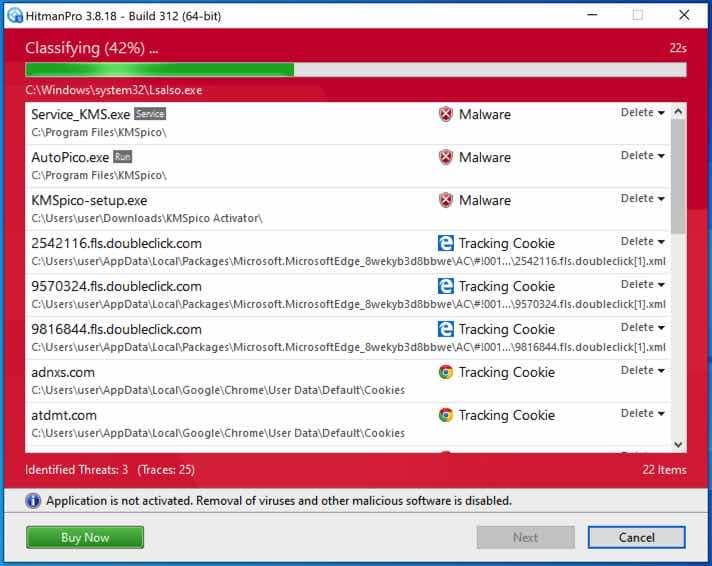
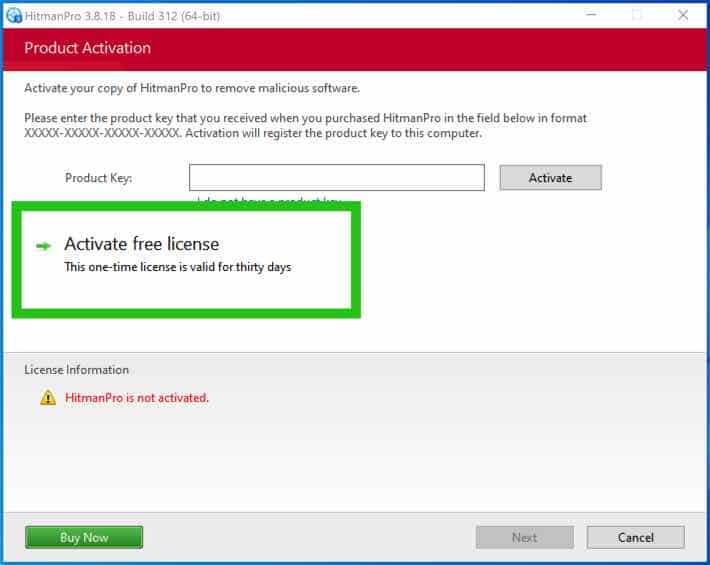
Когда scan готово, нажмите Далее и активируйте бесплатную лицензию HitmanPRO. Нажмите Активировать бесплатную лицензию.
Введите свой адрес электронной почты, чтобы получить бесплатную XNUMX-дневную лицензию Sophos HitmanPRO. Щелкните Активировать.
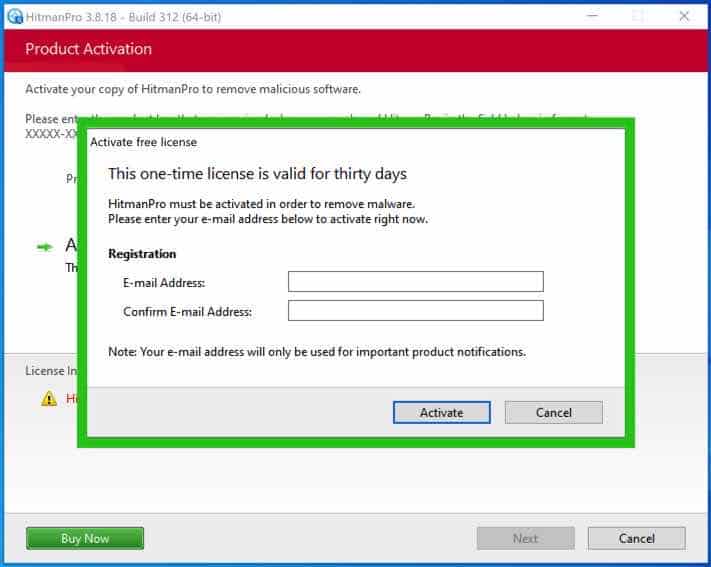
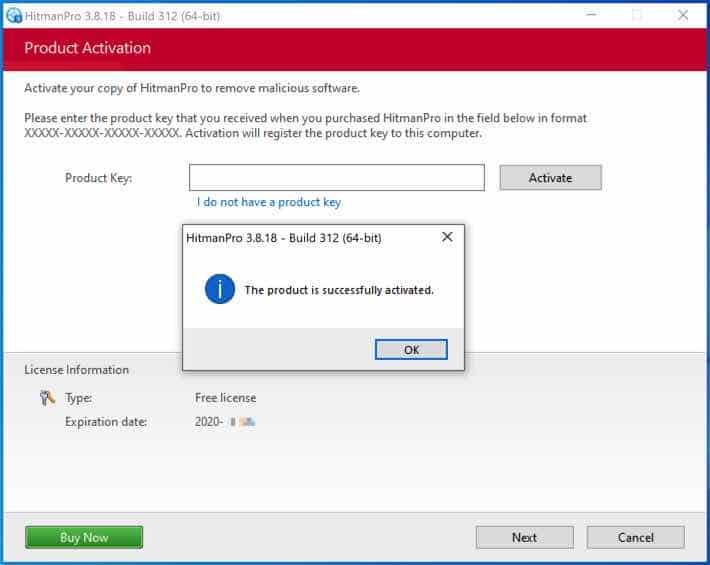
Бесплатная лицензия HitmanPRO успешно активирована.
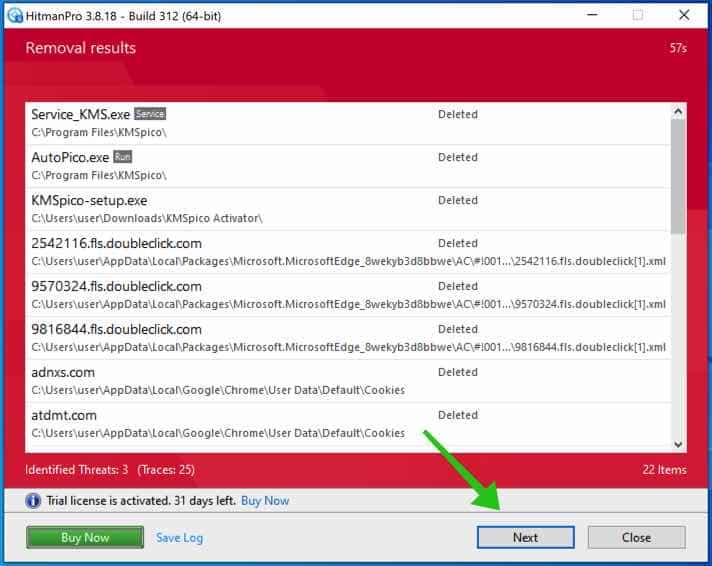
Вам будут представлены результаты удаления вредоносных программ, нажмите «Далее», чтобы продолжить.
Вредоносное ПО было частично удалено с вашего компьютера. Перезагрузите компьютер для завершения удаления.
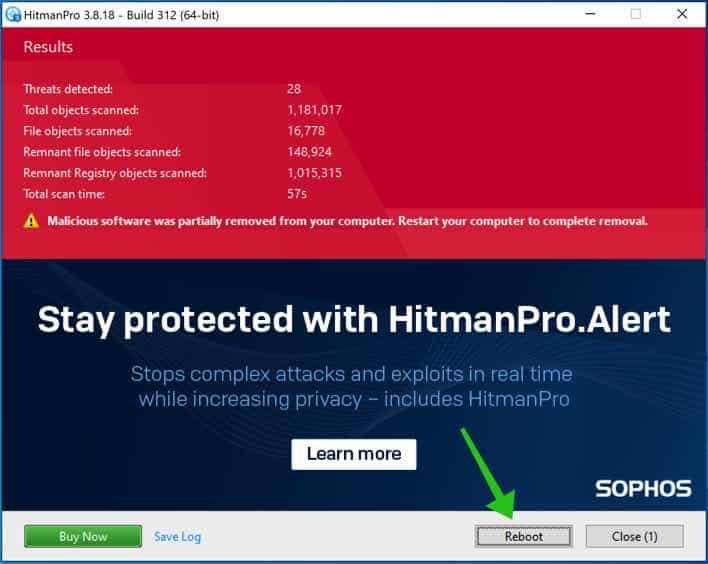
Добавьте эту страницу в закладки при перезагрузке компьютера.

Привет! Я Максим. Я исследую вредоносное ПО. Я веду блог о вредоносных программах и компьютерных вирусах по мере их появления, поэтому вы можете использовать его для удаления вирусов со своего компьютера, телефона или планшета. Эта информация полезна? Делитесь в социальных сетях и помогайте другим Спасибо!
Bablosoft
Почему в моем скрипте Trojan.Malware.300983.susgen?
@DoctorKrolic
Dear Valueded customer.
Be aware that the script is safe and antivirus are not!
Disable your antivirus imediately!
^^ 🙂
прикрипи файл под хед. я сделаю полный анализ почему у вас дитект
Да, Virustotal стал ругаться на exe файл скомпилированных скриптов и файл Qt5Core.dll в папке скрипта
Многим прогерам та пофиг, наверно, а вот, как людЯм пояснять за «вирусы». Вопрос.
Так ладно бы «популярные» антивирусы, так нет, какие то ноунэймы «ругаются».
И начинаются качели про цифровую подпись.
Многим прогерам та пофиг, наверно, а вот, как людЯм пояснять за «вирусы». Вопрос
Да не то чтобы пофиг, но если не получается объяснить то просто посылаю лесом, буквально недавно у меня сразу несколько к ряду таких попалось. Ну если человек не понимает, что во первых это всего лишь один малоизвестный антивирус, а во вторых он сам запускает мой софт и если я злой хакер то в таком случае мне не нужен никакой вирус и я «легально» могу делать на его ПК все что захочу!