Фальшивый троян
Троян Phonzy — это тип банковского трояна, относящегося к семейству троянов-похитителей. Этот тип троянов становится все более распространенным с ростом онлайн-банкинга во всем мире. Как следует из названия, банковские трояны предназначены для кражи учетных данных банковского счета пользователя. Банки обычно имеют механизмы безопасности для предотвращения таких попыток, но банковские трояны оснащены методами обхода этих уровней безопасности.
Троянец Phonzy может получать банковские учетные данные различными способами. Для банков, у которых отсутствует защита от кражи на страницах онлайн-банкинга, троянец может просто скопировать и вставить учетные данные пользователя в отдельный файл, который затем отправляется на командный сервер. Однако банки, которые уделяют первостепенное внимание безопасности клиентов, вынуждают трояна идти более окольным путем. Trojan:Script/Phonzy.A!ml может изменять сетевые настройки пользователя и настройки браузера, чтобы определить, когда пользователь обращается к защищенной банковской странице. Затем он отображает пользователю хорошо продуманную фишинговую страницу, изменяя файл HOSTS. Эта поддельная страница включает только окно входа и сообщение об ошибке входа, но предназначена для того, чтобы обмануть пользователя, заставив его ввести свои учетные данные для входа.
Что такое трояны и как они могут заразить вашу систему?
Трояны, также известные как троянские кони, представляют собой тип вредоносного программного обеспечения, замаскированного под законное программное обеспечение. Они предназначены для того, чтобы обманом заставить пользователей установить или запустить их, и, получив доступ к системе, они могут выполнять различные вредоносные действия.
Трояны могут заразить систему различными способами, в том числе:
-
Вложения электронной почты: троянские программы могут рассылаться в виде вложений электронной почты, часто замаскированных под допустимый тип файла или документа.
Trojan:Script/Phonzy.C!ml Virus Symptoms & Risks
Trojan:Script/Phonzy.C!ml is a highly dangerous malware that poses significant risks to your computer’s security. Once infiltrated, Phonzy.C!ml can execute a range of harmful actions, including data theft and unauthorized session tracking. Phonzy Trojan has the potential to compromise your privacy and compromise the integrity of your system.
If your system detects the Trojan:Script/Phonzy.C!ml, it is a clear indication of trouble. Phonzy and other malware of its kind pose a significant threat as they can exploit your computer, allowing for the injection of additional malware. Phonzy.C!ml specifically belongs to the category of Downloader Trojans, which are designed to download and install malicious software onto the infected system.
Downloader Trojans, including the Trojan:Script/Phonzy.C!ml, aim to silently infiltrate your system and facilitate the injection of additional malware. When this particular Trojan is present, it puts you at risk of being exposed to various forms of malware, such as spyware or even ransomware. It is crucial to take immediate action to remove this threat from your system to safeguard your data and prevent further infections.
Malware, without exception, is designed with a single objective – to generate profits at your expense. The individuals behind these malicious entities are driven solely by their own gain and employ various tactics to achieve it. They exploit your private data, generate revenue through the ads you are exposed to, and exploit your computer’s resources, such as CPU and GPU, for cryptocurrency mining and other illicit activities. Clearly, becoming a means for their profits is not a choice anyone would willingly make. It is important to remain vigilant and take necessary measures to protect yourself against these threats.
What does the pop-up with Trojan:Script/Phonzy.C!ml detection mean?
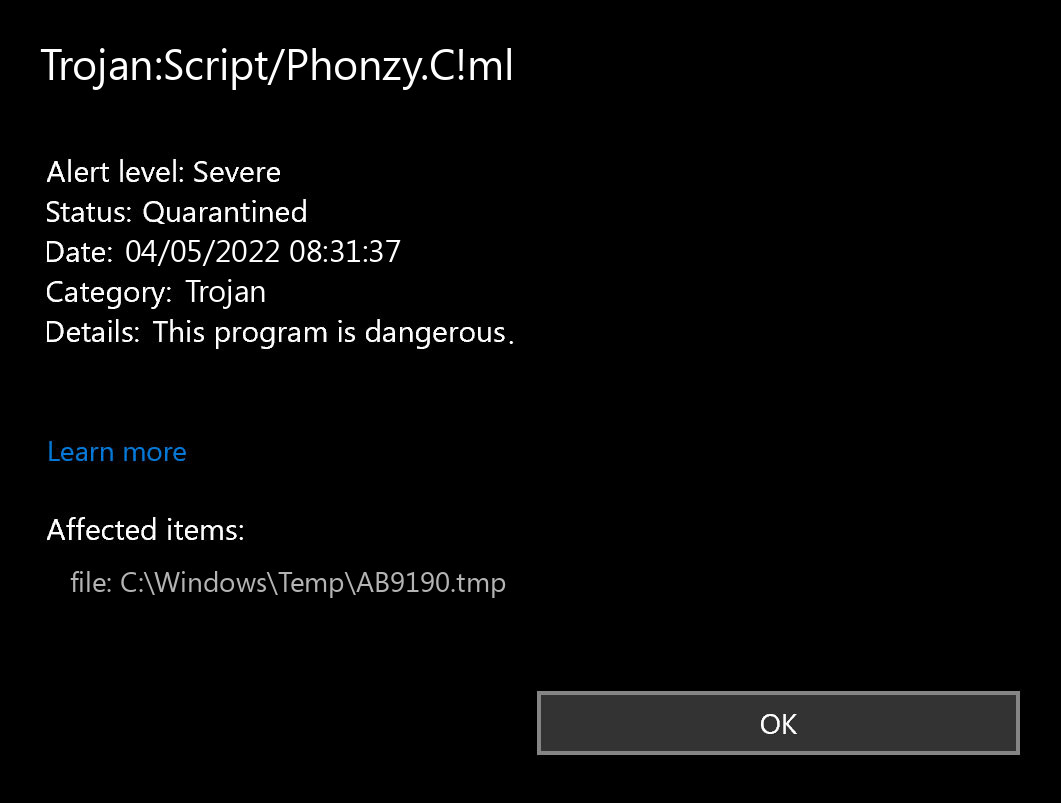
Microsoft Defender presents the detection of Trojan:Script/Phonzy.C!ml in the lower right corner. This notification is displayed by Microsoft Defender, an anti-malware application that performs decent scans but tends to be generally unstable. Although it lacks protection against malware invasions and has a glitchy interface and faulty malware removal features, the pop-up related to Phonzy simply indicates that Defender has detected the malware. To remove it, you will likely need to utilize a separate anti-malware program.
The Trojan:Script/Phonzy.C!ml virus is highly undesirable. It infiltrates your system under the guise of something benign or as part of a program downloaded from a forum. Once inside, it actively weakens your system and ultimately injects other viruses desired by the criminals controlling this particular malware. Consequently, predicting the exact effects of Phonzy’s actions is likely impossible. The unpredictability associated with malware makes it advisable to intervene promptly and prevent the malware from fulfilling its malicious tasks.
Threat Summary:
| Name | Phonzy Trojan |
| Detection | Trojan:Script/Phonzy.C!ml |
| Details | Phonzy tool that looks legitimate but can take control of your computer. |
| |
Technical details
Trojan:Script/Phonzy.C!ml also known as:
| GridinSoft | Trojan.Ransom.Gen |
| Lionic | Trojan.Win32.Cryrar.tqFl |
| Elastic | malicious (high confidence) |
| Cynet | Malicious (score: 100) |
| ALYac | Trojan.GenericKD.37347215 |
| Cylance | Unsafe |
| Zillya | Trojan.Generic.Win32.922194 |
| Alibaba | Trojan:Application/Generic.87c81b28 |
| Symantec | Trojan.Gen.2 |
| APEX | Malicious |
| Avast | Win64:Malware-gen |
| Kaspersky | Trojan-Ransom.Win32.Encoder.nkr |
| BitDefender | Trojan.GenericKD.37347215 |
| MicroWorld-eScan | Trojan.GenericKD.37347215 |
| Ad-Aware | Trojan.GenericKD.37347215 |
| Sophos | Mal/Generic-S |
| McAfee-GW-Edition | BehavesLike.Win64.Dropper.ch |
| FireEye | Generic.mg.436de87b93c215c6 |
| Emsisoft | Trojan.GenericKD.37347215 (B) |
| SentinelOne | Static AI – Suspicious PE |
| Webroot | W32.Encoder |
| Antiy-AVL | Trojan/Generic.ASMalwS.2BB2C00 |
| Microsoft | Trojan:Script/Phonzy.C!ml |
| Arcabit | Trojan.Generic.D239DF8F |
| ZoneAlarm | Trojan-Ransom.Win32.Encoder.nkr |
| GData | Trojan.GenericKD.37347215 |
| MAX | malware (ai score=81) |
| MaxSecure | Trojan.Malware.300983.susgen |
| Fortinet | PossibleThreat.PALLAS.H |
| AVG | Win64:Malware-gen |
| Paloalto | generic.ml |
Is Trojan:Script/Phonzy.C!ml dangerous?
As I have mentioned before, non-harmful malware does not exist. And Trojan:Script/Phonzy.C!ml is no exception. This malware modifies the system setups and alters the Group Policies and Windows registry. All of these components are vital for proper system operation, even in cases when we are not talking about system safety. Therefore, the malware that Phonzy contains, or which it will download later, will squeeze out maximum revenue from you. Cybercriminals can grab your data and then sell it on the black market. Using adware and browser hijacker functionality, built-in Trojan:Script/Phonzy.C!ml virus, they can make a profit by showing you the banners. Each view gives them a penny, but 100 views per day = $1. 1000 victims who watch 100 banners daily – $1000. Easy math, but sad conclusions. It is a bad choice to be a donkey for crooks.
How did I get this virus?
It is difficult to trace malware’s origins on your computer. Nowadays, things are mixed, and spreading ways chosen by adware five years ago can be utilized by spyware nowadays. However, if we abstract from the exact spreading way and will think about why it has success, the reply will be very uncomplicated – low level of cybersecurity understanding. People click on promotions on weird sites, open the pop-ups they receive in their browsers, and call “Microsoft tech support”, believing that the odd banner that says about malware is true. It is very important to understand what is legitimate – to prevent misunderstandings when attempting to identify a virus.
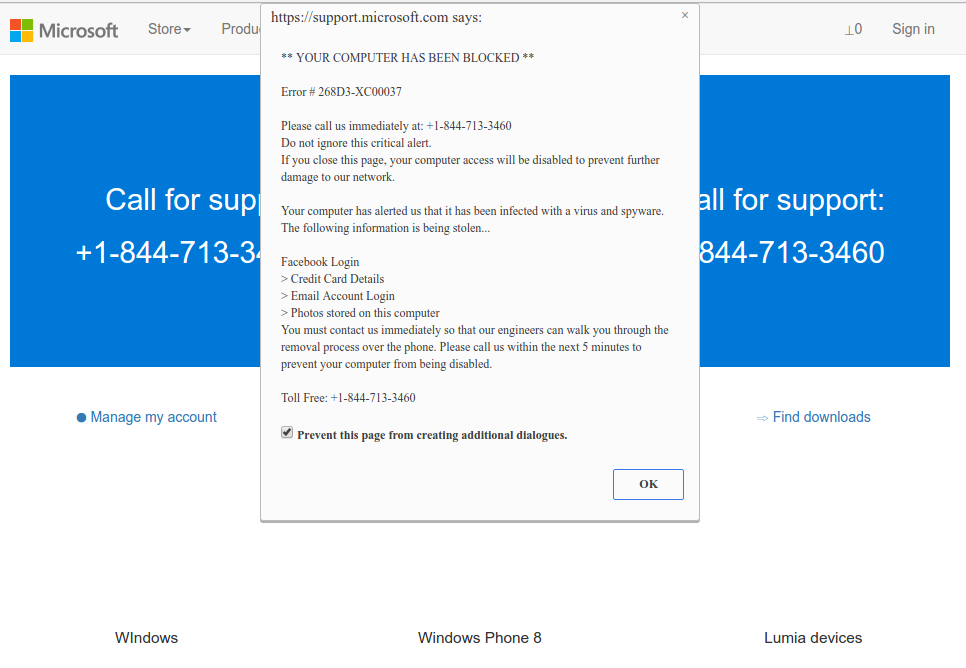
Microsoft Tech Support Scam
Nowadays, there are two of the most common tactics of malware spreading – lure emails and injection into a hacked program. While the first one is not so easy to evade – you must know a lot to understand a counterfeit – the 2nd one is easy to handle: do not use hacked programs. Torrent trackers and various other providers of “totally free” applications (which are, actually, paid, but with a disabled license checking) are a giveaway point of malware. And Trojan:Script/Phonzy.C!ml is just one of them.
How to remove the Trojan:Script/Phonzy.C!ml from my PC?
Trojan:Script/Phonzy.C!ml malware is tough to erase manually. It places its documents throughout the disk and can recover itself from one of the elements. Moreover, various changes in the registry, networking configurations and Group Policies are hard to discover and return to the initial. It is much better to use a special program – exactly, an anti-malware app. GridinSoft Anti-Malware will fit the best for malware removal goals.
Why GridinSoft Anti-Malware? It is lightweight and has its detection databases updated practically every hour. In addition, it does not have such bugs and weaknesses as Microsoft Defender does. The combination of these facts makes GridinSoft Anti-Malware ideal for getting rid of malware of any form.
Remove Trojan:Script/Phonzy.C!ml Completely [Updated]
Trojan:Script/Phonzy.C!ml is a severely dangerous Trojan horse mainly used to collect private information of computer users and send to hacker. It may install Spyware on web browser silently and then collect sensitive data. Besides, it cause poor system performance and other problems. Follow with the virus arrival, the memory space on the operating system would be largely consumed that it leads computer into slow running speed. Meanwhile, Trojan:Script/Phonzy.C!ml is very likely to exploit security leak for allowing other threats to penetrate into computer from backdoor vulnerability.

Trojan:Script/Phonzy.C!ml
Trojan:Script/Phonzy.C!ml is definitely crafty virus that there are ways to be utilized by it to penetrate into computer slightly. The very common way can be known as the infected removable device. If inadvertently plug in the device, Trojan:Script/Phonzy.C!ml can be activated immediately. Except that, malicious link, spam email attachment and porn site are also the possible carriers for the threat.
Even worse, Trojan:Script/Phonzy.C!ml is infamous for following the trail of online activities and take opportunity to steal private information for the cyber criminal. Be cautious, Trojan:Script/Phonzy.C!ml is able to force computer into blue screen of death and make you lose precious data. Seriously, as Trojan:Script/Phonzy.C!ml runs high risk to your computer that users should get it removed out from computer soon once upon the detection.
How to Remove Trojan:Script/Phonzy.C!ml? (Windows + Mac OS)
Quick Menu
Section A – Trojan:Script/Phonzy.C!ml Removal Steps For Windows OS
Section A – Trojan:Script/Phonzy.C!ml Removal Steps For Windows OS
( NOTE – Please bookmark this page first, because some steps will require you to restart your web browser or computer. )
Step 1. End malicious process run by Trojan:Script/Phonzy.C!ml and related malware.
1. Hit Ctrl + Shift + Esc keys at the same time to open Windows Task Manager:
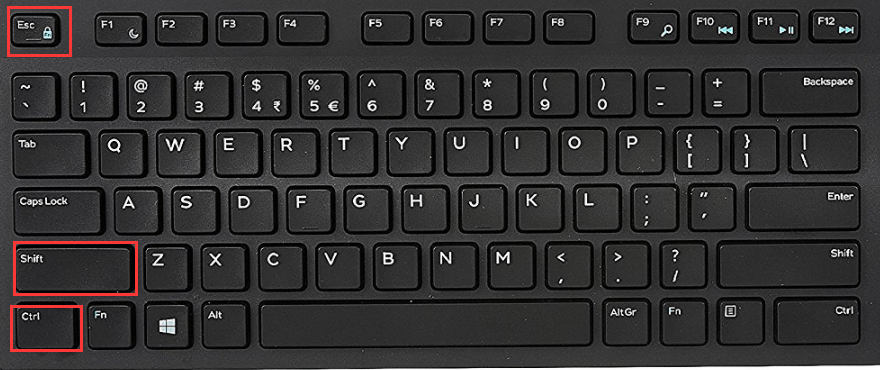
2. Find malicious process related with Trojan:Script/Phonzy.C!ml or malware, and then right-click on it and click End Process or End Task.

Step 2. Uninstall malicious programs related with Trojan:Script/Phonzy.C!ml.
Press “Win + R ” keys together to open the Run screen;

Type control panel in the Run window and click OK button;

In Control Panel, click Uninstall a program under Programs;

Look for malicious app related with Trojan:Script/Phonzy.C!ml; Right-click on the malicious program and click Uninstall.

Many malware may re-install themselves multiple times if you don’t delete thier core files. To get rid of Trojan:Script/Phonzy.C!ml completely, we recommend downloading SpyHunter Aniti-malware to scan entire system and delete all malicious files .
*OFFER – The SpyHunter Trial version includes, for one device, a one-time 7-day Trial period for SpyHunter 5 Pro (Windows) or SpyHunter for Mac. Check Terms & Conditions of SpyHunter Free Trial , EULA and Privacy/Cookie Policy.
Step 3. Delete extension installed by Trojan:Script/Phonzy.C!ml and related malware.
Chrome
On Chrome
Click the Chrome menu button >> Click Tools >> Select Extensions:

Find extension that may be related with Trojan:Script/Phonzy.C!ml or potential threat >> Click the trash can icon to delete them.

Microsoft Edge
On Microsoft Edge
Start Edge: Click the More (…) button ahe tog right corner and click Extensions:

Select the extensions you want to remove and click Remove:


Firefox
On Firefox
Click the menu button and choose Add-ons. The Add-ons Manager tab will open.

In the Add-ons Manager tab, select the Extensions panel >> find extension that may be related with Trojan:Script/Phonzy.C!ml or potential threat >> Click Remove button.

On Internet Explorer
Open the IE, click the Tools button , and then click Manage add-ons.

Choose Toolbars and Extensions on left side of the window >> Find extension that may be related with Trojan:Script/Phonzy.C!ml or potential threat>> Click Disable button

Malicious extensions may re-install itself on web browser if you don’t delete core files of Trojan:Script/Phonzy.C!ml and related malware. To get rid of Trojan:Script/Phonzy.C!ml completely, we recommend downloading SpyHunter Aniti-malware to scan entire system and delete all malicious files .
*OFFER – The SpyHunter Trial version includes, for one device, a one-time 7-day Trial period for SpyHunter 5 Pro (Windows) or SpyHunter for Mac. Check Terms & Conditions of SpyHunter Free Trial , EULA and Privacy/Cookie Policy.
Step 4. Remove malicious files created by Trojan:Script/Phonzy.C!ml or related malware.
1. Hit Windows + R keys at the same time to open Run window and input a regedit and click OK:

2. In the Registry Editor, hit Windows key + F key together to open Find window → Enter virus name → Press Enter key to start search.

3. When the search is completed, right click the folders related with Trojan:Script/Phonzy.C!ml and click Delete button:

Please Read This Before You Remove Registry Files
PLEASE Be Carefully, Do Not Delete Healthy Registry Entries, Or Your Computer May Be Damaged.
If you are not able to determine which regsitry files are malicious, we recommend downloading SpyHunter Anti-malware to scan entire system and find out all malicious files. It can avoid mistakes and may reduce the cleanup time from hours to minutes.
*OFFER – The SpyHunter Trial version includes, for one device, a one-time 7-day Trial period for SpyHunter 5 Pro (Windows) or SpyHunter for Mac. Check Terms & Conditions of SpyHunter Free Trial , EULA and Privacy/Cookie Policy.
Step 5. Reset Web Browsers to remove Hijackers Brought by Trojan:Script/Phonzy.C!ml.
Chrome
Reset Chrome:
- Click the Chrome menu button, represented by three horizontal lines;
- Click Settings when the drop-down menu appears;
- In the Settings screen, scroll to the bottom of the page and click on the “Advanced” link;
- Click on the “Reset settings to their original defaults” button.
- A confirmation dialog appears, click on the “Reset Settings” button.
Reset Microsoft Edge:
- Click on Microsoft Edge’s main menu button, represented by three horizontal dots;
- Click on “Settings“ button when the drop-down menu appears;
- Click on “Reset Settings”On the left side of the window;
- Click on “Restore settings to their default values”
- Click on the “Reset” button in the new confirmation window that opens.
Firefox
Reset Firefox:
- Click the menu button of firefox, represented by three horizontal lines;
- Click on “Help“ button when the drop-down menu appears;
- Click on “Troubleshooting Information“ from the Help menu;
- Click the “Refresh Firefox” button in the upper-right corner of the “Troubleshooting Information” page.
- Click on the “Refresh Firefox” button in the new confirmation window that opens.
Reset IE :
- Open Internet Explorer, click on the gear icon in the upper-right part of your browser, then select “Internet Options“.
- Now select the “Advanced” tab, then click on the “Reset” button
- In the “Reset Internet Explorer settings” section, select the “Delete personal settings” checkbox, then click on the “Reset” button.
NOTE – If the steps above doesn’t help, please rescan entire infected PC with Spyhunter anti-malware and let it help you fix all problems.
Section B – Trojan:Script/Phonzy.C!ml Removal Steps For Mac OS
Step 1 – Remove nasty extension and browser hijacker related with Trojan:Script/Phonzy.C!ml or malware.
Chrome
– Click the setting button “≡” at the top right of the browser window, choose “More Tools” and choose “Extensions“.

– Click the “trash can icon” button to remove extension related with Trojan:Script/Phonzy.C!ml or malware:

Safari
Safari:
– Choose Safari > Preferences

– On the ‘Extensions’ tab, find out the extension related with adware or hijacker and click Uninstall or Disable

Firefox
Mozilla Firefox:
– Click the settings button (three horizontal bars) in the top-right corner and then select ‘Add-ons’.

– Click “Extensions” tab under Add-on Manager page to view the extensions.
– Find the suspicious add-on you want to disable and click its “Disable” button.
– If you want to delete an extension entirely, click “Remove.”

Malicious browser extensions hijack your Google Search and redirect you to unwanted websites. To get rid of related search hijacker, you need to delete core files of Trojan:Script/Phonzy.C!ml and related malware. We recommend downloading SpyHunter Mac Antimalware to remove all malicious apps and hijacker for you. This may save you hours and ensure you don’t make mistakes that harm your system
*OFFER – The SpyHunter Trial version includes, for one device, a one-time 7-day Trial period for SpyHunter 5 Pro (Windows) or SpyHunter for Mac. Check Terms & Conditions of SpyHunter Free Trial , EULA and Privacy/Cookie Policy.
Step 2 – Uninstall harmful Apps related with Trojan:Script/Phonzy.C!ml or malware
– Open Finder at the Dock

– Select Applications and find out suspicious apps related with Trojan:Script/Phonzy.C!ml , then right click on the app and click Move to Trash:

– Right click on Trash icon to select Empty Trash

Step 3 – Remove malicious files generated by Trojan:Script/Phonzy.C!ml or malware from your Mac
Malware geneates lots of malicious files and folders on infected Mac, to avoid Trojan:Script/Phonzy.C!ml reinstalling itself, you need to find out and remove all malicious files:
1. Click the Finder icon from the menu bar >> choose “Go” then click on “Go to Folder“:

2. In the Go to Folder… bar, type “/Library/LaunchAgents” and click Go:

3. In LaunchAgents folder, search for any recently-added suspicious files and move them to the Trash.

Here are some examples of files generated by malware:
“installmac.AppRemoval.plist”, “com.genieo.completer.download.plist” “com.genieoinnovation.macextension.plist” “com.genieo.engine.plist” “com.adobe.fpsaud.plist” , “myppes.download.plist”, “mykotlerino.ltvbit.plist”
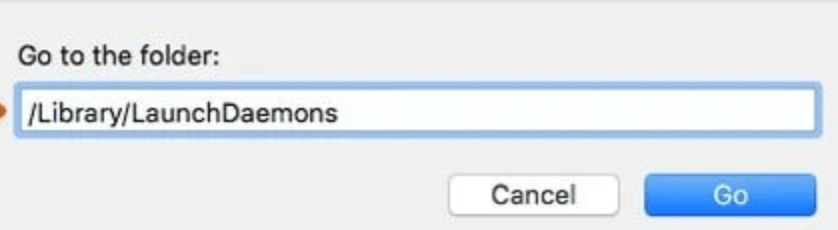
4.Repeat the process on the following folders:
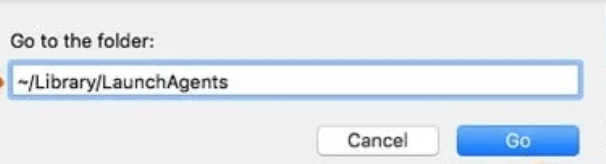
/Library/Application Support

/Library/LaunchDaemons
Many malware may re-install themselves multiple times if you don’t delete thier core files. To find and remove all malicious files , We recommend downloading SpyHunter Mac Antimalware to scan your Mac. This may save you hours and ensure you don’t make mistakes that harm your system
*OFFER – The SpyHunter Trial version includes, for one device, a one-time 7-day Trial period for SpyHunter 5 Pro (Windows) or SpyHunter for Mac. Check Terms & Conditions of SpyHunter Free Trial , EULA and Privacy/Cookie Policy.
Step 4 – Download SpyHunter Antimalware For Mac to Scan For Malicious Apps and Files.
Lots of Malware keep generating malicious files on infected computer deeply, thus it’s quite difficult for common computer users to find out and remove all harmful items related with Trojan:Script/Phonzy.C!ml. Meanwhile, there will be possibility that users remove core system files by mistake and then the entire computer will be harmed seriously.
To avoid the risks, We recommend all users downloading SpyHunter Antimalware For Mac, a professional automatic malware removal tool which keeps your Mac away from virus and malware attack and avoid online spam and phishing websites and protect your privacy and files well.
1. Click Download button here to download SpyHunter For Mac :
( *OFFER – The SpyHunter Trial version includes, for one device, a one-time 7-day Trial period for SpyHunter 5 Pro (Windows) or SpyHunter for Mac. Check Terms & Conditions of SpyHunter Free Trial , EULA and Privacy/Cookie Policy. )
2. Double-click SpyHunter-1.2-15-7043-Installer.dmg to install Spyhunter For Mac:

3. Once SpyHunter For Mac is installed, run a scan and register its full version to remove all malicious objects on your Mac.
Trojan:Win32/Phonzy.C!ml (Removal Guide)
Windows Defender may have informed you of this virus threat by alerting you that it had discovered the specific malware on your computer. These detections are Windows’ alarm signals informing you of any hazardous content it has spotted.
If it alerts you that you have a malicious virus on your system, you should not ignore it and take appropriate action to protect your device
These threats are often acquired through spam emails, infected websites, or by clicking on a link in an email. Once installed on the computer system, Trojan:Win32/Phonzy.C!ml will begin to spread across your PC via Windows System files.
This allows them to access all of the information on your computer and even take control of it. Such threats should not be kept around the computer that is why Windows Defender will keep on alerting you about the malware until you take action on it.
Here are the symptoms that users who have their devices infected with Trojan:Win32/Phonzy.C!ml are most likely to experience.
- Sudden problems with internet connection and applications
- Freezing or slowdowns in computer performance
- Difficulties opening documents or accessing files.
- Unusual pop-up ads appear online or when browsing.
- Overheat and high CPU usage.
Detections like these are particularly dangerous because they can be used to attack other users online by stealing their privacy credentials, financial information, and more.
If you think that you may have been affected by this specific type of virus, then it is important to remove it as soon as possible.
Since the detection name format matches how the built-in antimalware tool describes its discovered threats, Windows Defender is particularly the one that found the Trojan:Win32/Phonzy.C!ml from the computer.
Typically, Windows Defender would be enough to eliminate the threat it found on the computer and you would have only needed to click the quarantine button to remove it.
Unless certain circumstances prevent Windows Defender to eliminate the said malware, you may utilize Malwarebytes Anti-malware to remove it for you.
Please follow the given instructions below to remove the detected threat from your system.
Remove Trojan:Win32/Phonzy.C!ml with Malwarebytes Anti-Malware
We have also been using this software on our systems ever since, and it has always been successful in detecting viruses. It has blocked many known computer threats as shown from our tests with the software, and we assure you that it can remove Trojan:Win32/Phonzy.C!ml as well as other malware hiding on your computer.

Not to mention, it is free to use and does not come at any cost to remove the viruses it finds on your computer.
To use Malwarebytes and remove malicious threats from the computer, follow the steps below:
1. Download Malwarebytes by clicking the button below, as we have made an additional and in-depth tutorial on how to use it. Otherwise, you may go to their official website via Malwarebytes.com (Avoid misspelling as it may lead to scams).
2. Visit their download section and start a Free Download to begin installing the software on your computer.  3. Once the Malwarebytes setup file (MBsetup.exe) has finished downloading, open the executable file in File Explorer, then right-click the setup and select run as administrator to give the highest system authority and make sure Malwarebytes is installed correctly.
 4. Make sure to carefully follow the installation setup wizard’s instructions and provide the relevant information it requires. You will be prompted with questions such as Personal or Business Use, Email Address, and others.
 5. From the application’s home screen, go to the scan tab and begin running a system scan. This will scan the whole computer, including memory, startup items, the registry, and the file system. This is done so not only the residuals of Trojan:Win32/Phonzy.C!ml but also other trojan viruses hiding in the system can be detected.
 6. Since it can take a while, you should either relax and wait for it to finish or find something else to do. The length of the scan depends on the size of the files you have and the hardware capabilities of your computer. Here are some ways to make scanning faster.
7. Once the scan is finished, Malwarebytes will show the malicious viruses and threats it found on your PC. Trojan:Win32/Phonzy.C!ml will also show up on the detection results, and it will show up in a threat name such as PUP.Optional.OpenCandy, and many more.  8. Select all the detected files from the report and click the quarantine button to remove the malicious items from the computer into the protected safe quarantine zone of the anti-malware program so that they would not affect and do malicious actions the PC again.
 9. After placing the virus files in the program’s quarantine, it may prompt you to restart the computer to finalize the full system scan procedure. Please restart your computer if prompted, as it is essential. After the restart, Malwarebytes will open and display a message that the scan was complete.
Note: Don’t forget to delete the quarantined files afterward.
Simply quarantining the malware files is not enough to make sure they are completely removed. This is a very common misconception: once you click the quarantine button, it is all good and gone.
But, while its effects and harmful activities are halted, the malware is still in the system, only placed in the anti-malware program’s quarantine folders. To completely remove it from the computer, go to Detection History from the home screen, select all Quarantined items, and click Delete.

You have successfully removed Trojan:Win32/Phonzy.C!ml as well as the hidden threats on your computer. Rest assured they would not resurface again since Malwarebytes offers a premium trial for 14 days, so you could take advantage of it for free and prevent malware from infecting your system.
While the detection and removal of malware are free for Malwarebytes, the premium versions include real-time protection that ensures your computer is safe all the time. Although we encourage you to use the premium trial, you are free to purchase the full version if you find it useful.
We suggest Malwarebytes if you are looking for a removal tool and as a second opinion scanner, but if you want full-fledged antivirus software, we believe that the built-in Windows Defender is sufficient for computer security, or if you want something with a more sophisticated system and better protection: Kaspersky Free.
If you choose to uninstall Malwarebytes, you may suddenly see that Windows Defender Real-Time Protection is turned off. This is a common issue that users may face when uninstalling the software. To fix this issue, you may refer to this article.
Alternative: Kaspersky Free Antivirus
After removing Trojan:Win32/Phonzy.C!ml and other malicious threats, you may want to install antivirus software to protect your system against malware.

More importantly, running an additional scan with a different program’s threat database will alert you to hidden Trojan viruses and rootkits that were not removed from the prior scan with Malwarebytes.Kaspersky is a widely known antivirus software that has been on the market for as long as the field of cybersecurity has existed. It is acclaimed by professionals in the field and is one of the most effective antivirus programs available. With its advanced internet security protection, it can also remove additional malware from the computer.
What is the difference between anti-malware and antivirus? Anti-Malware software is designed to specifically remove malware and its variants. In addition, it employs heuristic-based detection by picking up harmful code from files.
On the other hand, an antivirus uses signature-based detection, which examines data for attacks to protect users from dangerous viruses, including keyloggers, loaders, worms, trojans, and others.

Malwarebytes and Kaspersky are identical, but Kaspersky is a better overall program since Malwarebytes’ main purpose is to remove malware, but Kaspersky has been known for comprehensive computer security protection ever since.
Based on our experience removing malware, when two different programs are used to scan, various threats are identified by one software but not by the other. Given that their threat databases differ from each other, it might be able to capture harmful viruses, rootkits, and trojans that Malwarebytes has missed.
Please be aware that if you decide to use Kaspersky, you should first uninstall Malwarebytes because having both security programs installed will cause a conflict. If you choose to do so, please remove Malwarebytes first, as it is essential to do so before we get started.
1. Click the button below to start downloading Kaspersky Antivirus on your computer. On the following page, we have provided clear details on how to install it on the computer. On the other hand, you may go to their official website by searching for the software on your web browser or typing Kaspersky.com (Beware of misspellings since cybercriminals typically use these as exploits to redirect users to malicious webpages).
2. Go to the download page for Kaspersky Free Antivirus. Before clicking download, you will be prompted to choose your continent and where your country is located. This is very important, and you should not choose a different country because you will be met with a «Not supported in your region» message during installation.  3. Once you click download, a setup file (startup.exe) will be downloaded on the computer. After it has finished downloading, open its file location, right-click the executable file, and then select Run as administrator. This will ensure that Kaspersky’s installation will be smooth and will not result in certain errors.
 4. The Kaspersky installation wizard will launch, and you can then proceed to install Kaspersky Free by following the setup instructions. If a UAC prompt appears, simply accept it and proceed with the installation.
 5. Please be patient while Kaspersky is being installed on your computer. The speed and length of the installation process will depend on your computer’s specifications. Kaspersky also mentioned that sluggishness or dark displays during the installation of their program are normal and should not be worried about.
6. To use the antivirus program, you must first create an account on the sign-in page that appears after the antivirus application has been successfully installed on the computer. If you’re looking for the sign-up button, simply enter your email exactly as it appears; if you don’t already have an account, one will be created for you.  7. Kaspersky will ask you to decide which plan to use. It will be either the Standard version or Kaspersky Plus. In this case, the standard version is all you need for now. If you want to try the premium version of Kaspersky, you may opt for Kaspersky Plus to try the features for free. You do not have to add a payment method to get started, and after the trial ends, you will be downgraded to the Standard version unless you pay for it.
 8. You will be asked if you want to install additional applications, namely Kaspersky Password Manager and a VPN. Feel free to opt for a program you might want to use; otherwise, install both, or choose not to if you do not need them.
 9. Kaspersky will ask you to scan for viruses in the background. Simply choose not to do so because we will be doing a full system scan later; however, doing a scan now will only initiate a quick scan. However, if you want to be safe, you can run the background scan now and proceed with a full system scan after.
 10. Once the antivirus application has opened, go to the security tab and click the choose a scan button. You will be presented with several different scans; go for the full system scan to ensure full computer security. Always remember to update the database because this will ensure that Kaspersky can detect newly discovered threats and exploits.
 11. A full system scan will take a long time to finish since it will look into all the files on the computer, including the registry, memory, startup applications, and many more. The scanning time will depend on how many files there are on the computer and how big the files are. Additionally, the computer’s hardware and specs will also play into how long the scan will take.
12. After the full system scan is finished, it may detect remnants of the Trojan:Win32/Phonzy.C!ml detection virus as well as other malware hiding in the computer, showing its location along with a detection name (Trojan.Win32.Generic, Exploit.Win32.Generic, etc.) given to it. Go ahead and proceed to disinfect and restart the computer.  13. The Advanced Disinfection process will then start, and depending on the amount of RAM the computer has, it could take some time. It will then request a computer restart to complete the operation.
 Your computer will now have finished the entire system scan after restarting. By doing this, you can be sure that Trojan:Win32/Phonzy.C!ml and other types of malware and viruses have been wiped from your computer.
You shouldn’t be concerned if the scan turned up no instances of malware or viruses, which indicates that there isn’t any malware on your computer. If two independent programs declare your computer safe, then that’s probably the case.
For a better and safer web browsing experience, we’ve provided a few security measures and advice below that will safeguard your browser and computer from harmful threats like worms, malware, trojans, keyloggers, stealers, and other kinds of computer viruses that will harm user data.
Protective measures for better overall security
Removing the malicious detections from the computer is one thing; keeping it secure for the future and a long period is a different thing and will require certain things to make sure you are secured, especially if you do not know most of the ins and outs of the device you are using.
Cybercriminals are always stepping up their game to make sure they infect users and extract data and money from them.
We encourage you to take the actions listed below to ensure complete security before leaving this page because we strongly promote web security and having a secure online presence.
Safeguard your data and privacy online by using a VPN application
VPNs, also known as virtual private networks, guarantee your safety and complete anonymity while you browse the internet.
In contrast to a firewall, which monitors and blocks potentially harmful connections in the network, A VPN hides the user’s connection via a tunnel so that it would appear to third parties as a different IP address and location.
This ensures that your data won’t be leaked because the program hides it. Be aware that visiting infected websites may cause your IP address and location to be disclosed; however, if you use a VPN, this will prevent your true IP address from being revealed to malware actors.
If you already had Kaspersky installed from the previous step, you had the choice to install its integrated Virtual Private Network, which is a good tool that we also advise.
However, if you decide against doing so and instead download a VPN-only program to cloak your web browsing activity, Mullvad VPN is an excellent choice for fast connections and better privacy.

Since user privacy is the main focus of a virtual private network program, Mullvad VPN excels at putting users’ privacy first. You do not need to enter your email address while registering to download their application because they maintain anonymous accounts.
If you wanted to hide or didn’t want your credit card information to be disclosed, they also accept Bitcoin payments. According to their website, they support a free internet that is devoid of surveillance and censorship.
They have also been announcing new server locations to guarantee users a fast connection anytime they want to connect to various areas throughout the world.
Use a firewall to prevent cyber attacks
A security firewall is required for every internet connection that is made. It is an essential tool that enhances security and stops online attacks.
Through a security mechanism, it controls incoming and outgoing network connections on your system and network and filters the undesirable ones. Consider it a further barrier against malicious assaults and zero-day exploits.
You don’t need to do anything if you installed Kaspersky in the previous step because the program we installed earlier comes with a built-in firewall that is turned on by default.
On the other hand, if you prefer a standalone, fully functional firewall utility application that is exclusively focused on securing the network, we recommend ZoneAlarm Firewall.
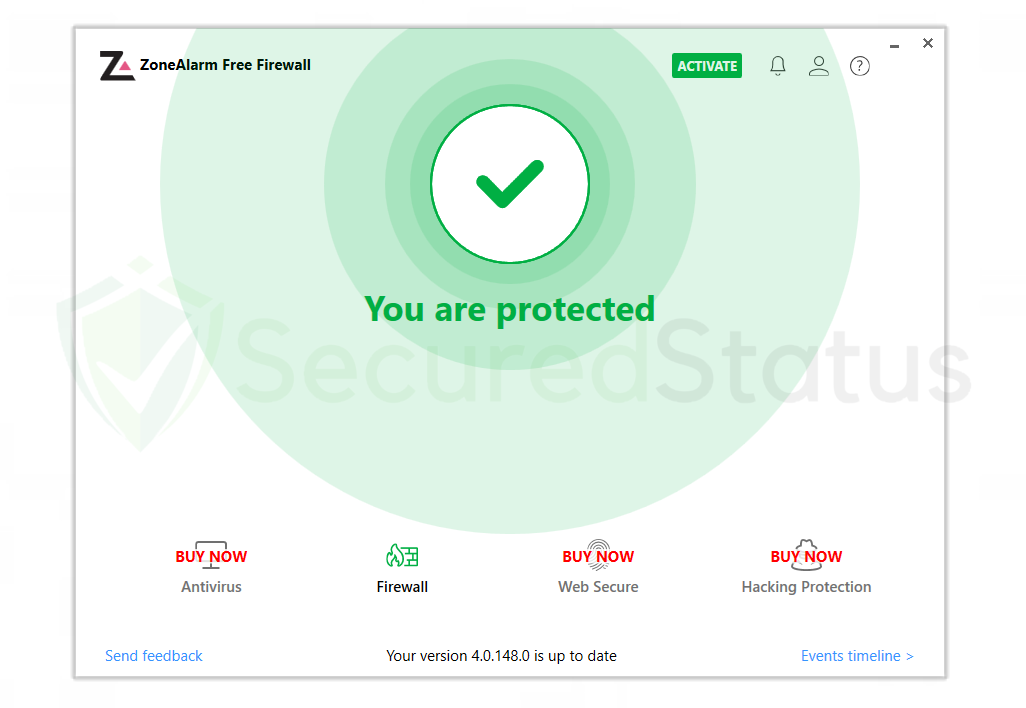
You can also opt for ZoneAlarm Free Firewall as your first line of defense between your device and the internet. The program safeguards your network and blocks any dangers, and you can use the free version of it without paying anything.
It provides a robust two-way protection solution that guards against spyware from disclosing your data online while also hiding your PC from nefarious hackers.
With its cutting-edge anti-bot protection, it also protects your computer from automated cyberattacks in real-time.
Additionally, it protects your computer against spam, dubious websites, and many others. Lastly, it provides real-time defense against automated cyberattacks with its cutting-edge anti-bot security.
Bottom Line
Always make sure that your device is protected against sneaky exploits and stealthy cyberattacks. While taking precautions and avoiding dubious websites are crucial, having a solid line of defense is essential to ensuring the security of your network and data.
If you experience another malware issue, please visit our website to find a solution for your problem or get in touch with us, and SecuredStatus will be happy to assist you once again.