Trojan:Win32/Dynamer!rfn (Dynamer Trojan)
Trojan:Win32/Dynamer!rfn can be accurately categorized as a trojan-downloader. This kind of malicious software aims at bringing other malware strains to your system. Additionally, it collects certain information about the system and the user.
Trojan:Win32/Dynamer!rfn functions as a downloader for other viruses, creating a favorable environment for incoming malware. It alters multiple system configurations, often targeting networking settings and Microsoft Defender. Modifying networking settings can result in difficulties connecting to certain websites or servers. While disabling Windows Defender is more noticeable, many users do not utilize this antivirus tool. Consequently, the likelihood of the virus’s activity remaining undetected until additional malware is downloaded is significantly increased.
Trojan:Win32/Dynamer!rfn: list of activities
These modifications can be as complies with:
- Executable code extraction.Cybercriminals frequently employ binary packers to impede reverse-engineering of malicious code by malware analysts. A packer is a tool that compresses, encrypts, and alters the format of a malicious file. In certain cases, packers may serve legitimate purposes, such as protecting a program against cracking or unauthorized duplication.
- Creates RWX memory.A security trick with memory regions allows an attacker to fill a buffer with a shellcode and then execute it. Filling a buffer with a shellcode isn’t a big deal. It’s just data. The problem arises when the attacker can control the instruction pointer (EIP), usually by corrupting a function’s stack frame using a stack-based buffer overflow and then changing the flow of execution by assigning this pointer to the address of the shellcode.
- Unconventionial language used in binary resources: Nepali;
- The binary likely contains encrypted or compressed data.In this case, encryption hides virus code from antiviruses and virus analysts.
- Queries information on disks, possibly for anti-virtualization.Since VMs share the same disk space, so it is expected that they won’t be getting as much space as an application running on
native hardware will have access to. - Network activity detected but not expressed in API logs.Microsoft built an API solution into its Windows operating system. It reveals network activity for all apps and programs that ran on the computer in the past 30 days. This malware hides network activity.
- Anomalous binary characteristics.This is a way of hiding virus code from antiviruses and virus analysts.
Trojan:Win32/Dynamer injection ways
The most common channels through which Trojan:Win32/Dynamer!rfn Ransomware Trojans are injected are:
- Through email spamming
- With malvertising
- As a part of software bundle
Email spamming became a prevalent malware distribution method since the users do not raise suspicion on notifications from DHL or Amazon about the incoming delivery. However, it is quite easy to distinguish the malevolent email from the original one. One which is sent by cybercriminals has a strange sender address – something like [email protected]. Simultaneously, the original email address has a specific domain name (@amazon.com or @dhl.us) and can also be seen on the official website in the “Contact us” tab.
Malicious advertisements on the web, however, is an old-timer of malware distribution. And the advice to stop clicking the blinking advertisements on untrustworthy websites exists as long as the ads on the Internet. You can also install ad-blocking plugins for your web browser – they will deal with any ads. However, if they are generated by adware already present on your PC, ad blockers will be useless.
Software bundling is a widespread practice among virus developers. Users who hack the programs to make them usable without purchasing a license approve any offer to include another program in the pack because they are gaining money in such a way. Check precisely the installation window for signs like “Advanced installation settings” or so. The ability to switch off the malware installation often hides under such items.
Trojan:Win32/Dynamer!rfn visual effects of presence.
In different edges of the world, victims of the Dynamer!rfn say about different signs of virus activity. Nonetheless, the common sign of the fact that criminals hijacked your PC with the use of a backdoor is that it lives its own life – mouse pointer moves without any mouse move, windows appear and close autonomously; your browser may start searching for something while you are sitting in front of the monitor with your hands off the input devices.
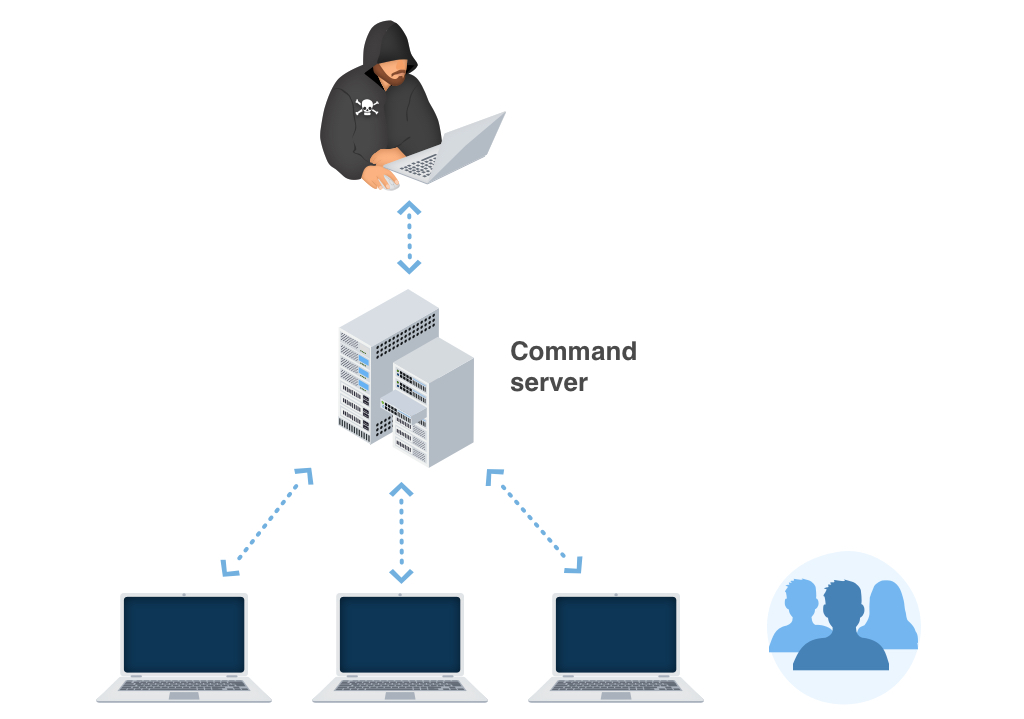
As I mentioned before, Trojan:Win32/Dynamer!rfn downloader makes several changes to the system configurations. It disables the Microsoft Defender – the embedded anti-malware solution for Windows. A lot of users do not make use of third-party antivirus programs because of the Defender’s availability. But the fact that it can be disabled in several clicks through the Group Policies settings creates a big risk.
Another thing changed by this Trojan virus is networking settings. Exactly, the thing which became changed is the HOSTS file. That file contains DNS settings for specific websites. Regarding the Dynamer!rfn activity, several additional entries have been added. These entries allow the virus to connect to malware distributors’ control servers and get the other viruses. Malware can also block the connection to different anti-malware forums and same-themed sites to prevent searching the malware removal guide.
Technical details
Trojan:Win32/Dynamer!rfn also known as:
| GridinSoft | Trojan.Ransom.Gen |
| MicroWorld-eScan | Trojan.GenericKD.42117995 |
| CAT-QuickHeal | Ransom.Stop.MP4 |
| McAfee | GenericRXJH-YA!3A23F339D858 |
| Sangfor | Malware |
| CrowdStrike | win/malicious_confidence_100% (W) |
| BitDefender | Trojan.GenericKD.42117995 |
| Arcabit | Trojan.Generic.D282AB6B |
| Cyren | W32/Trojan.JNIZ-0820 |
| Symantec | ML.Attribute.HighConfidence |
| ESET-NOD32 | a variant of Win32/GenKryptik.EAFW |
| APEX | Malicious |
| Paloalto | generic.ml |
| Kaspersky | not-a-virus:NetTool.Win32.TorTool.ama |
| Rising | Downloader.Dofoil!8.322 (TFE:6:qFwI1sROWJO) |
| Endgame | malicious (high confidence) |
| Emsisoft | Trojan.GenericKD.42117995 (B) |
| Invincea | heuristic |
| McAfee-GW-Edition | BehavesLike.Win32.Generic.gc |
| Fortinet | W32/GenKryptik.EAFW!tr |
| FireEye | Generic.mg.3a23f339d858b6a7 |
| Sophos | Generic PUA EB (PUA) |
| Ikarus | Ransom.Win32.Shade |
| Webroot | W32.Adware.Installcore |
| MAX | malware (ai score=85) |
| Microsoft | Trojan:Win32/Dynamer!rfn |
| ZoneAlarm | not-a-virus:NetTool.Win32.TorTool.ama |
| AhnLab-V3 | Trojan/Win32.MalPe.R303789 |
| Ad-Aware | Trojan.GenericKD.42117995 |
| Malwarebytes | Trojan.MalPack.GS |
| Panda | Trj/GdSda.A |
| SentinelOne | DFI – Malicious PE |
| GData | Trojan.GenericKD.42117995 |
| BitDefenderTheta | Gen:NN.ZexaF.33550.BCW@a852RDdG |
| AVG | FileRepMalware |
| Cybereason | malicious.362d35 |
| Avast | FileRepMalware |
| Qihoo-360 | HEUR/QVM10.2.E643.Malware.Gen |
How to remove Trojan:Win32/Dynamer!rfn virus?
Unwanted application has ofter come with other viruses and spyware. These threats can steal account credentials or crypt your documents for ransom.
Reasons why I would recommend GridinSoft 1
The is an excellent way to deal with recognizing and removing threats – using Gridinsoft Anti-Malware. This program will scan your PC, find and neutralize all suspicious processes. 2 .
Download GridinSoft Anti-Malware.
You can download GridinSoft Anti-Malware by clicking the button below:
Run the setup file.
When the setup file has finished downloading, double-click on the install-antimalware-fix.exe file to install GridinSoft Anti-Malware on your system.
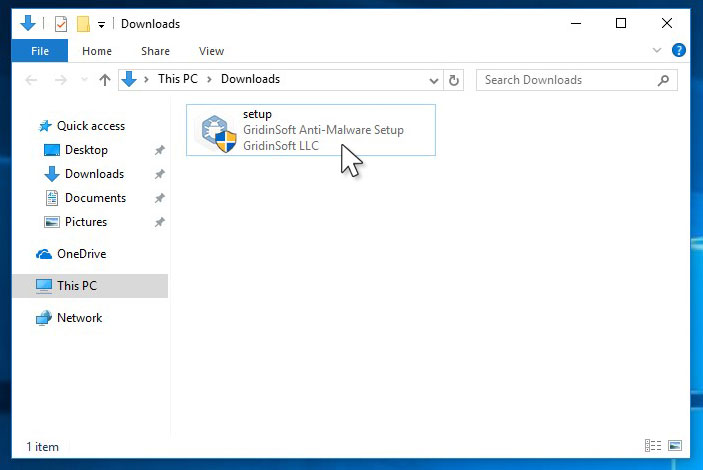
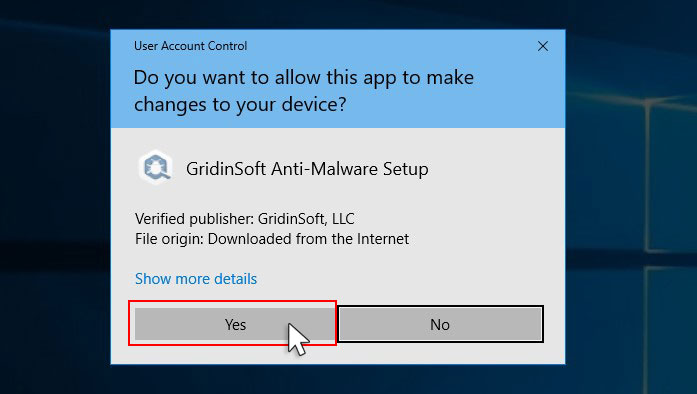
An User Account Control asking you about to allow GridinSoft Anti-Malware to make changes to your device. So, you should click “Yes” to continue with the installation.
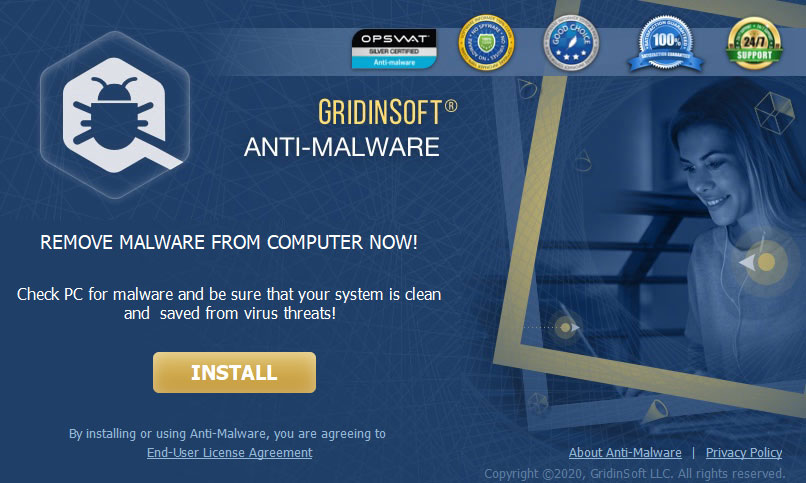
Press “Install” button.
Once installed, Anti-Malware will automatically run.
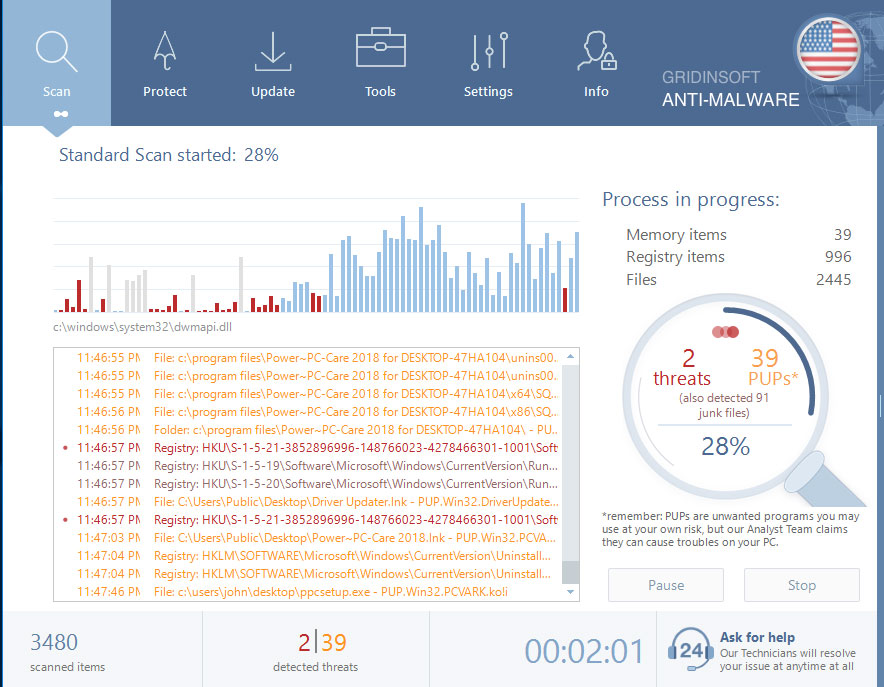
Wait for the Anti-Malware scan to complete.
GridinSoft Anti-Malware will automatically scan your system for Trojan:Win32/Dynamer!rfn files and other malicious programs. This process can take 20-30 minutes, so I suggest you periodically check on the status of the scan process.
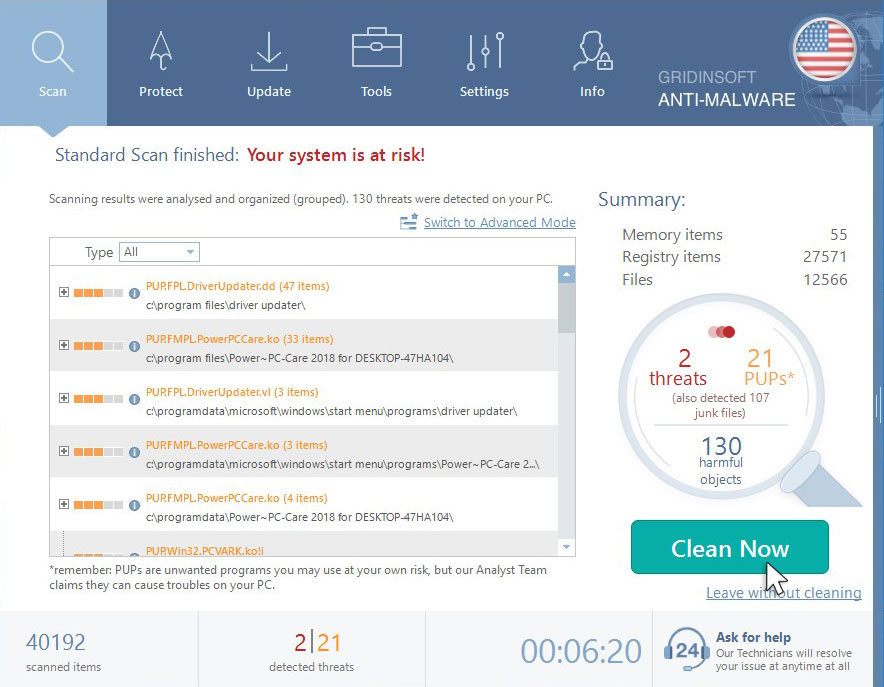
Click on “Clean Now”.
When the scan has finished, you will see the list of infections that GridinSoft Anti-Malware has detected. To remove them, click the “Clean Now” button in the right corner.
Are Your Protected?
GridinSoft Anti-Malware will scan and clean your PC for free in the trial period. The free version offer real-time protection for first 2 days. If you want to be fully protected at all times – I can recommended you to purchase a full version:
Full version of GridinSoft Anti-Malware
If the guide doesn’t help you remove Trojan:Win32/Dynamer!rfn, you can always ask me in the comments to get help.
Является ли "Win32/Dynamer!ac" действительно опасным вирусом а не кряком/таблэткой от программы или утилиты?
 Тема закрыта
#1 Nicholas7779
Скачал я сборку «Windows 10 от SmokieBlahBlah 17.07.17» и при проверке на вирусное ПО антивирус нашёл «троян» Win32/Dynamer!ac в папке: sources\boot.wim->\Program Files\Password\ResetWinPassword\rwp.exe->(7zSfx)->RunRWP.exe
Автор писал, что все антивирусные программы реагируют так на кряки/таблэтки и т. д, это я знаю, но на самом то деле что? Это липовый троян который не опасен?
Я лишь хотел уточнить, настолько ли этот вирус опасен, ибо антивирусные программы могут (как правило) воспринимать любой взломщик программы за виурс, ибо этот вирус, как правило, является Кряком или Таблэткой.
Ибо Скачивал я как-то Action! с проверенного трекера, там был отдельный .exe кряк-генератор ключей, так он тоже его посчитал за этот самый Дунамериак, при удаление которого удалился и сам этот .exe кряк.
К слову, этот Action! я качал около года назад, за это время никакой активности вируса не замечал, а я человек опытный в этом деле, за 6 лет у меня из вирусов был только он и ещё один троян. Обычно я сижу без антивирусной утилиты.
Но я так-же не отрицаю того факта, что это самый что ни на есть троян для кражи информации.
Trojan win32 dynamer rfn что это
Stumped on a tech problem? Ask the community and try to help others with their problems as well. Note: Reddit is dying due to terrible leadership from CEO /u/spez. Please use our Discord server instead of supporting a company that acts against its users and unpaid moderators.
So Today I downloaded some cracked games (all from trusted sources) and for safety I scanned all of them using Windows defender and after the scan I got this Trojan Alert from windows defender and after check the files using virustotal I got similar results. What should I do?
Троян использует «режим Бога» Windows, чтобы спрятаться в системе
 Как известно, в операционной системе Windows Vista, 7, 8 и 10 есть своеобразная пасхалка — GodMode (режим Бога). Начиная с версии Vista можно создать папку со специфическим именем, которая перенаправляет на настройки Windows или служебные папки, такие как «Панель управления», «Компьютер», «Принтеры» и проч.
Например, если создать на рабочем столе папку с названием GodMode. (вместо GodMode можно указать любые символы), то внутри будут отображаться все настройки, в том числе и те, которые не включены в меню «Панели управления» или «Параметры»: скриншот.
Очень удобная фича для управления настройками в системе и для системного администрирования.
К сожалению, режим Бога используют не только сисадмины, но и авторы вирусов.
Специалисты из антивирусной компании McAfee Labs рассказывают о трояне Dynamer, который использует режим Бога, чтобы скрыться от обнаружения в системе.
Dynamer при установке записывает свои файлы в одну из таких папок внутри %AppData%. В реестре создаётся ключ, который сохраняется после перезагрузки, запуская каждый раз бинарник зловреда.
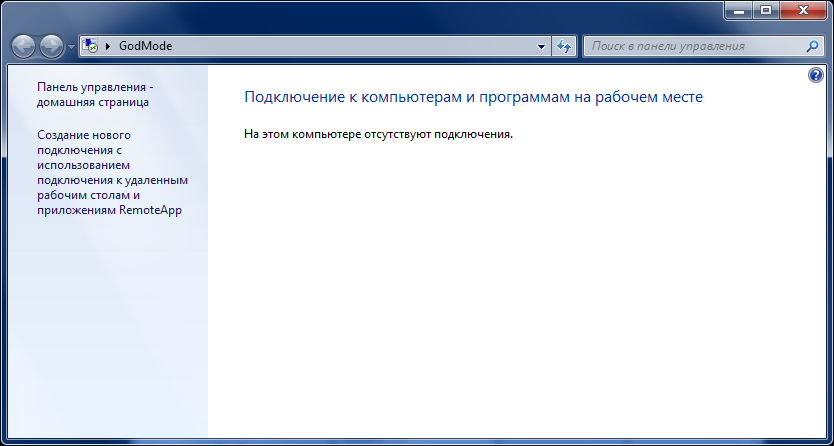
Таким образом, исполняемый файл нормально запускается по команде из реестра, но вручную зайти в эту папку нельзя: как указано в списке выше, папка <241D7C96-F8BF-4F85-B01F-E2B043341A4B>работает как ярлык на настройки «Подключение к компьютерам и программам на рабочем месте» (RemoteApp and Desktop Connections).
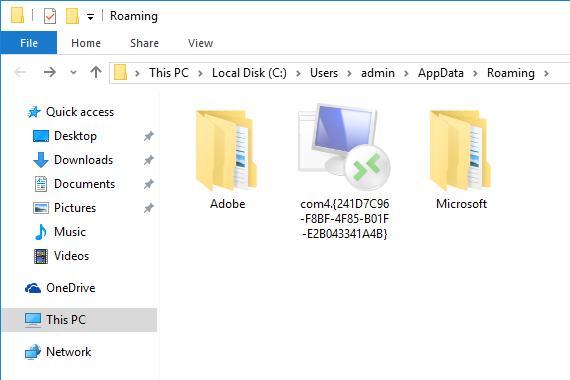
Вот содержимое папки, если открыть её в проводнике.
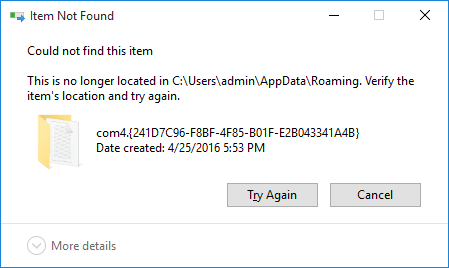
Более того, авторы трояна добавили к названию папки «com4.», так что Windows считает папку аппаратным устройством. Проводник Windows не может удалить папку с таким названием.
Аналогично, удаление невозможно из консоли.
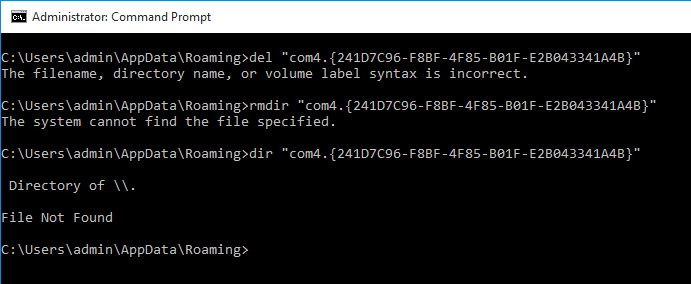
Нормальные антивирусы обходят этот трюк вирусописателей. Чтобы удалить папку вручную, нужно запустить из консоли следующую команду.
Троян Dynamer впервые обнаружен несколько лет назад, но Microsoft до сих пор считает его «серьёзной угрозой» для пользователей Windows.
В качестве бонуса.
Список имён папок (GUID) в режиме Бога для быстрого доступа к отдельным настройкам Windows