PUA:Win32/Puwaders.C!ml — Puwaders PUA Removal
PUA:Win32/Puwaders.C!ml is a detection name used by Microsoft Defender Antivirus to identify a potentially unwanted application (PUA) known as Puwaders. PUAs are software programs that are not classified as outright malware but may exhibit behaviors that users find undesirable or potentially harmful. These applications often come bundled with other software or may be downloaded unintentionally by users.
Puwaders is categorized as a PUA because it may display excessive advertisements, redirect web browsers to unwanted sites, collect user data without proper consent, or use deceptive tactics to trick users into installing other software. While it may not cause direct harm to the system like typical malware, it can negatively impact the user’s browsing experience and privacy.
It is essential to be cautious when installing software and to download applications only from trusted sources. Additionally, using Gridinsoft Anti-malware can help detect and remove potential PUAs like Puwaders to ensure a safer and more secure computing environment.
What is PUA:Win32/Puwaders.C!ml?
If your computer is alerted by Windows Defender about the presence of the PUA:Win32/Puwaders.C!ml virus, do not ignore it. Take immediate action to safeguard your device.
These virus threats often infiltrate through spam emails, infected websites, or by clicking on links in emails. Once installed on your system, PUA:Win32/Puwaders.C!ml spreads through Windows System files, granting it access to all the information on your computer and even allowing it to take control.
Windows Defender will continue to alert you about the malware until you address the issue promptly. It is crucial to remove such threats from your computer to ensure its safety.
Here are some symptoms experienced by users whose devices are infected with PUA:Win32/Puwaders.C!ml:
- Sudden disruptions in internet connection and application performance.
- Computer freezes or experiences slowdowns.
- Difficulty in opening documents or accessing files.
- Unusual popup ads appearing online or while browsing.
- Increased overheating and CPU usage.
What is PUA:Win32/Puwaders.C!ml detection mean?
The PUA:Win32/Puwaders.C!ml detection you can see in the lower right side is shown to you by Microsoft Defender. That anti-malware application is quite OK at scanning, but prone to be mainly unstable. It is unprotected to malware attacks, it has a glitchy interface and problematic malware removal features. Thus, the pop-up which says about the Puwaders is simply a notification that Defender has actually found it. To remove it, you will likely need to make use of a separate anti-malware program.
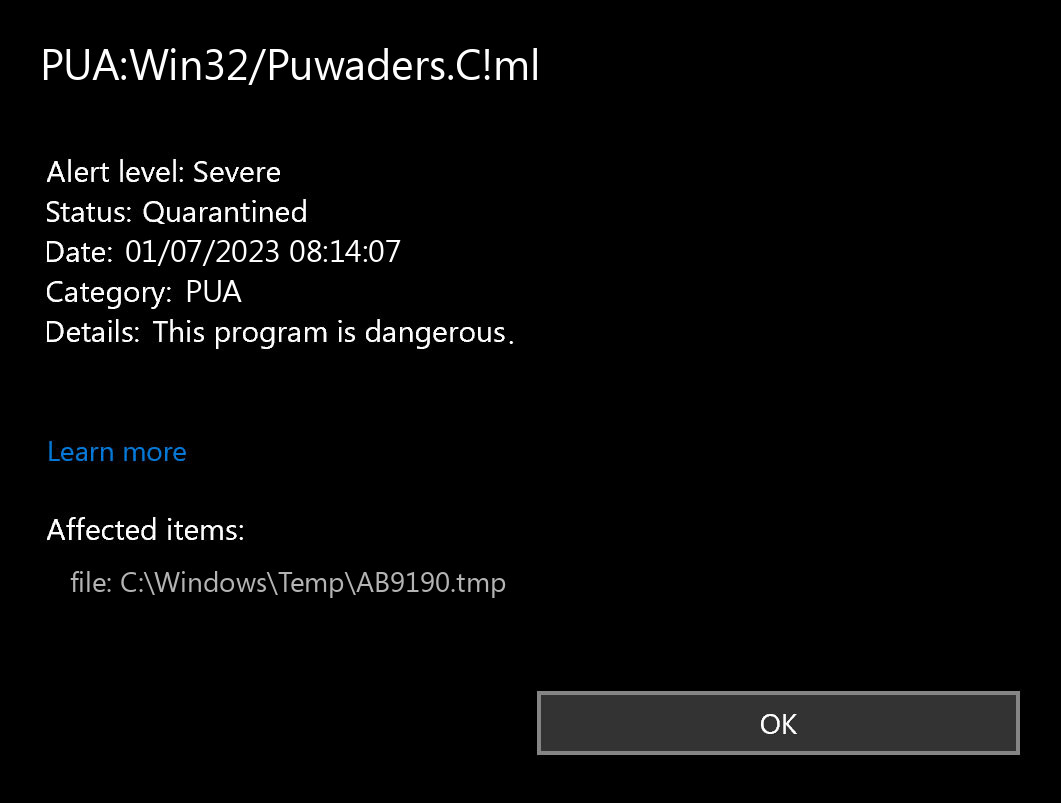
Microsoft Defender: “PUA:Win32/Puwaders.C!ml”
PUA:Win32/Puwaders.C!ml unwanted program is a case in point of PUA, which are pretty common nowadays. Being free to use, it can offer you “the extended functions” for the additional payment. Some instances of this program type can have no real functions whatsoever – just the shell with the colorful interface. You can see it advertised as a system optimization software, driver updater or torrent downloadings tracker. This or another way it does not bring you any kind of real capability, exposing you to risk instead.
Detections like these are highly dangerous as they can be used to compromise other users’ privacy credentials and financial information.
If you suspect that your computer is affected by this specific virus, it is crucial to remove it immediately.
The detection name format aligns with how Windows Defender describes its discovered threats, making it clear that Windows Defender identified the PUA:Win32/Puwaders.C!ml on your computer.
Typically, Windows Defender is sufficient to remove the detected threat, requiring only a click on the quarantine button to initiate the removal process.
However, in certain circumstances where Windows Defender is unable to eliminate the malware, you may opt to use Gridinsoft Anti-malware to remove it effectively.
Unwanted Program Summary:
Is PUA:Win32/Puwaders.C!ml dangerous?
I have already specified that PUA:Win32/Puwaders.C!ml PUA is not as trustworthy as it pretends to be. The “legitimate and effective” tool can abruptly unveil itself as a downloader trojan, spyware, backdoor, or coin miner malware. And you can never forecast what to look for even from separate variants of Puwaders unwanted program. That still does not say that you need to panic – possibly, this nasty thing has not succeeded to do bad things to your computer.
The particular damage to your system may be created not just because of the malware injection. A considerable share of suspicious programs, like the Puwaders app is, is just badly developed. Potentially, their actions are fairly useful than pointless if done on particular system setups, but not on each one. That’s how an uncomplicated system optimization program can cause disorder with continuous BSODs on your system. Any interruptions to the system registry are dangerous, and they are a lot more risky if performed with such programs.
How did I get this virus?
It is hard to line the origins of malware on your PC. Nowadays, things are mixed up, and spreading methods utilized by adware 5 years ago can be used by spyware nowadays. However, if we abstract from the exact distribution tactic and will think of why it works, the explanation will be really uncomplicated – low level of cybersecurity understanding. Individuals click on ads on weird sites, open the pop-ups they get in their browsers, call the “Microsoft tech support” assuming that the weird banner that says about malware is true. It is very important to know what is legitimate – to prevent misunderstandings when trying to find out a virus.
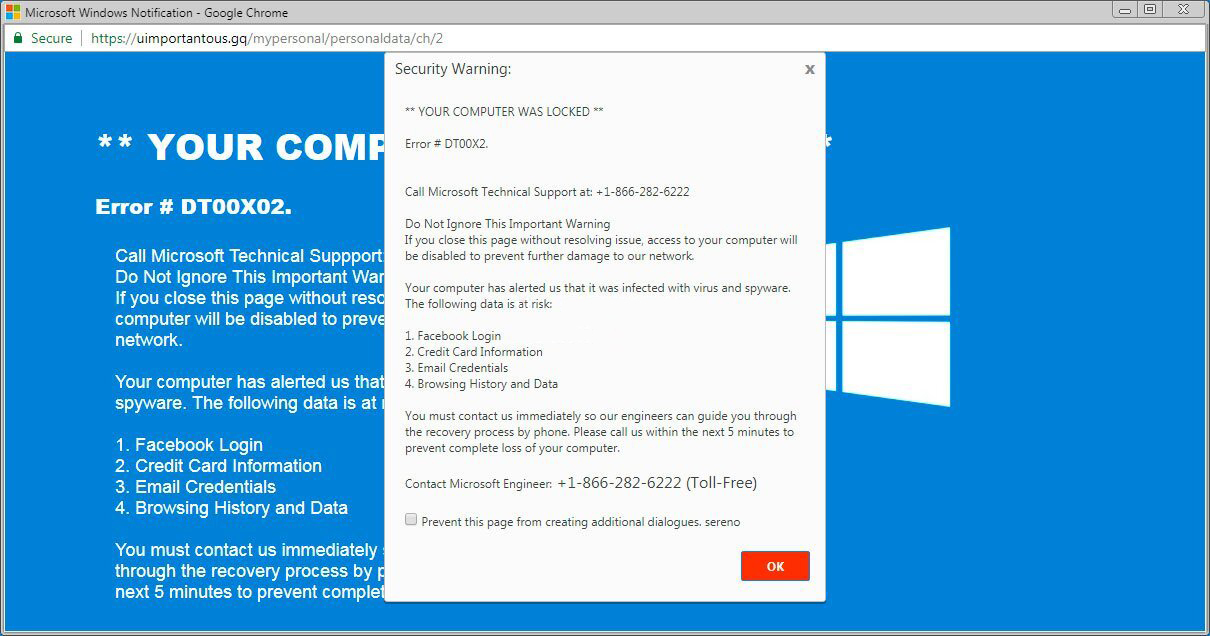
The example of Microsoft Tech support scam banner
Nowadays, there are two of the most widespread tactics of malware distribution – bait e-mails and injection into a hacked program. While the first one is not so easy to avoid – you must know a lot to understand a counterfeit – the 2nd one is easy to handle: just don’t use cracked applications. Torrent-trackers and various other sources of “free” applications (which are, in fact, paid, but with a disabled license checking) are really a giveaway place of malware. And PUA:Win32/Puwaders.C!ml is simply amongst them.
How to remove the PUA:Win32/Puwaders.C!ml from my PC?
PUA:Win32/Puwaders.C!ml malware is very hard to delete by hand. It stores its documents in numerous places throughout the disk, and can restore itself from one of the elements. Furthermore, a number of modifications in the windows registry, networking configurations and Group Policies are pretty hard to locate and revert to the initial. It is far better to use a special tool – exactly, an anti-malware program. GridinSoft Anti-Malware will definitely fit the best for malware elimination objectives.
Why GridinSoft Anti-Malware? It is pretty lightweight and has its detection databases updated practically every hour. Moreover, it does not have such problems and weakness as Microsoft Defender does. The combination of these details makes GridinSoft Anti-Malware ideal for clearing away malware of any form.
Как удалить PUA:Win32/Puwaders.C!ml
Как удалить вирусный файл PUA:Win32/Puwaders.C!ml? PUA:Win32/Puwaders.C!ml — это тип файла, который заражает компьютеры. Он берет под свой контроль ваш компьютер, собирает информацию и даже может быть использован хакерами для получения доступа к вашей системе.
Если ваше антивирусное программное обеспечение обнаруживает наличие PUA:Win32/Puwaders.C!ml, это означает, что некоторые связанные файлы все еще остаются. Эти оставшиеся файлы, связанные с PUA:Win32/Puwaders.C!ml, следует удалить. Однако антивирусным программам часто не удается удалить все следы PUA:Win32/Puwaders.C!ml.
Вирус PUA:Win32/Puwaders.C!ml — это форма кода, созданная для заражения компьютеров или сетевых систем, вызывающая повреждение, сбой или кражу данных. Он может распространяться с одного компьютера на другой. Может даже повлиять на целые сети. Компьютерные вирусы могут передаваться через устройства хранения загрузок, такие как USB-накопители, и даже через вложения электронной почты. Со временем эти вредоносные угрозы становятся все более изощренными, что усложняет пользователям обнаружение и защиту своих систем от атак. Существуют различные типы компьютерных вирусов, каждый из которых обладает своими характеристиками и возможностями, которые могут привести к серьезным последствиям при заражении любого устройства или системы.
Пользователи должны осознавать риски, связанные с компьютерными вирусами, и принимать меры для защиты своих данных от этих вредоносных вторжений.
Компьютерный вирус — это любое программное обеспечение, намеренно созданное для заражения компьютеров, причиняющее ущерб данным или нарушающее нормальную работу.
Компьютерные вирусы могут распространяться через сети и съемные носители, например USB-накопители. Их также можно передавать в виде вложений электронной почты. Некоторые вирусы даже могут самовоспроизводиться и заражать компьютеры без какого-либо вмешательства человека. Существуют типы компьютерных вирусов и вредоносного программного обеспечения, включая червей, троянов и других форм вредоносного ПО. Эти гнусные сущности часто созданы для того, чтобы нанести ущерб или нарушить работу компьютерных систем и сетей, похитить информацию или испортить данные. Вирусы и другие формы вредоносного ПО могут распространяться через файлы, веб-сайты, вложения электронной почты и другие форматы исполняемых кодов.
Способы распространения компьютерных вирусов могут различаться в зависимости от типа вируса и настроек безопасности скомпрометированного устройства. Многие программы распространяются через сообщения электронной почты, веб-сайты или файлы различных форматов. Вложения электронной почты служат вектором распространения компьютерных вирусов; их можно либо прикрепить непосредственно к электронному письму, либо внедрить в его содержимое. Предположим, вложение электронного письма заражено вирусом. В этом случае он может заразить не только устройство, на котором он открыт, но и любые другие устройства, на которые копируется это зараженное вложение. Кроме того, компьютерные вирусы также могут распространяться через веб-сайты, на которых размещено программное обеспечение, например платформы социальных сетей, распространяющие поддельные видео, изображения или другой вводящий в заблуждение контент.
Веб-сайты также могут содержать код, который может заразить устройство, когда пользователь нажимает на ссылку или посещает сайт.
Симптомы заражения сильно зависят от типа вируса, заразившего устройство. Общие симптомы инфекции включают следующее:
Что такое вирус “PUABundler:Win32”? Как это удалить?
Защитник Windows мог предупредить вас о вирусной угрозе, обнаруженной на вашем компьютере, указывая на наличие определенного вредоносного ПО, имя которого начинается с «PUABundler:Win32». Эти оповещения служат предупреждениями Windows, уведомляющими вас об обнаруженном потенциально опасном содержимом. Если Защитник Windows уведомляет вас о вредоносном вирусе в вашей системе, очень важно не игнорировать его, так как он может нанести серьезный ущерб вашей системе.
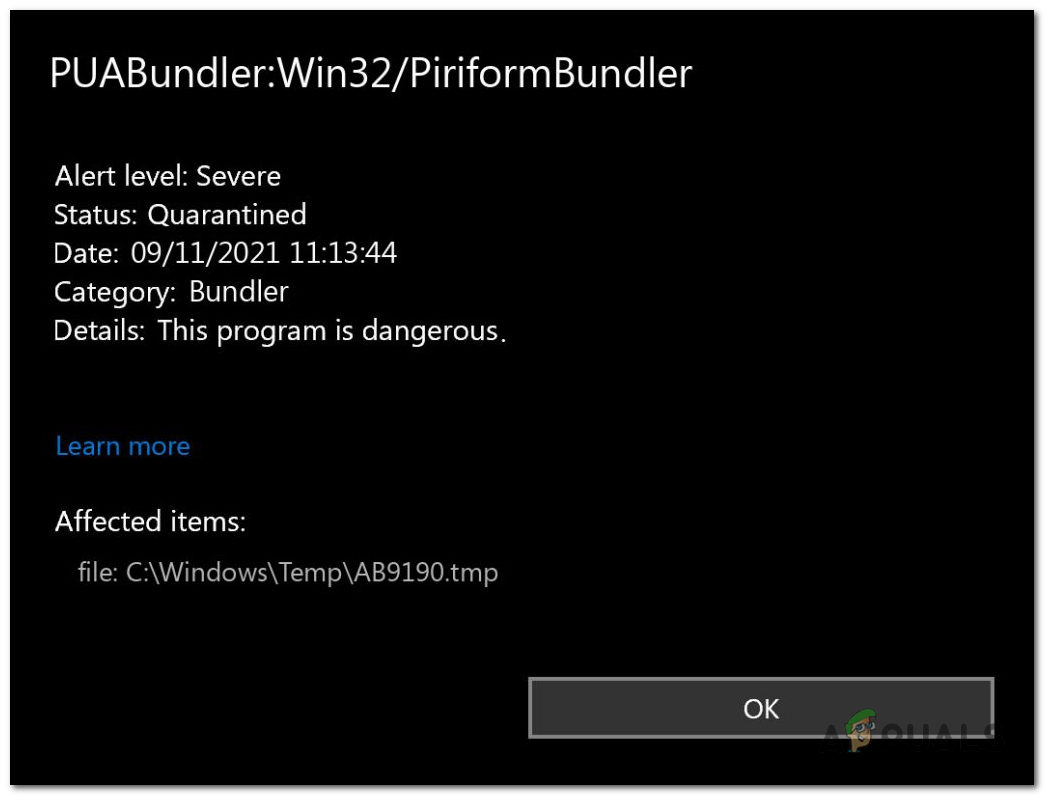
Вирус «PUABundler:Win32/PiriformBundler», обнаруженный системой безопасности Windows.
Программы для Windows, мобильные приложения, игры — ВСЁ БЕСПЛАТНО, в нашем закрытом телеграмм канале — Подписывайтесь:)
Эти угрозы часто попадают в вашу систему через спам, зараженные веб-сайты или переходы по вредоносным ссылкам. Как только этот вирус установлен на вашем компьютере, он начинает распространяться через системные файлы Windows. Это позволяет вредоносным программам получить доступ ко всей информации на вашем компьютере и даже получить над ней контроль. Вирус может вызывать различные проблемы, в том числе:
- Неожиданные проблемы с подключением к Интернету и приложениями.
- Зависание или замедление работы компьютера.
- Проблемы с открытием документов или доступом к файлам.
- Во время работы в Интернете появляются необычные всплывающие окна с рекламой.
- Перегрев и высокая загрузка процессора.
Подобные обнаружения особенно опасны, поскольку их можно использовать для атаки на пользователей путем кражи их личных учетных данных, финансовой информации и многого другого. Если вы подозреваете, что ваше устройство заражено этим конкретным вирусом, крайне важно удалить его как можно скорее.
1. Запустите Windows в безопасном режиме с поддержкой сети.
Запуск в безопасном режиме имеет решающее значение, поскольку он позволяет запускать компьютер с минимальным количеством программ и драйверов. Это помогает, потому что останавливает запуск вируса при запуске компьютера, что облегчает его удаление. Чтобы войти в безопасный режим с поддержкой сети, выполните следующие действия:
- Откройте диалоговое окно запуска, одновременно нажав кнопку Windows + клавишу R на клавиатуре.
- Когда откроется окно запуска, введите «msconfig.exe» и нажмите клавишу ввода, чтобы открыть окно конфигурации системы Microsoft.
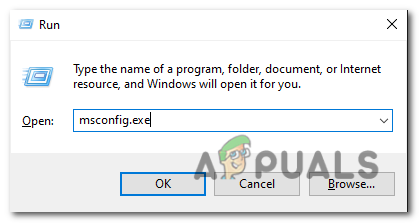 Откройте окно запуска и введите «msconfig.exe».
- После того, как откроется окно конфигурации системы, нажмите на вкладку «Boot». Установите флажок «Безопасная загрузка» и выберите параметр ниже, который указывает «Сеть». Нажмите «Применить».
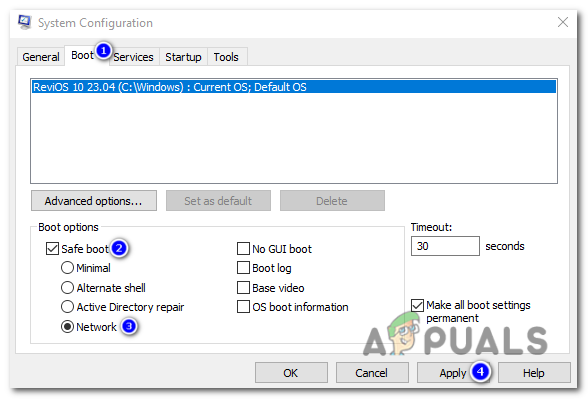 Когда откроется окно конфигурации системы, нажмите на вкладку «Boot». Установите флажок «Безопасная загрузка» и выберите параметр ниже, который указывает «Сеть». Нажмите «Применить».
- Перезагрузите компьютер, чтобы войти в безопасный режим.
- Перейдя в безопасный режим, вы можете перейти к следующему шагу — удалению вредоносного ПО из вашей компьютерной системы.
2. Использование Rkill для уничтожения вируса
RKill — это программа, разработанная BleepingComputer.com который направлен на прекращение всех известных вредоносных процессов. Его цель – позволить вашему обычному программному обеспечению безопасности работать и эффективно очищать ваш компьютер от инфекций. Когда RKill запускается, он завершает вредоносные процессы, исправляет неправильные ассоциации исполняемых файлов и исправляет политики, которые могут препятствовать использованию определенных инструментов. Чтобы загрузить и использовать Rkill, выполните следующие действия:
- Откройте веб-браузер и перейдите на официальная страница загрузки RKill.
- На странице загрузки найдите конкретную ссылку для загрузки с надписью «iExplore.exe» и нажмите на нее. Это переименованная версия RKill, которая может обходить определенные ограничения вредоносных программ.
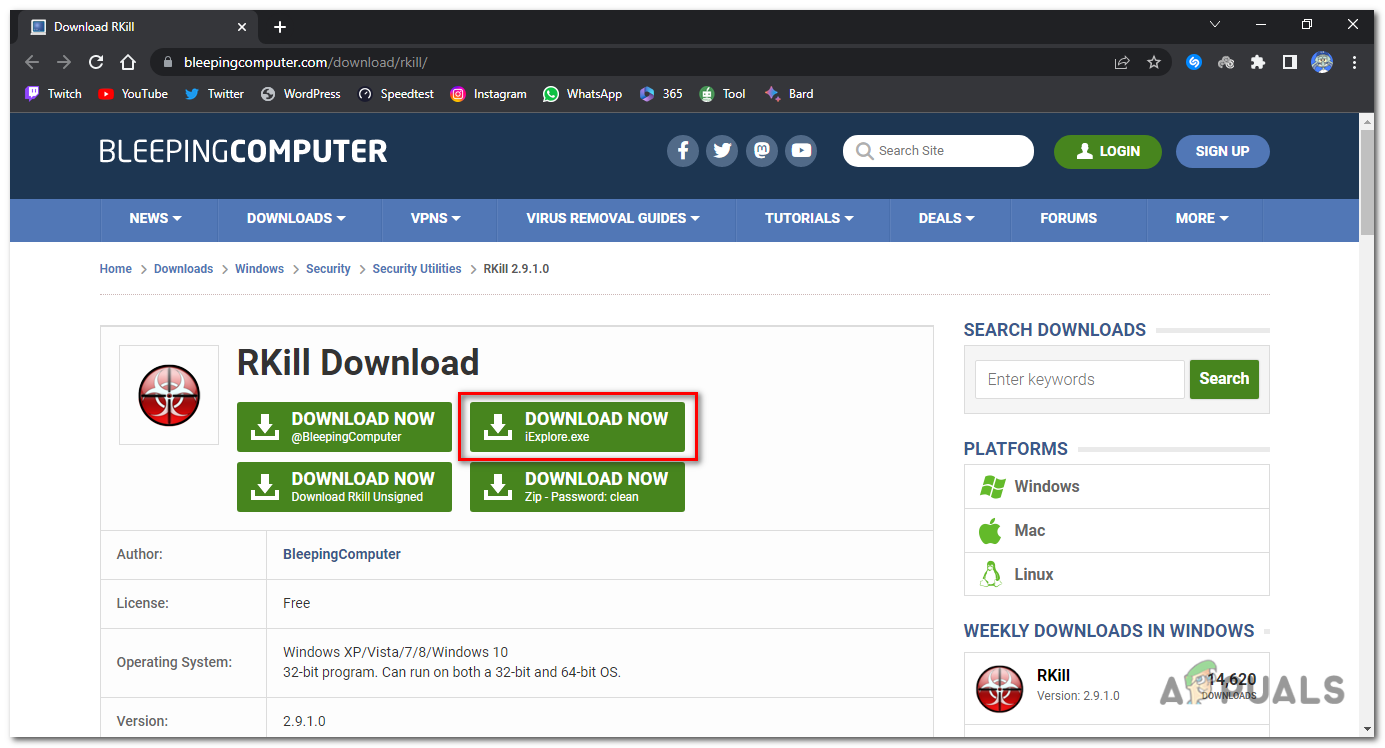 Нажмите на ссылку для скачивания с надписью «iExplore.exe».
- После завершения загрузки перейдите в папку, в которую браузер загрузил исполняемый файл RKill.
- Дважды щелкните исполняемый файл RKill (iExplore.exe), чтобы запустить его. Появится предупреждение, нажмите «Да» или «Выполнить», чтобы продолжить.
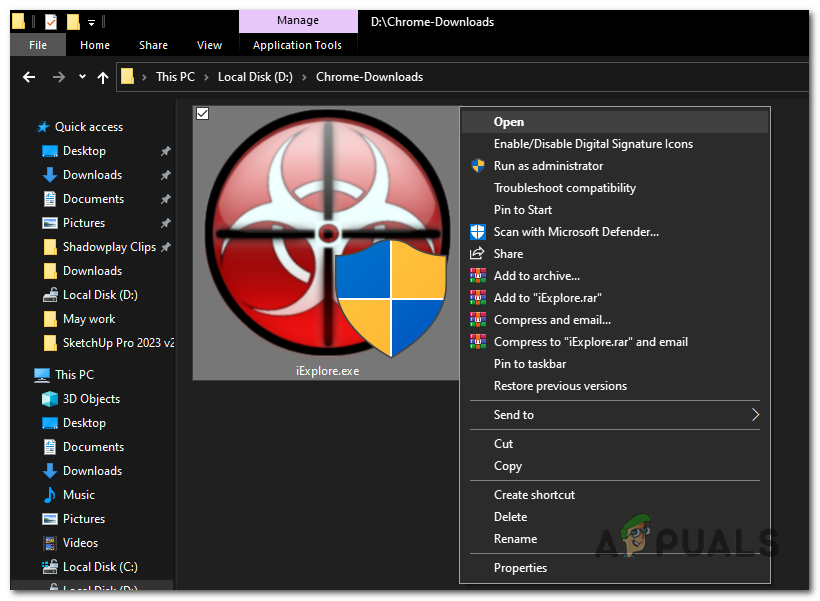 Дважды щелкните исполняемый файл RKill (iExplore.exe), чтобы запустить его.
- Теперь RKill начнет сканирование и завершение известных вредоносных процессов на вашем компьютере. Завершение процесса может занять некоторое время, и вы можете увидеть черное окно командной строки, отображающее ход выполнения.
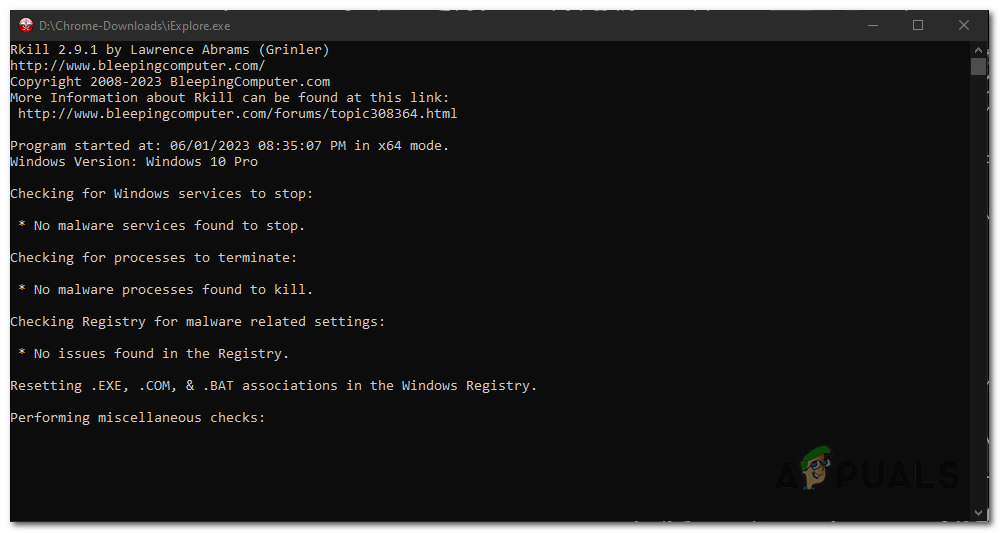 Теперь RKill начнет сканирование и завершение известных вредоносных процессов на вашем компьютере.
- После завершения работы RKill черное окно автоматически закроется, и будет создан файл журнала.
- В этот момент важно не перезагружать компьютер. Вместо этого перейдите к следующему шагу запуска полного сканирования системы.
3. Запустите полное сканирование системы
Выполнение полного сканирования системы с помощью Windows Security обнаружит местонахождение вирусного файла и удалит его с помощью встроенных антивирусных возможностей. Этот процесс прост, особенно если у вас не установлено какое-либо внешнее антивирусное программное обеспечение, поскольку безопасность Windows интегрирована в операционную систему Windows. Чтобы запустить полное сканирование системы, выполните следующие действия:
- Нажмите клавишу Windows, чтобы открыть меню «Пуск», введите «Безопасность Windows» в строке поиска и выберите приложение «Безопасность Windows» в результатах поиска.
- В приложении «Безопасность Windows» щелкните вкладку «Защита от вирусов и угроз», расположенную в левой части окна.
- На вкладке «Защита от вирусов и угроз» в разделе «Быстрое сканирование» нажмите «Параметры сканирования». На вкладке «Защита от вирусов и угроз» в разделе «Быстрое сканирование» нажмите «Параметры сканирования».
- Появится меню с различными параметрами сканирования. Выберите «Полное сканирование» из списка.
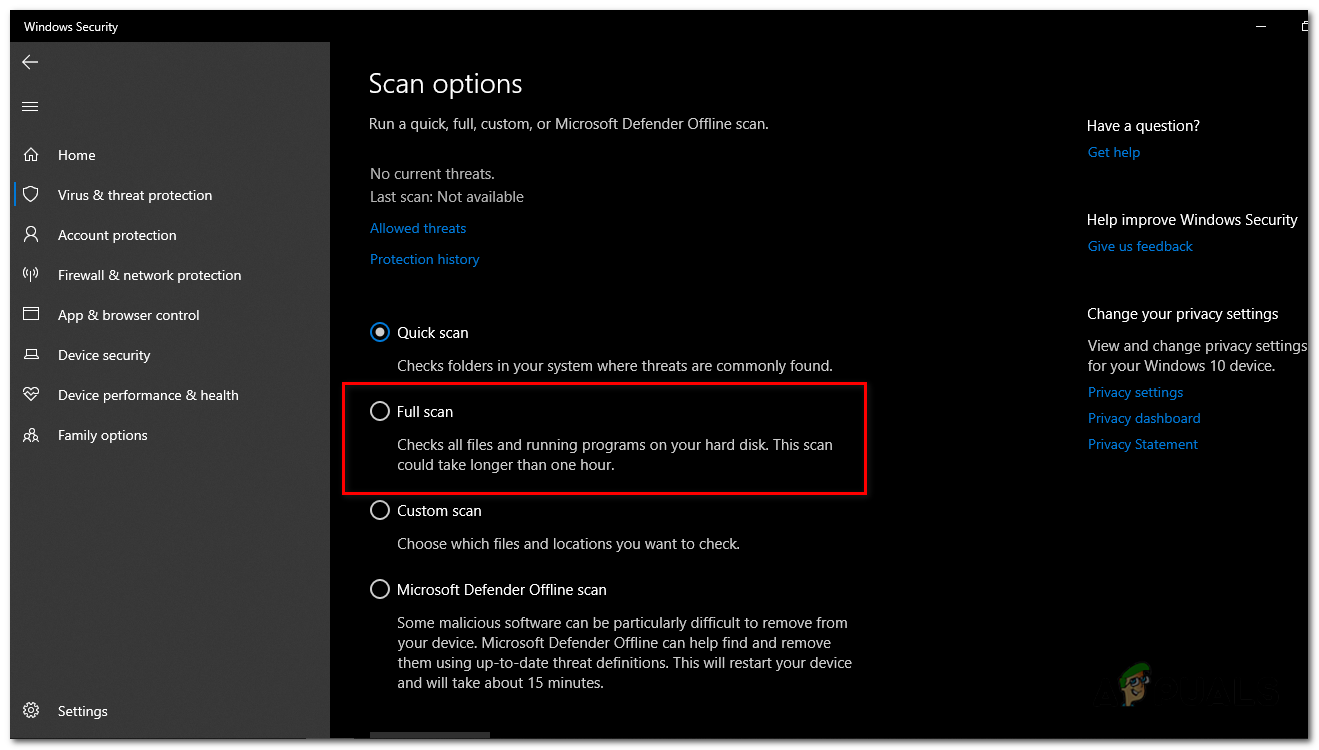 Появится меню с различными параметрами сканирования. Выберите «Полное сканирование» из списка.
- Нажмите кнопку «Сканировать сейчас», чтобы начать полное сканирование. Безопасность Windows теперь будет сканировать всю вашу систему на наличие вредоносных программ, включая вирус «PUABundler:Win32».
- Процесс сканирования может занять некоторое время, в зависимости от размера и скорости вашего накопителя и количества файлов в вашей системе. Вы можете следить за ходом сканирования на экране.
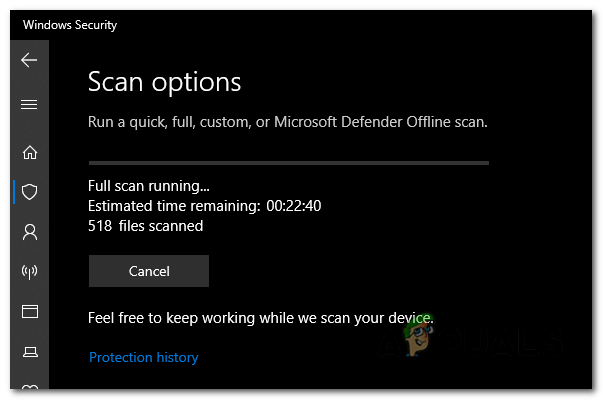 Вы можете следить за ходом сканирования на экране.
- После завершения сканирования Windows Security отобразит результаты. В нем будут перечислены все обнаруженные угрозы.
- Безопасность Windows предоставит варианты действий против обнаруженных угроз. Если обнаружен вирус PUABundler:Win32, следуйте инструкциям по его удалению или помещению в карантин.Если обнаружен вирус PUABundler:Win32, следуйте инструкциям по его удалению или помещению в карантин.
- В некоторых случаях Windows Security предложит перезагрузить компьютер, чтобы завершить процесс удаления. При появлении запроса сохраните свою работу и перезагрузите компьютер.
4. Использование антивируса Malwarebytes
Malwarebytes широко признан одним из самых популярных и эффективных антивирусных программ для Windows. Его репутация связана с его способностью успешно устранять различные типы вредоносных программ, которые другие программы могут не заметить. Самое приятное то, что Malwarebytes предлагает свои мощные функции бесплатно. Когда дело доходит до работы с зараженным устройством и обеспечения его чистоты, Malwarebytes неизменно доступен в качестве бесплатного и незаменимого инструмента в продолжающейся борьбе с вредоносным ПО. Чтобы загрузить и использовать Malwarebytes, выполните следующие действия:
- Откройте браузер и откройте Страница загрузки Malwarebytes.
- Нажмите на кнопку «Free Dowload», программа начнет загрузку.
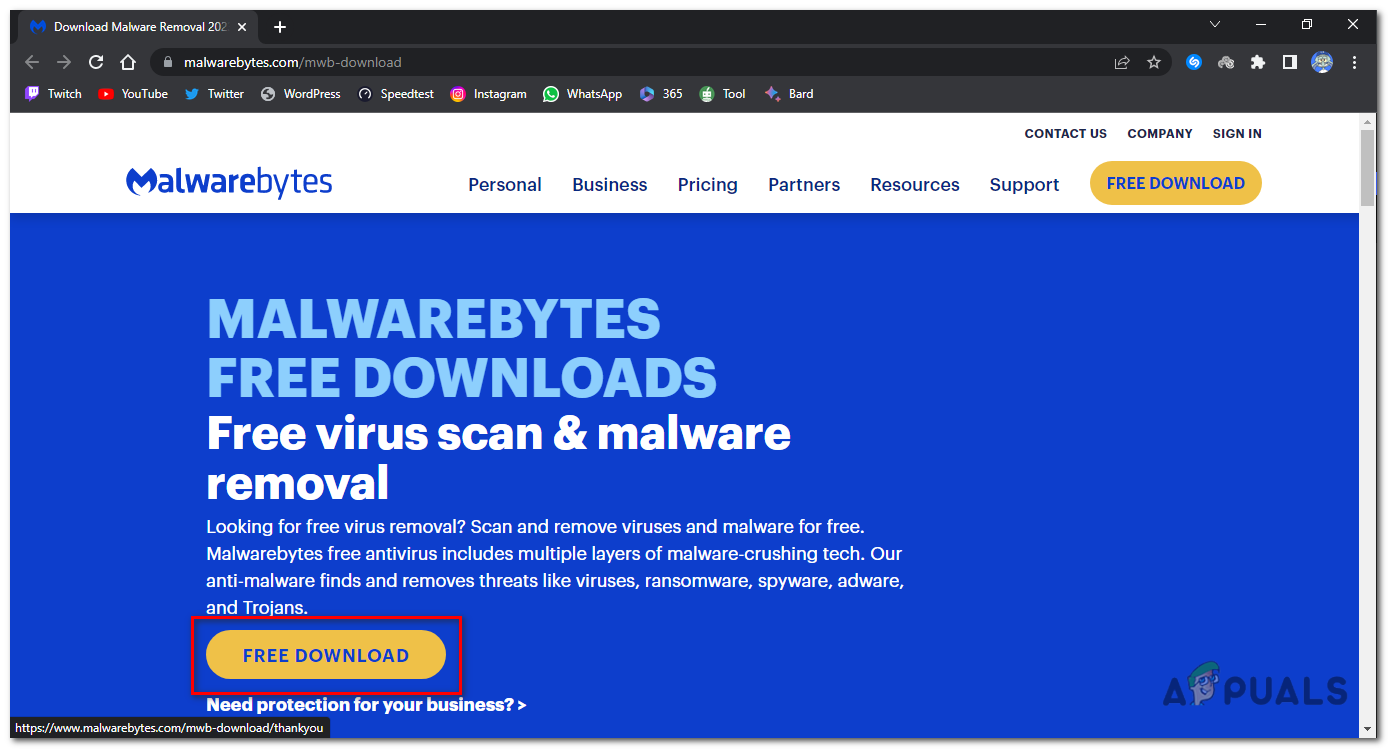 Нажмите на кнопку «Free Dowload», программа начнет загрузку.
- После завершения загрузки найдите загруженный файл (обычно в папке «Загрузки») и дважды щелкните файл «MBSetup», чтобы начать установку Malwarebytes.
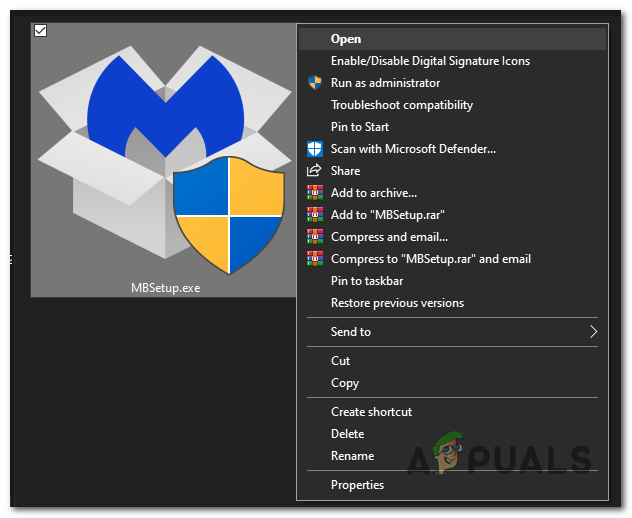 дважды щелкните файл «MBSetup», чтобы начать установку Malwarebytes.
- Следуйте инструкциям на экране, представленным мастером установки Malwarebytes, чтобы завершить установку. Когда вас попросят выбрать тип компьютера, выберите «Персональный компьютер» или «Рабочий компьютер». Затем нажмите «Далее», чтобы продолжить.
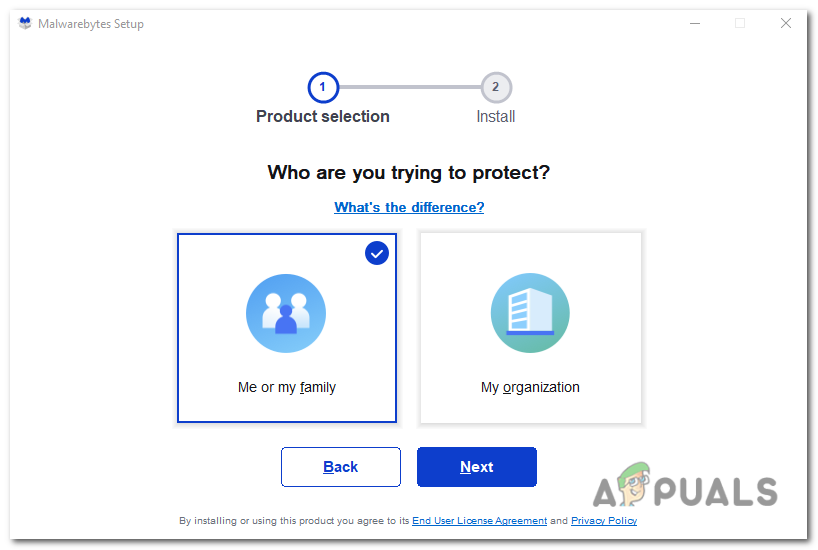 выберите «Персональный компьютер» или «Рабочий компьютер». Затем нажмите «Установить», чтобы продолжить.
- Нажмите на кнопку «Сканировать», чтобы начать сканирование вашего компьютера. Программа автоматически обновит свою антивирусную базу перед сканированием на наличие вредоносных программ.
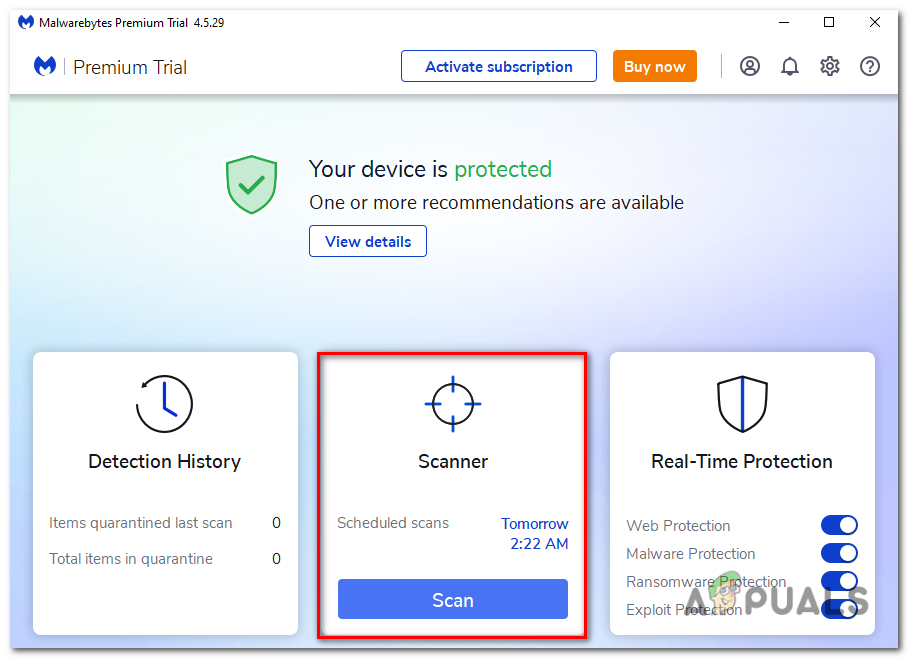 Нажмите на кнопку «Сканировать», чтобы начать сканирование вашего компьютера.
- Дождитесь завершения сканирования. Программа просканирует ваш компьютер на наличие угонщиков браузера, вредоносных программ и потенциально нежелательных программ. Этот процесс может занять несколько минут, поэтому вы можете выполнять другие задачи, периодически проверяя ход сканирования.
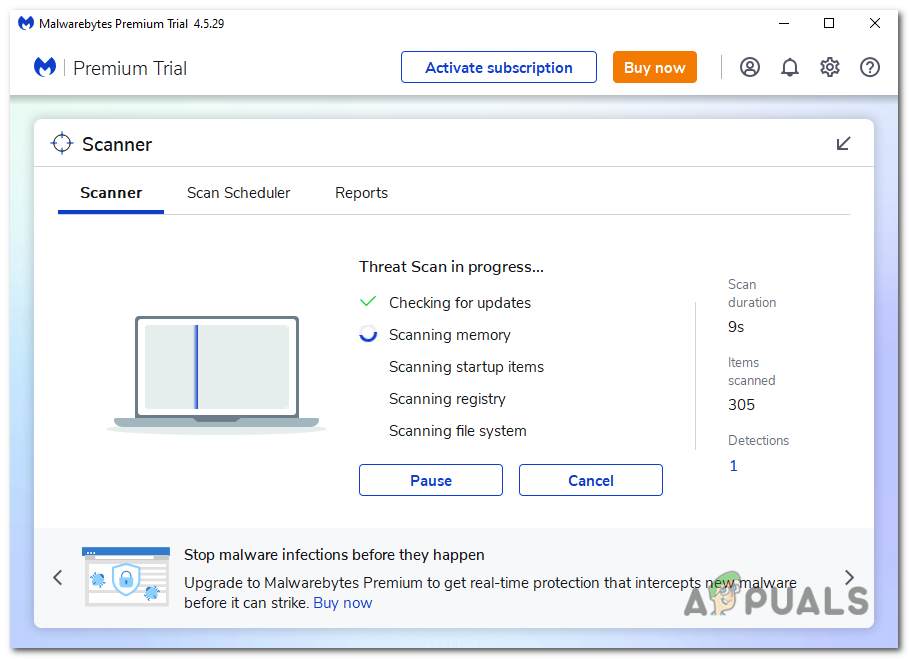 Программа просканирует ваш компьютер на наличие угонщиков браузера, вредоносных программ и потенциально нежелательных программ.
- После завершения сканирования отобразится экран, показывающий все обнаруженные вредоносные программы, рекламное ПО или потенциально нежелательные программы. Чтобы удалить эти угрозы, нажмите на кнопку «Карантин».
- Просмотрите список обнаруженных вредоносных программ и нажмите «Карантин», чтобы удалить их из вашей системы.
- Чтобы завершить процесс удаления, Malwarebytes предложит перезагрузить компьютер.
5. Сброс браузеров к настройкам по умолчанию
Если этот вирус влияет на вашу работу в Интернете, он заразил ваш браузер спам-уведомлениями, вредоносными расширениями и мошенническими настройками. Чтобы вернуть браузер к его состоянию по умолчанию, вам придется сбросить его. Сброс приведет к удалению всех расширений, панелей инструментов и других настроек, но ваши закладки и избранное останутся нетронутыми.
5.1 Сброс Google Chrome для Windows до настроек по умолчанию:
- Откройте Chrome и нажмите кнопку меню (обозначенную тремя вертикальными точками) в правом верхнем углу окна.
- В выпадающем меню выберите «Настройки».
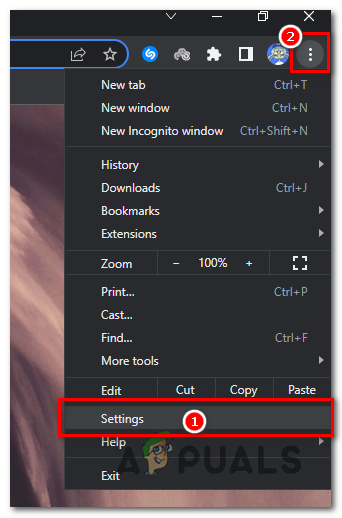 В выпадающем меню выберите «Настройки».
- На странице «Настройки» нажмите вкладку «Сбросить настройки» на левой боковой панели.
- Затем нажмите «Сбросить настройки до исходных значений по умолчанию».
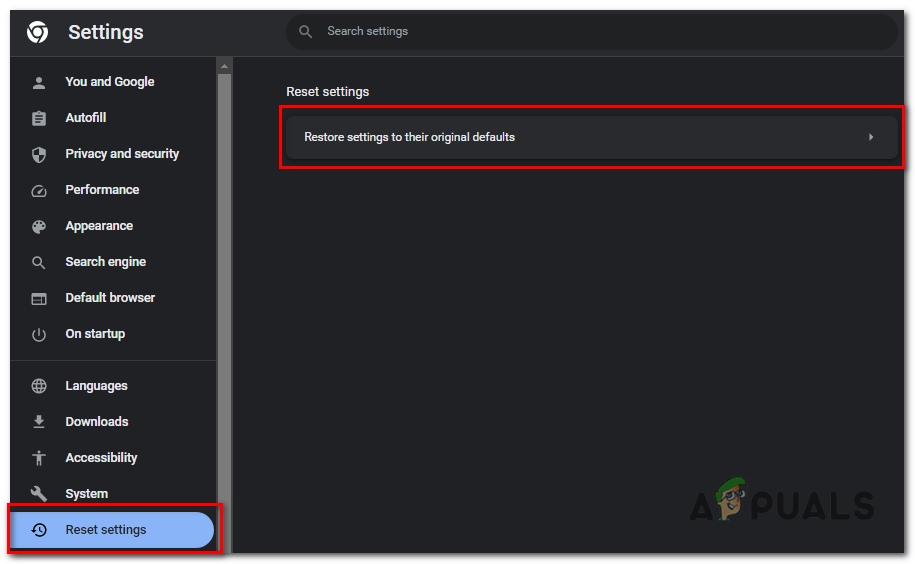 нажмите «Сбросить настройки до исходных значений по умолчанию».
- Появится диалоговое окно подтверждения с подробным описанием компонентов, для которых будут восстановлены значения по умолчанию. Чтобы продолжить, нажмите на кнопку «Сбросить настройки».
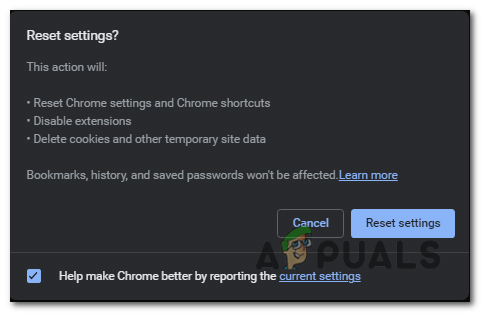 нажать на кнопку «Сбросить настройки».
- Необязательно: если вредоносное расширение продолжает переустанавливаться, вы также можете сбросить синхронизацию данных для своего браузера, посетив chrome.google.com/sync и нажав на кнопку «Очистить данные».
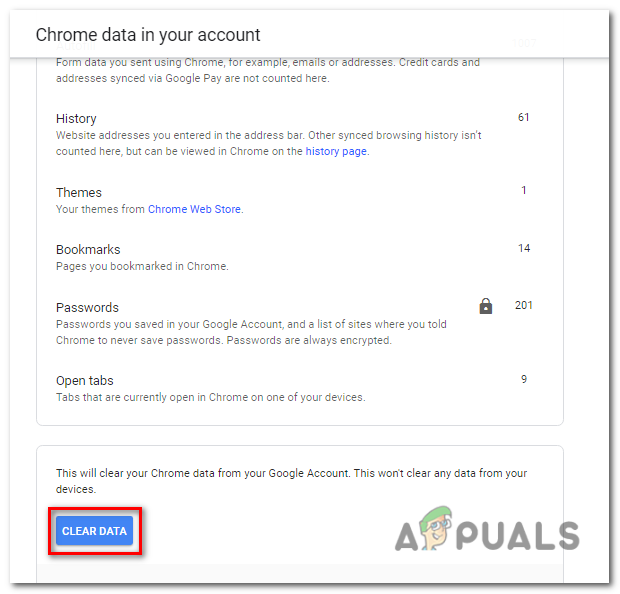 Если вредоносное расширение продолжает переустанавливаться, вы также можете сбросить синхронизацию данных для своего браузера, посетив chrome.google.com/sync и нажав кнопку «Очистить данные».
5.2 Сброс Microsoft Edge до настроек по умолчанию:
- Откройте Microsoft Edge и нажмите кнопку меню (представленную тремя горизонтальными точками) в правом верхнем углу окна.
- В выпадающем меню выберите «Настройки».
- На странице настроек прокрутите вниз и нажмите кнопку «Сбросить настройки».
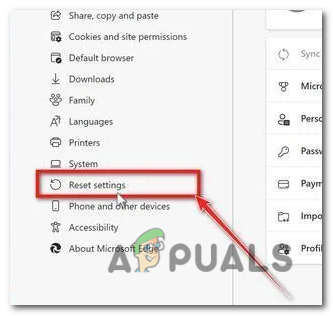 На странице настроек прокрутите вниз и нажмите кнопку «Сбросить настройки».
- Затем нажмите «Сбросить настройки до исходных значений по умолчанию».
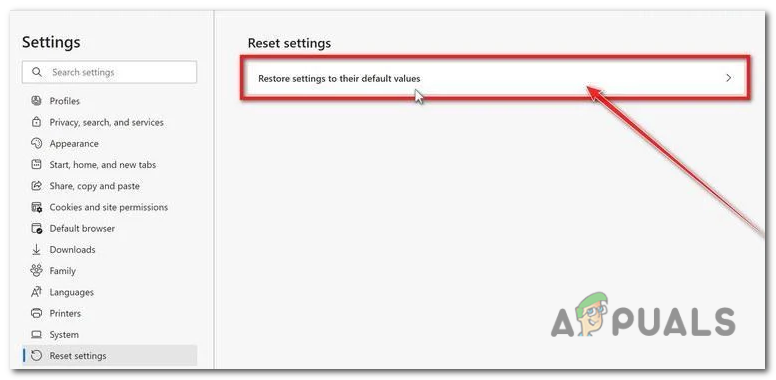 нажмите «Сбросить настройки до исходных значений по умолчанию».
- Появится диалоговое окно подтверждения с вопросом, хотите ли вы сбросить настройки Microsoft Edge. Чтобы продолжить, нажмите на кнопку «Сброс».
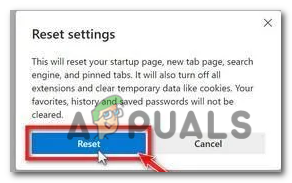 Появится диалоговое окно подтверждения с вопросом, хотите ли вы сбросить настройки Microsoft Edge. Чтобы продолжить, нажмите на кнопку «Сброс».
Программы для Windows, мобильные приложения, игры — ВСЁ БЕСПЛАТНО, в нашем закрытом телеграмм канале — Подписывайтесь:)
PUA:Win32/Puwaders.C!ml (Removal Guide)
Windows Defender may have informed you of this virus threat by alerting you that it had discovered the specific malware on your computer. These detections are Windows’ alarm signals informing you of any hazardous content it has spotted.
If it alerts you that you have a malicious virus on your system, you should not ignore it and take appropriate action to protect your device
These threats are often acquired through spam emails, infected websites, or by clicking on a link in an email. Once installed on the computer system, PUA:Win32/Puwaders.C!ml will begin to spread across your PC via Windows System files.
This allows them to access all of the information on your computer and even take control of it. Such threats should not be kept around the computer that is why Windows Defender will keep on alerting you about the malware until you take action on it.
Here are the symptoms that users who have their devices infected with PUA:Win32/Puwaders.C!ml are most likely to experience.
- Sudden problems with internet connection and applications
- Freezing or slowdowns in computer performance
- Difficulties opening documents or accessing files.
- Unusual pop-up ads appear online or when browsing.
- Overheat and high CPU usage.
Detections like these are particularly dangerous because they can be used to attack other users online by stealing their privacy credentials, financial information, and more.
If you think that you may have been affected by this specific type of virus, then it is important to remove it as soon as possible.
Since the detection name format matches how the built-in antimalware tool describes its discovered threats, Windows Defender is particularly the one that found the PUA:Win32/Puwaders.C!ml from the computer.
Typically, Windows Defender would be enough to eliminate the threat it found on the computer and you would have only needed to click the quarantine button to remove it.
Unless certain circumstances prevent Windows Defender to eliminate the said malware, you may utilize Malwarebytes Anti-malware to remove it for you.
Please follow the given instructions below to remove the detected threat from your system.
Remove PUA:Win32/Puwaders.C!ml with Malwarebytes Anti-Malware
We have also been using this software on our systems ever since, and it has always been successful in detecting viruses. It has blocked many known computer threats as shown from our tests with the software, and we assure you that it can remove PUA:Win32/Puwaders.C!ml as well as other malware hiding on your computer.

Not to mention, it is free to use and does not come at any cost to remove the viruses it finds on your computer.
To use Malwarebytes and remove malicious threats from the computer, follow the steps below:
1. Download Malwarebytes by clicking the button below, as we have made an additional and in-depth tutorial on how to use it. Otherwise, you may go to their official website via Malwarebytes.com (Avoid misspelling as it may lead to scams).
2. Visit their download section and start a Free Download to begin installing the software on your computer.  3. Once the Malwarebytes setup file (MBsetup.exe) has finished downloading, open the executable file in File Explorer, then right-click the setup and select run as administrator to give the highest system authority and make sure Malwarebytes is installed correctly.
 4. Make sure to carefully follow the installation setup wizard’s instructions and provide the relevant information it requires. You will be prompted with questions such as Personal or Business Use, Email Address, and others.
 5. From the application’s home screen, go to the scan tab and begin running a system scan. This will scan the whole computer, including memory, startup items, the registry, and the file system. This is done so not only the residuals of PUA:Win32/Puwaders.C!ml but also other trojan viruses hiding in the system can be detected.
 6. Since it can take a while, you should either relax and wait for it to finish or find something else to do. The length of the scan depends on the size of the files you have and the hardware capabilities of your computer. Here are some ways to make scanning faster.
7. Once the scan is finished, Malwarebytes will show the malicious viruses and threats it found on your PC. PUA:Win32/Puwaders.C!ml will also show up on the detection results, and it will show up in a threat name such as PUP.Optional.OpenCandy, and many more.  8. Select all the detected files from the report and click the quarantine button to remove the malicious items from the computer into the protected safe quarantine zone of the anti-malware program so that they would not affect and do malicious actions the PC again.
 9. After placing the virus files in the program’s quarantine, it may prompt you to restart the computer to finalize the full system scan procedure. Please restart your computer if prompted, as it is essential. After the restart, Malwarebytes will open and display a message that the scan was complete.
Note: Don’t forget to delete the quarantined files afterward.
Simply quarantining the malware files is not enough to make sure they are completely removed. This is a very common misconception: once you click the quarantine button, it is all good and gone.
But, while its effects and harmful activities are halted, the malware is still in the system, only placed in the anti-malware program’s quarantine folders. To completely remove it from the computer, go to Detection History from the home screen, select all Quarantined items, and click Delete.

You have successfully removed PUA:Win32/Puwaders.C!ml as well as the hidden threats on your computer. Rest assured they would not resurface again since Malwarebytes offers a premium trial for 14 days, so you could take advantage of it for free and prevent malware from infecting your system.
While the detection and removal of malware are free for Malwarebytes, the premium versions include real-time protection that ensures your computer is safe all the time. Although we encourage you to use the premium trial, you are free to purchase the full version if you find it useful.
We suggest Malwarebytes if you are looking for a removal tool and as a second opinion scanner, but if you want full-fledged antivirus software, we believe that the built-in Windows Defender is sufficient for computer security, or if you want something with a more sophisticated system and better protection: Kaspersky Free.
If you choose to uninstall Malwarebytes, you may suddenly see that Windows Defender Real-Time Protection is turned off. This is a common issue that users may face when uninstalling the software. To fix this issue, you may refer to this article.
Alternative: Kaspersky Free Antivirus
After removing PUA:Win32/Puwaders.C!ml and other malicious threats, you may want to install antivirus software to protect your system against malware.

More importantly, running an additional scan with a different program’s threat database will alert you to hidden Trojan viruses and rootkits that were not removed from the prior scan with Malwarebytes.Kaspersky is a widely known antivirus software that has been on the market for as long as the field of cybersecurity has existed. It is acclaimed by professionals in the field and is one of the most effective antivirus programs available. With its advanced internet security protection, it can also remove additional malware from the computer.
What is the difference between anti-malware and antivirus? Anti-Malware software is designed to specifically remove malware and its variants. In addition, it employs heuristic-based detection by picking up harmful code from files.
On the other hand, an antivirus uses signature-based detection, which examines data for attacks to protect users from dangerous viruses, including keyloggers, loaders, worms, trojans, and others.

Malwarebytes and Kaspersky are identical, but Kaspersky is a better overall program since Malwarebytes’ main purpose is to remove malware, but Kaspersky has been known for comprehensive computer security protection ever since.
Based on our experience removing malware, when two different programs are used to scan, various threats are identified by one software but not by the other. Given that their threat databases differ from each other, it might be able to capture harmful viruses, rootkits, and trojans that Malwarebytes has missed.
Please be aware that if you decide to use Kaspersky, you should first uninstall Malwarebytes because having both security programs installed will cause a conflict. If you choose to do so, please remove Malwarebytes first, as it is essential to do so before we get started.
1. Click the button below to start downloading Kaspersky Antivirus on your computer. On the following page, we have provided clear details on how to install it on the computer. On the other hand, you may go to their official website by searching for the software on your web browser or typing Kaspersky.com (Beware of misspellings since cybercriminals typically use these as exploits to redirect users to malicious webpages).
2. Go to the download page for Kaspersky Free Antivirus. Before clicking download, you will be prompted to choose your continent and where your country is located. This is very important, and you should not choose a different country because you will be met with a «Not supported in your region» message during installation.  3. Once you click download, a setup file (startup.exe) will be downloaded on the computer. After it has finished downloading, open its file location, right-click the executable file, and then select Run as administrator. This will ensure that Kaspersky’s installation will be smooth and will not result in certain errors.
 4. The Kaspersky installation wizard will launch, and you can then proceed to install Kaspersky Free by following the setup instructions. If a UAC prompt appears, simply accept it and proceed with the installation.
 5. Please be patient while Kaspersky is being installed on your computer. The speed and length of the installation process will depend on your computer’s specifications. Kaspersky also mentioned that sluggishness or dark displays during the installation of their program are normal and should not be worried about.
6. To use the antivirus program, you must first create an account on the sign-in page that appears after the antivirus application has been successfully installed on the computer. If you’re looking for the sign-up button, simply enter your email exactly as it appears; if you don’t already have an account, one will be created for you.  7. Kaspersky will ask you to decide which plan to use. It will be either the Standard version or Kaspersky Plus. In this case, the standard version is all you need for now. If you want to try the premium version of Kaspersky, you may opt for Kaspersky Plus to try the features for free. You do not have to add a payment method to get started, and after the trial ends, you will be downgraded to the Standard version unless you pay for it.
 8. You will be asked if you want to install additional applications, namely Kaspersky Password Manager and a VPN. Feel free to opt for a program you might want to use; otherwise, install both, or choose not to if you do not need them.
 9. Kaspersky will ask you to scan for viruses in the background. Simply choose not to do so because we will be doing a full system scan later; however, doing a scan now will only initiate a quick scan. However, if you want to be safe, you can run the background scan now and proceed with a full system scan after.
 10. Once the antivirus application has opened, go to the security tab and click the choose a scan button. You will be presented with several different scans; go for the full system scan to ensure full computer security. Always remember to update the database because this will ensure that Kaspersky can detect newly discovered threats and exploits.
 11. A full system scan will take a long time to finish since it will look into all the files on the computer, including the registry, memory, startup applications, and many more. The scanning time will depend on how many files there are on the computer and how big the files are. Additionally, the computer’s hardware and specs will also play into how long the scan will take.
12. After the full system scan is finished, it may detect remnants of the PUA:Win32/Puwaders.C!ml detection virus as well as other malware hiding in the computer, showing its location along with a detection name (Trojan.Win32.Generic, Exploit.Win32.Generic, etc.) given to it. Go ahead and proceed to disinfect and restart the computer.  13. The Advanced Disinfection process will then start, and depending on the amount of RAM the computer has, it could take some time. It will then request a computer restart to complete the operation.
 Your computer will now have finished the entire system scan after restarting. By doing this, you can be sure that PUA:Win32/Puwaders.C!ml and other types of malware and viruses have been wiped from your computer.
You shouldn’t be concerned if the scan turned up no instances of malware or viruses, which indicates that there isn’t any malware on your computer. If two independent programs declare your computer safe, then that’s probably the case.
For a better and safer web browsing experience, we’ve provided a few security measures and advice below that will safeguard your browser and computer from harmful threats like worms, malware, trojans, keyloggers, stealers, and other kinds of computer viruses that will harm user data.
Protective measures for better overall security
Removing the malicious detections from the computer is one thing; keeping it secure for the future and a long period is a different thing and will require certain things to make sure you are secured, especially if you do not know most of the ins and outs of the device you are using.
Cybercriminals are always stepping up their game to make sure they infect users and extract data and money from them.
We encourage you to take the actions listed below to ensure complete security before leaving this page because we strongly promote web security and having a secure online presence.
Safeguard your data and privacy online by using a VPN application
VPNs, also known as virtual private networks, guarantee your safety and complete anonymity while you browse the internet.
In contrast to a firewall, which monitors and blocks potentially harmful connections in the network, A VPN hides the user’s connection via a tunnel so that it would appear to third parties as a different IP address and location.
This ensures that your data won’t be leaked because the program hides it. Be aware that visiting infected websites may cause your IP address and location to be disclosed; however, if you use a VPN, this will prevent your true IP address from being revealed to malware actors.
If you already had Kaspersky installed from the previous step, you had the choice to install its integrated Virtual Private Network, which is a good tool that we also advise.
However, if you decide against doing so and instead download a VPN-only program to cloak your web browsing activity, Mullvad VPN is an excellent choice for fast connections and better privacy.

Since user privacy is the main focus of a virtual private network program, Mullvad VPN excels at putting users’ privacy first. You do not need to enter your email address while registering to download their application because they maintain anonymous accounts.
If you wanted to hide or didn’t want your credit card information to be disclosed, they also accept Bitcoin payments. According to their website, they support a free internet that is devoid of surveillance and censorship.
They have also been announcing new server locations to guarantee users a fast connection anytime they want to connect to various areas throughout the world.
Use a firewall to prevent cyber attacks
A security firewall is required for every internet connection that is made. It is an essential tool that enhances security and stops online attacks.
Through a security mechanism, it controls incoming and outgoing network connections on your system and network and filters the undesirable ones. Consider it a further barrier against malicious assaults and zero-day exploits.
You don’t need to do anything if you installed Kaspersky in the previous step because the program we installed earlier comes with a built-in firewall that is turned on by default.
On the other hand, if you prefer a standalone, fully functional firewall utility application that is exclusively focused on securing the network, we recommend ZoneAlarm Firewall.
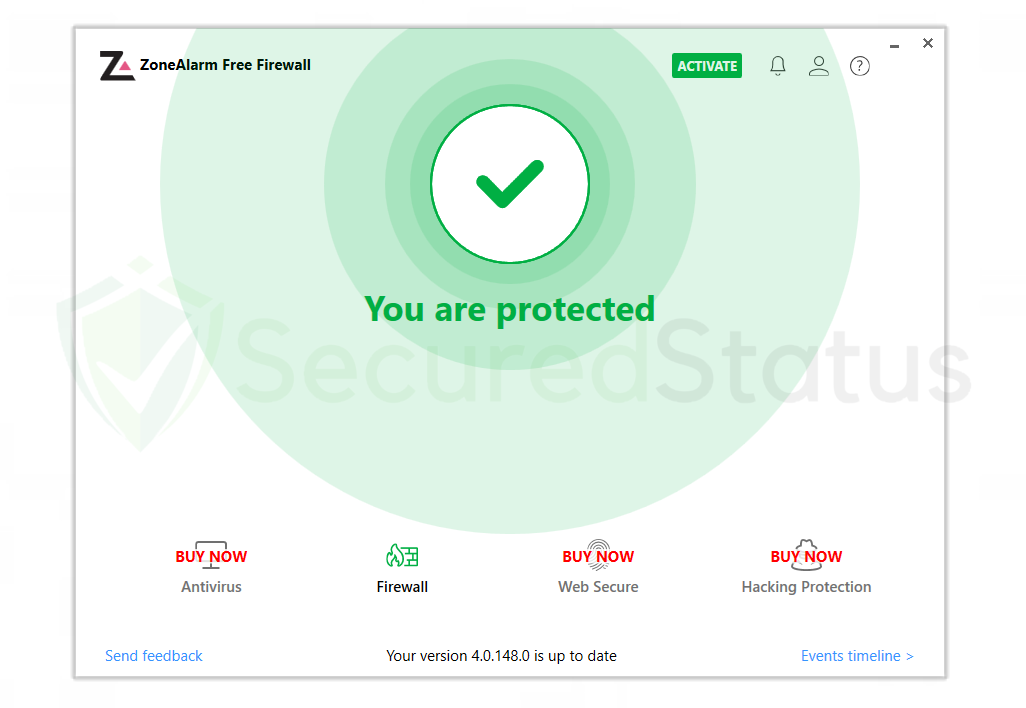
You can also opt for ZoneAlarm Free Firewall as your first line of defense between your device and the internet. The program safeguards your network and blocks any dangers, and you can use the free version of it without paying anything.
It provides a robust two-way protection solution that guards against spyware from disclosing your data online while also hiding your PC from nefarious hackers.
With its cutting-edge anti-bot protection, it also protects your computer from automated cyberattacks in real-time.
Additionally, it protects your computer against spam, dubious websites, and many others. Lastly, it provides real-time defense against automated cyberattacks with its cutting-edge anti-bot security.
Bottom Line
Always make sure that your device is protected against sneaky exploits and stealthy cyberattacks. While taking precautions and avoiding dubious websites are crucial, having a solid line of defense is essential to ensuring the security of your network and data.
If you experience another malware issue, please visit our website to find a solution for your problem or get in touch with us, and SecuredStatus will be happy to assist you once again.