Sorry, you have been blocked
This website is using a security service to protect itself from online attacks. The action you just performed triggered the security solution. There are several actions that could trigger this block including submitting a certain word or phrase, a SQL command or malformed data.
What can I do to resolve this?
You can email the site owner to let them know you were blocked. Please include what you were doing when this page came up and the Cloudflare Ray ID found at the bottom of this page.
Cloudflare Ray ID: 803ece104d630523 • Your IP: Click to reveal 178.175.133.131 • Performance & security by Cloudflare
What Is Usoprivate
ETL stands for Event Trace Log file which is created by Microsoft Tracelog, a program that creates logs using the events from the kernel in Microsoft operating systems. … To answer your query, you may delete these files and deleting will not affect anything on your system.
What is USO private?, The USO is a nonprofit, charitable corporation chartered by Congress that relies on donations from individuals, organizations and corporations to support its programs. It is not an agency of the United States Government. … Learn more about the history of the USO.
Furthermore, What is Boost_interprocess?, I have discovered that the boost_interprocess folder, and its contents, are created by the Cloudfogger app on my system. Cloudfogger is (was) an app to automatically encrypt the contents of folders synced with cloud storage services.
Finally, What are UNP logs?, Microsoft changed its use of UNP a while ago (I’m not sure when) and it now stands for Update Notification Pipeline related to files used by Windows 10 to improve Windows Update service components in your device, specifically to manage feature updates.
Frequently Asked Question:
What is UNP on my computer?
UNP stands for Update Notification Pipeline, commonly mistaken for Universal Notification Platform. The main function of this gear is to assist the Windows 10 system and ensure that all new updates will be installed correctly.
Can I delete UNP?
This cyber threat is launching as an executable file also known as UNP.exe or UNPCampaignManager.exe. … The trojan may be hidden in system folders or other common directories to convince people that this executable is a legitimate application and there is no need to delete it.
Can I delete universal notification platform?
Unfortunately, it can‘t be remove. You can disable it though based on a Microsoft support post through registry. … You can disable it though based on a Microsoft support post through registry.
What is DFIX?
Here is the answer from Microsoft: “The DIFx driver store is a repository for driver packages that is located on the computer’s hard disk drive and is managed by Microsoft Windows Driver Install Frameworks (DIFx). DIFxApp, DPInst, and other DIFx tools use the driver store to store and retrieve driver packages.”
Can I delete Usoshared logs?
2 Answers. ETL stands for Event Trace Log file which is created by Microsoft Tracelog, a program that creates logs using the events from the kernel in Microsoft operating systems. … To answer your query, you may delete these files and deleting will not affect anything on your system.
Can I delete UNP folder?
Select your root directory and then use the Find functions (Ctrl + F) to search for “UNP” and delete all of those folders.
What is Boost_interprocess folder?
The boost_interprocess folder is one of the methods for inter-process communication by means of shared memory, and you may see this folder on other OSs since it is a boost mechanism. The file(s) you see in the folder are named shared memory objects.
Can I delete universal notification platform?
Unfortunately, it can‘t be remove. You can disable it though based on a Microsoft support post through registry. … You can disable it though based on a Microsoft support post through registry.
What is universal notification platform?
UNP stands for Universal Notification Platform and can show notifications on your Desktop. Symptoms. Pop-up boxes, messages, and alerts appear on your Windows 10 desktop. The reason is that the Universal Notification Platform is made to show you advertisements of things that you might want.
What apps can I uninstall on Windows 10?
Now, let’s look at what apps you should uninstall from Windows—remove any of the below if they’re on your system!
- QuickTime.
- CCleaner. …
- Crappy PC Cleaners. …
- uTorrent. …
- Adobe Flash Player and Shockwave Player. …
- Java. …
- Microsoft Silverlight. …
- All Toolbars and Junk Browser Extensions.
What is UpdateNotificationMgr?
SUMMARY: UpdateNotificationMgr.exe, UNPUXLauncher.exe, UNPUXHost.exe, UNPCampaignManager.exe and UNPDetector.exe files present in UNP folder in your Windows 10 computer are not a virus or malware. These files are used by Windows 10 to improve Windows Update Service components in your machine.
What is Remsh EXE?
The legitimate remsh.exe is a reliability improvement file introduced by the Windows update KB4023057. Remsh.exe was released to address update component issues specifically for Windows 10 Versions 1057, 1511 and 1607.
Can I delete UNP folder in Program Files?
Some malicious websites use this UNP folder and its files to scare their users and thus sell anti-malware that promises to remove this folder and its contents. … There is no problem with the UNP folder in Program Files.
Can I delete UNP?
This cyber threat is launching as an executable file also known as UNP.exe or UNPCampaignManager.exe. … The trojan may be hidden in system folders or other common directories to convince people that this executable is a legitimate application and there is no need to delete it.
What is UNP software?
UNP Campaign Manager is a program, developed by Microsoft. UNP stands for Universal Notification Platform and can show notifications on your Desktop. Symptoms. Pop-up boxes, messages, and alerts appear on your Windows 10 desktop.
Can I delete universal notification platform?
Unfortunately, it can‘t be remove. You can disable it though based on a Microsoft support post through registry. … You can disable it though based on a Microsoft support post through registry.
What is USOShared folder?
The USOShared folder contains which belong to the Windows Update service . . . I presume those files are etl files – ETL – Event Trace Log file which is created by Microsoft Tracelog, a process that creates logs using the events from the kernel in Microsoft operating systems.
Thinking About Usoprivate Folder? 0 Reasons To Be Worried
The usoprivate folder and usoshared folder are two folders at location ‘C:\ProgramData‘ in windows 10. Common users of the Windows operating system don’t have very much idea about these folders. Even on the internet, there does not seem to be a consensus among the users regarding these folders. Some users report these folders as malware, while other claim that these are system folders and are harmless. Let’s explore these folders in detail.
What does USO mean?
USO is short for Update Session Orchestrator. All the processes or folders with ‘uso’ in their name are somehow part of the Windows Update services. The USO is a service that is responsible for updates in your system. Downloading, verifying, and installing the updates are the responsibilities of this service.
You can check this service running in the task manager under the services tab. It has the same PID as the process svchost.exe.
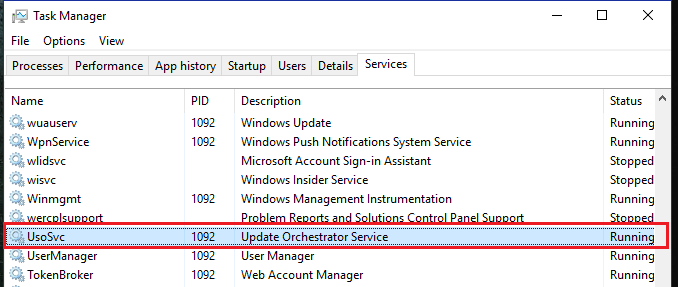
UsoSvc with PID 1092
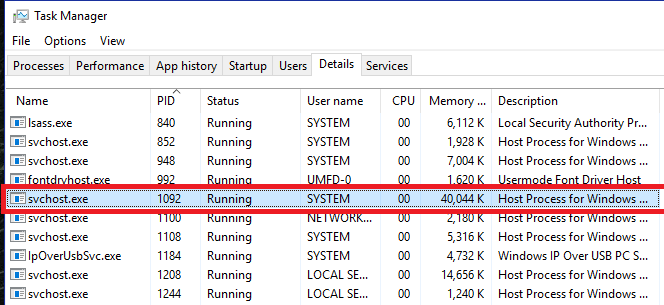
svchost.exe with PID 1092
USOPrivate folder
This folder is located in the C drive inside the ProgramData folder. Sometimes the folder is hidden. You might have to click on the Hidden item tick box under the view tab to see the folder. The access to the folder is restricted to the higher privileged user. It would help if you were an Administrator to open and look inside this folder. Inside this folder, you will find the usoprivate folder.
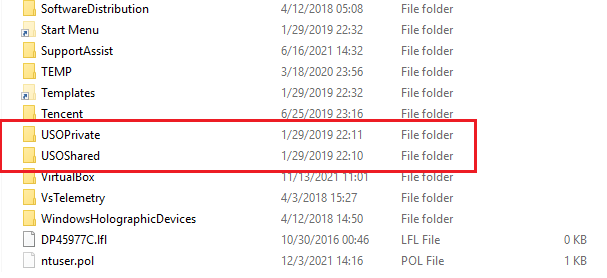
USOPrivate folder in the ProgramData
As you can see in the image, the USOPrivate folder was last modified a long time ago. Along with it, there is also the USOShared folder. Let’s have a look inside these folders.
Inside USOPrivate
On opening the USOPrivate folder, you should find only one folder: UpdateStore. Again on opening this folder, you should see three XML files. You can easily see the content of these files, open the file with any text editor of your choice, and you can view the content of these files.
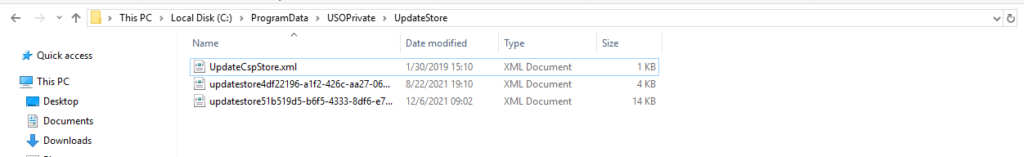
XML files in the USOPrivate/UpdateStore
If you open these files with any text editor, you will notice that these are just XML files without any executable code or script. There’s nothing suspicious about these files.
USOShared folder
Another folder alongside USOPrivate that people claim to be malware is USOShared. This folder also requires Administrator privileges. It contains a lot of ETL files. ETL stands for Event Trace Logs. These log files are created by the Tracelog process, which keeps logs of the events from the kernel level of the Windows Operating System.
Technically, it is safe to remove the log files, and it does not affect the system performance in any way. Admin privileges are required to delete these files. But it is recommended not to alter any folder content until there is a strong reason.
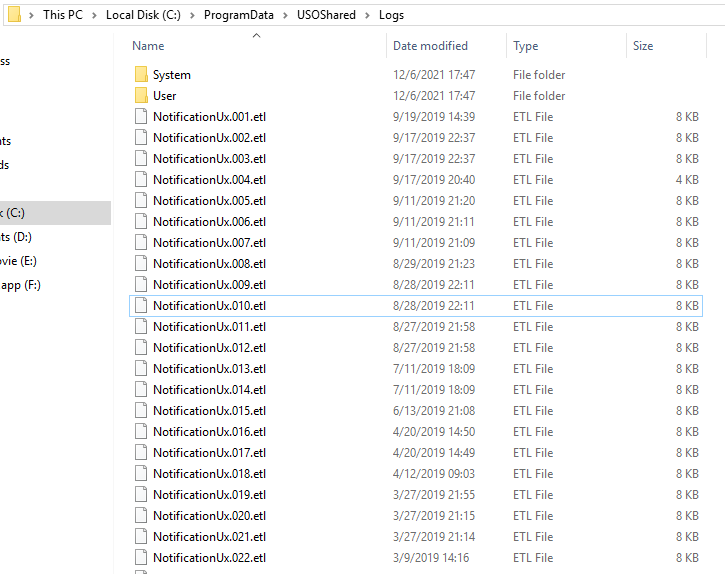
ETL files in USOShared/Logs
Difference between USOPrivate and USOShared
The main difference between USOShared and USOPrivate folder is the type of data they contain. USOPrivate folder contains XML files with basic update info and links in them, while the USOShared folder contains ETL files that are system logs. It is clear that both folders serve a different purpose, even when they fall under the same Windows Update service.
USOPrivate MD5 Hash
MD5 stands for Mixed Digest 5. It is a cryptographic hash function that takes a string of data of arbitrary length and spits out a fixed-length string. These kinds of functions are widely used on the internet to confirm data integrity because a property of these functions, called the Avalanche effect. The Avalanche effect means the slightest change in the function’s input will change the output completely. That is why these functions are used to check if a file was altered in any way or not.
In Windows, a Utility tool is available to find the hashes of data, called “certutil”. Unfortunately, it can’t be used to hash a whole folder. But, there are workarounds you can use either hash each file or can compress the entire folder into a zip file and then feed it to the Hash function. Follow the given steps to find the MD5 hash of a file.
- open the folder where your target file is
- Press and hold ‘Shift‘ key and then Right click on the mouse.
- In the menu, click on ‘Open PowerShell Window here‘.
- A PowerShell window will show up with the directory opened in it.
- type ” certutil -hashfile <name_of_file> MD5 “
- the output MD5 hash digest will show up.
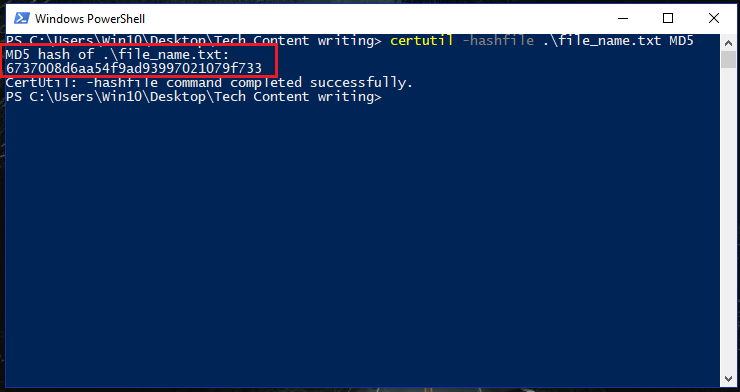
An MD5 hash of a file using certutil
Is USOPrivate a threat?
Some people on the Internet claim that the USOPrivate folder is malware, While most people claim it to be harmless. As we saw ourselves, the folders only contained some XML files that did not have any kind of executable code. Therefore it can be concluded that the USOPrivate folder is not a Threat. It is just a system folder part of the Windows Update mechanism.
Still, if a user is unsure about the folders, they can always run an antivirus scan on the drive. If the antivirus software finds anything suspicious, then the appropriate measures should be followed as suggested by the antivirus itself.
Can I delete USOPrivate?
A straightforward answer to this question is Yes. You can indeed delete the USOPrivate folder just like any other folder; The system doesn’t even show a warning dialog box when you try to delete it, unlike the USOShared folder, which asks for admin privileges before deleting. But, keep in mind that it is neither necessary nor recommended.
USOPrivate что за папка в Windows 10?
 Всем даровчик. Опять мы говорим о Windows 10 и о непонятных вещах в ней. Мне даже мысль в голову пришла, что в этой Windows 10 слишком много косяков всяких… Ладно, негатива нем не нужно. Так, что там у нас сегодня? А сегодня мы будем изучать папку USOPrivate, я покопаюсь в интернете, достану инфу и здесь ее изложу в удобном формате.
Итак ребята, я узнал что папка USOPrivate обычно расположена в C:\ProgramData и все это относится к Windows Update, ну то есть к обновлениям.
Ребята, инфы нет вообще по поводу USOPrivate, я нашел только то, что это относится к обновлениям и эта инфа кстати на официальном форуме Microsoft.
Нужно ли удалять эту папку? Нет ребята, я так не думаю. Если она идет от винды, то значит так нужно, пусть будет.
Ребята, я в шоке.. Ну кто бы мог подумать, что и у меня эта папка есть.. Я открыл эту папку:
Ну и вот смотрите сами:

Тут даже две папки похожи по названиям, это USOPrivate и USOShared Посмотрим что внутри? Давайте! Вот я открыл папку USOPrivate, внутри как мы видим есть еще папка UpdateStore:

Внутри папки UpdateStore какие-то два файла, это UpdateCspStore.xml и updatestore51b519d5-b6f5-4333-8df6-e74d7c9aead4.xml:

Без понятия что это за файлы. Но у меня точно вирусов нет, это стопудово, так как безопасность на высшем уровне.
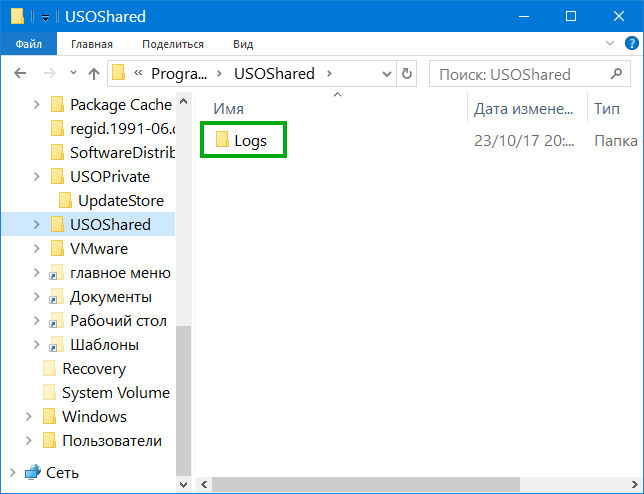
Потом я открыл папку USOShared, внутри вижу папку Logs:
Зашел в папку Logs, а внутри вот что:
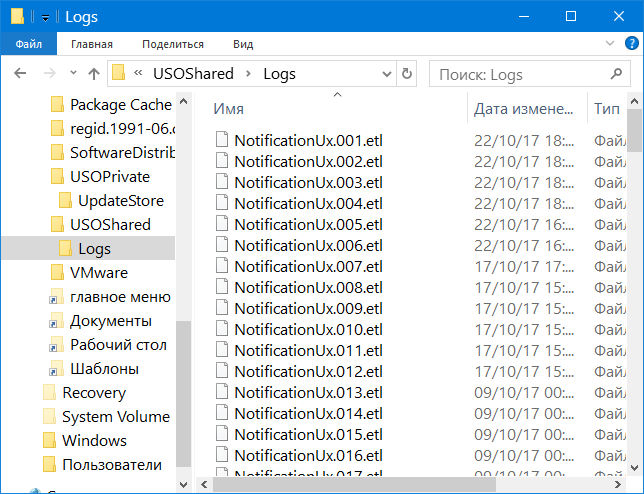
Просто куча файлов с расширением etl.. Когда я покрутил мышкой список файлов, то я там увидел еще много файлов, в имени которых фигурирует слово Update, смотрите:

То есть все сходится, это имеет какое-то отношение к обновлениям.
В общем какой можно сделать вывод? Папки USOPrivate и USOShared это никак не от вирусов. У меня их не может быть, поверьте, так как все очень жестко контролируется, программы не ставятся, в интернет допуск только ограниченным процессам. То есть все под контролем. Я не знаю можно ли эти папки удалять, мне даже в голову такая мысль не пришла, ибо их создала сама винда. И весят они почти ничего. Так что я вам тоже не советую их удалять…
На этом все ребята, думаю мы разобрались и поняли, что об этих папках стоит забыть. Удачи вам и счастья в жизни!