LogiShrd Logs by LogiShrd
LogiShrd Logs is published by LogiShrd. You can find out more about LogiShrd Logs at its official website or at LogiShrd’s website.
How do I clean LogiShrd Logs?
LogiShrd Logs may store excess, temporary data on your computer that can take up valuable space. It may also store private data such as passwords or browsing history in the registry or on the file system. The easiest way to erase this data is by downloading AppCleaner, it is 100% free and about 1MB in size. A portable version is also available.
If you want to clean LogiShrd Logs manually, you can follow the steps outlined below. There are five locations in the file system where LogiShrd Logs stores data that can be cleaned.
Files
To clean your file system from files stored by LogiShrd Logs and to gain free disk space, examine the following file system locations. First of all, open a command prompt window:
- Hit the Windows key , usually located in the lower left of your keyboard between the Ctrl and Alt keys.
- Windows XP/Vista/7: Click Run.
- Type cmd
- Hit Enter
Now list all the files stored by LogiShrd Logs that can be cleaned:
- Type dir %APPDATA%/LogiShrd/Updater/LuUpdater.log
- Type dir %APPDATA%/LogiShrd/Updater/UpdateList.csv
- Type dir %ALLUSERSPROFILE%/Logishrd/unifying/EngineLog.*
- Windows XP: Type dir %ALLUSERSPROFILE%\Application Data/Logishrd/unifying/EngineLog.*
- Type dir /s %ALLUSERSPROFILE%/LogiShrd/*.log
- Windows XP: Type dir /s %ALLUSERSPROFILE%\Application Data/LogiShrd/*.log
- Type dir %LOCALAPPDATA%/VirtualStore/ProgramData/Logishrd/unifying/EngineLog.*
- Windows XP: Type dir %USERPROFILE%\Local Settings\Application Data/VirtualStore/ProgramData/Logishrd/unifying/EngineLog.*
- Type dir /s %LOCALAPPDATA%/VirtualStore/ProgramData/LogiShrd/*.log
- Windows XP: Type dir /s %USERPROFILE%\Local Settings\Application Data/VirtualStore/ProgramData/LogiShrd/*.log
Once you have identified the files stored by LogiShrd Logs that you want to clean, delete them using the del command or Windows Explorer.
LogiShrd
In the «My Documents» folder, I get a folder named «Logishrd» that contains a subfolder called «records» and a file without an extension named «productivity». It is obviously created by the application of the directive, but why is it in «My Documents» even when I remove it? In addition, the file is 0 bytes, so it seems not be storing anything.
Is there a way to remove it permanently?
Thanks for posting on the Microsoft answers Forum.
The file is related to Logitech QuickCam. If you no longer use the webcam you can uninstall it. That should get rid of the Logishrd file and the contents inside. If you are still using the Logitech QuickCam, then the folder will remain in the My Documents folder.
I hope this helps answer your question.
Marilyn
Microsoft Answers Support Engineer
Visit our Microsoft answers feedback Forum and let us know what you think
Similar Questions
Original title: Windows cannot find «C:\Program Files\Common Files\LogiShrd\CDDRV3\LDConfig.exe.» Make sure that you type the name correctly, and then try again.
This error keeps showing up in when I connect to my pc. How am I able to fix this? It’s really annoying. Please help me.
Its a file/utility Logitech and nothing to do with the victory
To solve the problem that I have, program uninstalled, rebooted machine. Has conducted an audit of the registry and remove the entries from 7 registry errors in Links 2003. Rebooted the machine. Installed Links 2003, installed patch 1.05, 1.07, and Links2k3-nvidia_win7_FINAL. I also tried to launch, links 2003 Safe Mode and still, I get this error message: ERROR: Invalid allocation, 1610612738 bytes. Any help would be greatly appreciated.
ERROR: Invalid allocation, 1610612738 bytes
Processor registers EAX = 0 x 00000000 EBX = 0 x 00000000 ECX = 00000000 EDX = 00000000 Flags x 0 x 0 = 0 x 00000000
= ESI = 0X00000000 EDI 0X00000000 EBP = 0X0012F4A8 ESP = 0X0012F348 EIP = = 0X00000000
EIP (0X00000000)? ?? ?? ?? ?? ?? ?? ?? ?? ?? ?? ?? ?? ?? ?? ?? ?? ?? ?? ?? ?? ?? ?? ?? ?? ?? ?? ?? ?? ?? ?? ??
ESP (0X0012F348) 0012F35C 0012F634 0012F62C 01DC3DC0 60000002 00010000 000001A 9 03C20DE0
00000100 0000002D 01DC4258 00000200 0000003D 01FDFDB0 76F5491C 00000014
75206AC4 84027F1C 00000674 75206E93 75206E9E 0031007E 75206E9E 004C002E
Details of the machine
===============
Name of executable: C:\Links 2003\LINKSMMIII. EXE
Executable hour, date: 19:49:12 Tuesday 3/30/2010
Command line:
Current directory: C:\Links 2003
Currently, date: 19:05:49 Tuesday 6/22/2010
GameOS build version: Version 1.1 02/11/2000
Software rasterizer: c:\links 2003\assets\binaries\blade.dll (size 282 693 bytes)
Username: Mike Harrison
Computer name: HICHAMCHGORA
Processor: 2812 MHz AMD 3DNow unknown MMX! Model SSE = 10, Type = 15, Stepping 0 = (6 processors)
Cache information: unknown
L2 w/r/rw speed: 4 cycles 22496 Mbps, 4 cycles 22496 Mbps, 4 cycles 22496 Mbps
Main memory r/w/rw speed: 14 cycles 6427 MB/s, 13 cycles 6921 Mbps, 10 Mbps 8998 cycles
W/r/rw video memory speed: 204 cycles 441 MB/s, 38 cycles 2368 Mbps, 289 cycles 311 Mbps
W/r/rw memory AGP speed: 204 cycles 441 MB/s, 37 2432 Mbps, 288 cycles cycles 312 MB/s
Operating system: Windows (6.1.7600)
DirectX version: 9.04.00.0904
Since booted time: 2 h 45 m 25 s
In the logic of the game time: 0 h 0 m s 0.62 (on frame 3)
App running time: 0 h 0 m s 0.62
Physical memory: 2 147 483 647 bytes (2048 Meg)
Physical memory available: 2 147 483 647 bytes (2048 Meg)
The swap file size: 4294967295 bytes (0 Meg)
Available page file: 4294967295 bytes (0 Meg)
Virtual memory: 2,147,352,576 bytes (2048 Meg)
Virtual memory available: 1,937,620,992 bytes (1848 Meg)
Amount of the used battery: 3172 bytes
Memory load: 31%
Desktop video mode: 32bpp 1920,1080
Mode when the accident occurred: full screen 1920 x 1080 x 32 (NVIDIA GeForce GT 220)
Networked Machine: No.
Executable version: 01.08.06.2200
PCI Chipset: unknown
Path of Threads process Pri
==========================================
TaskHost.exe: 8: 8: C:\Windows\system32\taskhost.exe
DWM.exe: 13:5: C:\Windows\system32\Dwm.exe
BCU.exe: 8:6: C:\Program Files\DeviceVM\Browser Configuration Utility\BCU.exe
RoxioBurnLauncher.exe: 8:8: C:\Program SharedCOM 2010\Roxio Burn\RoxioBurnLauncher.exe
VxBlockServer.exe: 8:5: C:\Program Files\Common PX storage Engine\VxBlockServer.exe
SetPoint.exe: 8:5: C:\Program Files\Logitech\SetPoint\SetPoint.exe
KHALMNPR. EXE:-08:27: C:\Program Files\Fichiers Files\Logishrd\KHAL2\KHALMNPR. EXE
RtHDVCpl.EXE: 8, 9: C:\Program Files\Realtek\Audio\HDA\RtHDVCpl.EXE
Skype.exe: 08:20: C:\Program Files\Skype\Phone\Skype.exe
LinksLauncher.exe: 8:1: C:\Links 2003\LinksLauncher.exe
LINKSMMIII. EXE: 08:16: C:\Links 2003\LINKSMMIII. EXE
Version numbers of DLLS
===================
Msvcrt.DLL — Version 7.0.7600.16385 — found in C:\Windows\system32
‘Msvcrtd.dll’ is not found
Msvcirt.DLL — Version 6.1.7600.16385 — found in C:\Windows\system32
‘Msvcirtd.dll’ is not found
amstream.DLL — Version 6.6.7600.16385
Quartz.DLL — Version 6.6.7600.16385
Ir50_32.DLL — Version R.5.10.15.2.55
Dsound.DLL — Version 6.1.7600.16385
Dinput.DLL — Version 6.1.7600.16385
D3dim.DLL — Version 6.1.7600.16385
Ddraw.DLL — Version 6.1.7600.16385
dplayx.DLL — Version 6.1.7600.16385
Audio device 0 (current) — (HW disabled mix)
==============
Description: Realtek Digital Output (Optical) (Realtek High Definition Audio)
Driver file: <0.0.0.00000000>.
Data of the driver file: can not find the driver file
CERTIFIED: No.
EMULDRIVER: No.
CONTINUOUSRATE: Yes
PRIMARYMONO: Yes
PRIMARYSTEREO: Yes
PRIMARY8BIT: Yes
PRIMARY16BIT: Yes
SECONDARYMONO: Yes
SECONDARYSTEREO: Yes
SECONDARY8BIT: Yes
SECONDARY16BIT: Yes
MinSecondarySampleRate: 100
MaxSecondarySampleRate: 200000
PrimaryBuffers: 1
MaxHwMixingAllBuffers: 1
MaxHwMixingStaticBuffers: 1
MaxHwMixingStreamingBuffers: 1
FreeHwMixingAllBuffers: 0
FreeHwMixingStaticBuffers: 0
FreeHwMixingStreamingBuffers: 0
MaxHw3DAllBuffers: 0
MaxHw3DStaticBuffers: 0
MaxHw3DStreamingBuffers: 0
FreeHw3DAllBuffers: 0
FreeHw3DStaticBuffers: 0
FreeHw3DStreamingBuffers: 0
TotalHwMemBytes: 0
FreeHwMemBytes: 0
MaxContigFreeHwMemBytes: 0
UnlockTransferRateHwBuffers: 0
PlayCpuOverheadSwBuffers: 0
Video device 0
==============
Description: NVIDIA GeForce GT 220
Company / Chipset: nVidia.
Driver file: nvd3dum.dll
Driver size: 9 386 600 bytes
Driver date: 22:55:32 Saturday 4/3/2010
Attributes: Final Version, Private Build
Driver version: 8.17.11.9745
Version: 8.17.11.9745
Hardware ID: 10DE.0A20 (Rev 162, Subsys 0 x 12253842)
Video memory: 2,375,872,512 bytes (2266 Meg)
Mem texture map: 1,034,485,760 bytes (987 Meg)
AGP texture memory: 1,341,386,752 bytes (1279 Meg)
Modes of FourCC: NV12 NV24 YV12, UYVY, YUY2 AI44 AI88 AYUV AIP8 AV12 PLFF NVMD NVDP NVDB SSAA ATOC
Texture formats: 555 1555 4444 565 0888 8888 bump N→∞ (8,8) bump map N→∞ (8,8) FourCC (1TXD) FourCC (2TXD) (3TXD) FourCC FourCC (4TXD) FourCC (5TXD) FourCC (SCVN) FourCC (UHVN) FourCC (SHVN)
Z buffer formats: 16 bit Z 32 bit Z (Z = 32 (0xffffff00) template = 8 (0xff)) (Z = 32 (0xffffff) template = 8 (0xff000000)) 32 bit Z 24 bit Z
modes 16 bits: 800 x 600 1024 x 768 x 1152 864 1176 x 664 1280 x 720 1280 x 768 1280 x 800 1280 x 960 1280 x 1024 1360 x 768 900 1600 x 1024 1600 x 1600 x 1200 1680 x 1050 992 1920 x 1080 x 1768
mode 32 bits: 800 x 600 1024 x 768 x 1152 864 1176 x 664 1280 x 720 1280 x 768 1280 x 800 1280 x 960 1280 x 1024 1360 x 768 900 1600 x 1024 1600 x 1600 x 1200 1680 x 1050 992 1920 x 1080 x 1768
CERTIFIED: No.
DRAWPRIMITIVES2: Yes
DRAWPRIMITIVES2EX: Yes
DRAWPRIMTLVERTEX: Yes
FLIPINTERVAL: Yes
FLIPNOVSYNC: Yes
NO2DDURING3DSCENE: No.
NONLOCALVIDMEM: Yes
NOPAGELOCKREQUIRED: No.
CALIBRATE the GAMMA: No.
PRIMARYGAMMA: Yes
ZBuffer: 16 24
Rendering depth: 16 32
Texture size: 1 x 1 to 8192 x 8192
Maximum U, v coords: 8192.0
Cutting guard :-100000000,-100000000 to 100000000,100000000
AlphaTest NotEqual: Yes
Lack of mixture of the CBC:
Lack of mixture Dest:
Texture AGP: Yes
Texture coords: 8
Mix the steps: 8
The Textures of max: 8
Hardware T & L: Yes
Vertex Blending: 4
Maximum lights: 8
Clip planes: 8
Mix Lightmap: Ok
Mix Specularmap: Ok
Mixture of detail: Ok
Vid linear memory: Yes
SELECTARG1: Yes
SELECTARG2: Yes
ADD: Yes
ADDSIGNED: Yes
SUBTRACT: Yes
MODULATE: Yes
MODULATE2X: Yes
MODULATE4X: Yes
BLENDCURRENTALPHA: Yes
BLENDDIFFUSEALPHA: Yes
BLENDTEXTUREALPHA: Yes
BUMPENVMAP: Yes
BUMPENVMAPLUMINANCE: Yes
DOTPRODUCT3: Yes
ANISOTROPY: Yes
ANTIALIASSORTINDEP: Yes
FOGTABLE: Yes
FOGVERTEX: Yes
FOGRANGE: Yes
WFOG: Yes
WBUFFER: No.
MIPMAPLODBIAS: Yes
WBUFFER: No.
ZBUFFERLESSHSR: No.
MIPNEAREST: Yes
LINEARMIPLINEAR: Yes
DONOTSTRIPELEMENTS: Yes
TEXTURE CLAMP: Yes
BORDER TEXTURE: Yes
MIRROR of TEXTURE: Yes
ALPHAGOURAUDBLEND: Yes
SQUAREONLY: No.
COLORFLATMONO: Yes
COLORGOURAUDMONO: Yes
COLORFLATRGB: Yes
COLORGOURAUDRGB: Yes
SPECULARFLATRGB: Yes
SPECULARGOURAUDRGB: No.
Video device 1
==============
Description: NVIDIA GeForce GT 220
Company / Chipset: nVidia.
Driver file: nvd3dum.dll
Driver size: 9 386 600 bytes
Driver date: 22:55:32 Saturday 4/3/2010
Attributes: Final Version, Private Build
Driver version: 8.17.11.9745
Version: 8.17.11.9745
Hardware ID: 10DE.0A20 (Rev 162, Subsys 0 x 12253842)
Video memory: 2,375,872,512 bytes (2266 Meg)
Mem texture map: 1,034,485,760 bytes (987 Meg)
AGP texture memory: 1,341,386,752 bytes (1279 Meg)
Modes of FourCC: NV12 NV24 YV12, UYVY, YUY2 AI44 AI88 AYUV AIP8 AV12 PLFF NVMD NVDP NVDB SSAA ATOC
Texture formats: 555 1555 4444 565 0888 8888 bump N→∞ (8,8) bump map N→∞ (8,8) FourCC (1TXD) FourCC (2TXD) (3TXD) FourCC FourCC (4TXD) FourCC (5TXD) FourCC (SCVN) FourCC (UHVN) FourCC (SHVN)
Z buffer formats: 16 bit Z 32 bit Z (Z = 32 (0xffffff00) template = 8 (0xff)) (Z = 32 (0xffffff) template = 8 (0xff000000)) 32 bit Z 24 bit Z
modes 16 bits: 800 x 600 1024 x 768 x 1152 864 1176 x 664 1280 x 720 1280 x 768 1280 x 800 1280 x 960 1280 x 1024 1360 x 768 900 1600 x 1024 1600 x 1600 x 1200 1680 x 1050 992 1920 x 1080 x 1768
mode 32 bits: 800 x 600 1024 x 768 x 1152 864 1176 x 664 1280 x 720 1280 x 768 1280 x 800 1280 x 960 1280 x 1024 1360 x 768 900 1600 x 1024 1600 x 1600 x 1200 1680 x 1050 992 1920 x 1080 x 1768
CERTIFIED: No.
DRAWPRIMITIVES2: Yes
DRAWPRIMITIVES2EX: Yes
DRAWPRIMTLVERTEX: Yes
FLIPINTERVAL: Yes
FLIPNOVSYNC: Yes
NO2DDURING3DSCENE: No.
NONLOCALVIDMEM: Yes
NOPAGELOCKREQUIRED: No.
CALIBRATE the GAMMA: No.
PRIMARYGAMMA: Yes
ZBuffer: 16 24
Rendering depth: 16 32
Texture size: 1 x 1 to 8192 x 8192
Maximum U, v coords: 8192.0
Cutting guard :-100000000,-100000000 to 100000000,100000000
AlphaTest NotEqual: Yes
Lack of mixture of the CBC:
Lack of mixture Dest:
Texture AGP: Yes
Texture coords: 8
Mix the steps: 8
The Textures of max: 8
Hardware T & L: Yes
Vertex Blending: 4
Maximum lights: 8
Clip planes: 8
Mix Lightmap: Ok
Mix Specularmap: Ok
Mixture of detail: Ok
Vid linear memory: Yes
SELECTARG1: Yes
SELECTARG2: Yes
ADD: Yes
ADDSIGNED: Yes
SUBTRACT: Yes
MODULATE: Yes
MODULATE2X: Yes
MODULATE4X: Yes
BLENDCURRENTALPHA: Yes
BLENDDIFFUSEALPHA: Yes
BLENDTEXTUREALPHA: Yes
BUMPENVMAP: Yes
BUMPENVMAPLUMINANCE: Yes
DOTPRODUCT3: Yes
ANISOTROPY: Yes
ANTIALIASSORTINDEP: Yes
FOGTABLE: Yes
FOGVERTEX: Yes
FOGRANGE: Yes
WFOG: Yes
WBUFFER: No.
MIPMAPLODBIAS: Yes
WBUFFER: No.
ZBUFFERLESSHSR: No.
MIPNEAREST: Yes
LINEARMIPLINEAR: Yes
DONOTSTRIPELEMENTS: Yes
TEXTURE CLAMP: Yes
BORDER TEXTURE: Yes
MIRROR of TEXTURE: Yes
ALPHAGOURAUDBLEND: Yes
SQUAREONLY: No.
COLORFLATMONO: Yes
COLORGOURAUDMONO: Yes
COLORFLATRGB: Yes
COLORGOURAUDRGB: Yes
SPECULARFLATRGB: Yes
SPECULARGOURAUDRGB: No.
I want to thank each and everyone of you for your input to try to help solve the problems I’ve had with links.
I am happy to report that I played my first round in nearly two weeks in this. Morning. The problem is a corrupted file, .l3. I have a little more 1 100 PoliAnis’ and am not sure which one is, but I can play. I tried whenever I took one of the following folders on until I finally took the PolyAni folder:
WAVs, mops, Custom photos of players, sky, Clubs, PIN code files and finally, all but one of PolyAni files. That after taking all but one of the frequented out of the folder PolyAni links has started without giving me the error of attribution not valid.
Thanks again to you all for your help.
I had a virus, I think.
After three weeks of phone calls to Support Dell trying to fix my computer; attempt to replace/reinstall the Windows 7 operating system and drivers/utilities disks sent by Dell, with two Dell technicians simply disappear for resettlement procedure calls, received installation instructions incorrect when a person remained on the line [except the last guy] and have a supervisor tell me — Dell decided to replace my hard drive.
Are you sure that your virus is really gone?
Replacement operating system disc included all my original applications; but the new hard drive has probably more things. I’m always exploring, troubleshooting and diagnosis.
I downloaded network diagnostic utility. When I run it it doesn’t let me go beyond to find the printer. He wants to be hung with ethernet cable that ain’ will happen. The printer is hooked up to a Dell desktop running Windows 7 is my wife. It works, I’m not playing with this end. fear? Not only needless pain so I don’t understand where it doesn’t. He puts a signal because the configuration of the printer screen says it’s better than only two laptops running Windows 7 can get impression of her. I initially hooked up wireless and this computer (runningXP Pro 32 bit) could get to print a test page. Photos would be would break. Printer is maybe half a page and leave a pin 2 or 3 pages gibberish * beep * and repeat. You could hit the computer host printing and it may begin to print ten minutes or so on the road. While I hit the print button 2 or three times more. This thing was spit out pages of stuff half done half a day later. Price of the Photo book made me he USB wire. I blamed it on slow internet. If we get 20 k, you are having a good day. My apoligies in advance at Leroy and Cush line DSL. It’s all water over the dam, but I am not happy so far. I’m tired and my eyes is burned ash reading web pages and I don’t always know what to do. I typed all the combinations of computer names, network names, ip addresses in each place I know to do and I can’t get XP to recognize. I had a program called hack that I will attach a copy. It means little to me, but more knowledgeable people understand. If anyone can help I would know you more. I have been using flash drives for my impressions, but it would be nice to be able to print a page or two from time to time.
Logfile of Trend Micro HijackThis v2.0.4
Scan saved at 23:45:53, 19/02/2012
Platform: Windows XP SP3 (WinNT 5.01.2600)
MSIE: Internet Explorer v8.00 (8.00.6001.18702)
Boot mode: Normal
1\AVG\AVG2012\avgrsx.exe
C:\Program Files\AVG\AVG2012\avgcsrvx.exe
C:\WINDOWS\system32\winlogon.exe
C:\WINDOWS\system32\services.exe
C:\WINDOWS\system32\lsass.exe
C:\WINDOWS\system32\Ati2evxx.exe
C:\WINDOWS\system32\svchost.exe
C:\Windows\System32\svchost.exe
C:\WINDOWS\system32\Ati2evxx.exe
C:\WINDOWS\system32\spoolsv.exe
C:\Program Files Files\CTAudSvc.exe
Adobe Photoshop elements 7.0\PhotoshopElementsFileAgent.exe C:\Program
C:\Program Files\AVG\AVG2012\avgfws.exe
C:\Program Files\AVG\AVG2012\avgwdsvc.exe
C:\WINDOWS\system32\CTsvcCDA.exe
C:\Program Intel Intel Matrix Storage Manager\Iaantmon.exe
C:\Program Files\Java\jre6\bin\jqs.exe
C:\WINDOWS\System32\ups.exe
C:\Program Files\Fichiers secure AVG Search\vToolbarUpdater\10.0.6\ToolbarUpdater.exe
C:\Program Files\Yahoo!\SoftwareUpdate\YahooAUService.exe
C:\Program Files\AVG\AVG2012\avgnsx.exe
C:\Program Files\AVG\AVG2012\AVGIDSAgent.exe
C:\Program Files\AVG\AVG2012\avgemcx.exe
C:\WINDOWS\Explorer.exe
C:\Program Intel Intel Matrix Storage Manager\Iaanotif.exe
C:\Program Files\Creative\SBAudigy2ZS\Surround Mixer\CTSysVol.exe
C:\WINDOWS\system32\dla\tfswctrl.exe
C:\Program Files\AVG\AVG2012\avgtray.exe
C:\Program Files\Logitech\SetPointP\SetPoint.exe
C:\Program Files\Fichiers Java Update\jusched.exe
C:\Program AVG Search\vprot.exe secure
C:\Program Files\Logitech\Gaming Software\LWEMon.exe
C:\WINDOWS\system32\CTHELPER. EXE
C:\Program Files\Creative\SBAudigy2ZS\DVDAudio\CTDVDDET. EXE
C:\WINDOWS\system32\ctfmon.exe
C:\Program Files\W3i\InstallIQUpdater\InstallIQUpdater.exe
C:\Program Files ATI Technologies ATI. ACE\Core-Static\MOM.exe
C:\Program Files\AVG\AVG2012\avgcsrvx.exe
Utility\RtWLan.exe and C:\Program Realtek USB Wireless LAN Driver
C:\Program Files\Fichiers Files\LogiShrd\KHAL3\KHALMNPR. EXE
C:\Program Files ATI Technologies ATI. ACE\Core-Static\ccc.exe
C:\Documents and Settings\Wayne\Local Settings\Application Data\Google\Chrome\Application\chrome.exe
C:\Documents and Settings\Wayne\Local Settings\Application Data\Google\Chrome\Application\chrome.exe
C:\Documents and Settings\Wayne\Local Settings\Application Data\Google\Chrome\Application\chrome.exe
C:\Documents and Settings\Wayne\Local Settings\Application Data\Google\Chrome\Application\chrome.exe
C:\Documents and Settings\Wayne\Local Settings\Application Data\Google\Chrome\Application\chrome.exe
C:\Documents and Settings\Wayne\Local Settings\Application Data\Google\Chrome\Application\chrome.exe
C:\Documents and Settings\Wayne\Local Settings\Application Data\Google\Chrome\Application\chrome.exe
C:\Documents and Settings\Wayne\Local Settings\Application Data\Google\Chrome\Application\chrome.exe
C:\WINDOWS\system32\NOTEPAD. EXE
C:\Program Trend Micro\HiJackThis\HiJackThis.exe
R1 — HKCU Software Microsoft Internet Explorer Main, Default_Page_URL is http://www.yahoo.com/?fr=fp-yie8
R0 — HKCU Software Microsoft Internet Explorer hand, Start Page = http://www.yahoo.com/?fr=fp-yie8
R1 — HKLM Software Microsoft Internet Explorer Main, Default_Page_URL is http://go.microsoft.com/fwlink/?LinkId=69157
R1 — HKLM Software Microsoft Internet Explorer Main, Default_Search_URL is http://go.microsoft.com/fwlink/?LinkId=54896
R1 — HKLM Software Microsoft Internet Explorer hand, Search Page = http://go.microsoft.com/fwlink/?LinkId=54896
R0 — HKLM Software Microsoft Internet Explorer hand, Start Page = http://go.microsoft.com/fwlink/?LinkId=69157
R0 — HKLM Search Microsoft Internet Explorer, SearchAssistant =
R1 — HKCU Software Microsoft Internet Explorer Main, Window Title = Windows Internet Explorer provided by Yahoo!
R3 — URLSearchHook: (no name) —
O2 — BHO: & Yahoo! Toolbar Helper — <02478D38-C3F9-4efb-9B51-7695ECA05670>— C:\Program Files\Yahoo!\Companion\Installs\cpn\yt.dll
O2 — BHO: WormRadar.com IESiteBlocker.NavFilter — <3CA2F312-6F6E-4B53-A66E-4E65E497C8C0>— C:\Program Files\AVG\AVG2012\avgssie.dll
O2 — BHO: BHO utility IE — <5AB7104A-B71F-49AD-9154-F7F8806AE848>-C:\Program Files\Surf Canyon\surfcanyon.dll
O2 — BHO: DriveLetterAccess — <5CA3D70E-1895-11CF-8E15-001234567890>— C:\WINDOWS\system32\dla\tfswshx.dll
O2 — BHO: AVG Security Toolbar — <95B7759C-8C7F-4BF1-B163-73684A933233>— C:\Program AVG Search\10.0.0.7\AVG sure sure Search_toolbar.dll
O2 — BHO: Google Toolbar Helper —
O2 — BHO: Google Toolbar notify BHO —
O2 — BHO: Java (TM) plug-in 2 SSV Helper —
O2 — BHO: JQSIEStartDetectorImpl —
O2 — BHO: SingleInstance Class —
O3 — Toolbar: Yahoo! Toolbar —
O3 — Toolbar: (no name) —
O3 — Toolbar: AVG Security Toolbar — <95B7759C-8C7F-4BF1-B163-73684A933233>— C:\Program AVG Search\10.0.0.7\AVG sure sure Search_toolbar.dll
O3 — Toolbar: toolbar — <2318C2B1-4965-11d4-9B18-009027A5CD4F>— C:\Program Files\Google\Google GoogleToolbar_32.dll
O4 — HKLM\. \Run: [IAAnotif] C:\Program Intel Intel Matrix Storage Manager\Iaanotif.exe
O4 — HKLM\. \Run: [CTSysVol] C:\Program Files\Creative\SBAudigy2ZS\Surround Mixer\CTSysVol.exe/r
O4 — HKLM\. \Run: [UpdReg] C:\WINDOWS\UpdReg.EXE
O4 — HKLM\. \Run: [dla] C:\WINDOWS\system32\dla\tfswctrl.exe
O4 — HKLM\. \Run: [UpdateManager] «C:\Program Files\Fichiers Sonic Manager\sgtray.exe» / r
O4 — HKLM\. \Run: [AVG_TRAY] «C:\Program Files\AVG\AVG2012\avgtray.exe».
O4 — HKLM\. \Run: [EvtMgr6] C:\Program Files\Logitech\SetPointP\SetPoint.exe /launchGaming
O4 — HKLM\. \Run: [SunJavaUpdateSched] «C:\Program Files\Fichiers Java Update\jusched.exe»
O4 — HKLM\. \Run: [vProt] «C:\Program AVG Secure Search\vprot.exe.
O4 — HKLM\. \Run: [ROC_roc_dec12] «C:\Program AVG Secure Search\ROC_roc_dec12.exe» /PROMPT /CMPID = roc_dec12
O4 — HKLM\. \Run: [start WingMan Profiler] C:\Program Files\Logitech\Gaming Software\LWEMon.exe Noui
O4 — HKLM\. \Run: [StartCCC] «C:\Program Files ATI Technologies ATI.» ACE\Core-Static\CLIStart.exe»MSRun
O4 — HKLM\. \Run: [CTxfiHlp] CTXFIHLP. EXE
O4 — HKLM\. \Run: [CTHelper] CTHELPER. EXE
O4 — HKLM\. \Run: [CTDVDDET] ‘ «C:\Program Files\Creative\SBAudigy2ZS\DVDAudio\CTDVDDET.» » EXE «.
O4 — HKCU\. \Run: [ctfmon.exe] C:\WINDOWS\system32\ctfmon.exe
O4 — HKCU\. \Run: [weather] C:\Program Files\AWS\WeatherBug\Weather.exe 1
O4 — HKCU\. \Run: [Google Update] «C:\Documents and Settings\Wayne\Local Settings\Application Data\Google\Update\GoogleUpdate.exe» / c.
O4 — HKCU\. \Run: [InstallIQUpdater] «C:\Program Files\W3i\InstallIQUpdater\InstallIQUpdater.exe» / / Silent/autorun
O4 — Global Startup: REALTEK USB Wireless LAN Utility.lnk =?
O8 — Extra context menu item: & Options ieSpell — res: / / C:\Program Files\ieSpell\iespell.dll/SPELLOPTION. HTM
O8 — Extra context menu item: Add to Google Photos Screensa & ver — res://C:\WINDOWS\system32\GPhotos.scr/200
O8 — Extra context menu item: spell check & — res: / / C:\Program Files\ieSpell\iespell.dll/SPELLCHECK. HTM
O8 — Extra context menu item: E & xport to Microsoft Excel — res: / / C:\PROGRA
4\OFFICE11\EXCEL. EXE/3000
O8 — Extra context menu item: Google Sidewiki. — res: / / C:\Program Files\Google\Google Toolbar\Component\GoogleToolbarDynamic_mui_en_7461B1589E8B4FB7.dll/cmsidewiki.html
O8 — Extra context menu item: search on Merriam Webster — file://C:\Program Files\ieSpell\Merriam Webster.HTM
O8 — Extra context menu item: search on Wikipedia — file://C:\Program Files\ieSpell\wikipedia. HTM
O9 — Extra button: ieSpell — <0E17D5B7-9F5D-4fee-9DF6-CA6EE38B68A8>— C:\Program Files\ieSpell\iespell.dll
O9 — Extra ‘Tools’ menuitem: ieSpell — <0E17D5B7-9F5D-4fee-9DF6-CA6EE38B68A8>— C:\Program Files\ieSpell\iespell.dll
O9 — Extra button: (no name) — <1606D6F9-9D3B-4aea-A025-ED5B2FD488E7>— C:\Program Files\ieSpell\iespell.dll
O9 — Extra ‘Tools’ menuitem: ieSpell — <1606D6F9-9D3B-4aea-A025-ED5B2FD488E7>— C:\Program Files\ieSpell\iespell.dll Options
O9 — Extra button: research — <92780B25-18CC-41C8-B9BE-3C9C571A8263>— C:\PROGRA
4\OFFICE11\REFIEBAR. DLL
O9 — Extra button: (no name) —
O9 — Extra ‘Tools’ menuitem: @xpsp3res.dll,-20001 —
O9 — Extra button: Messenger —
O9 — Extra ‘Tools’ menuitem: Windows Messenger —
Ø16 — DPF: <0067DBFC-A752-458C-AE6E-B9C7E63D4824>(detection of devices) — http://www.logitech.com/devicedetector/plugins/LogitechDeviceDetection32.cab
Ø16 — DPF: <0E5F0222-96B9-11D3-8997-00104BD12D94>(PCPitstop utility) — http://www.pcpitstop.com/betapit/PCPitStop.CAB
Ø16 — DPF: <1E54D648-B804-468d-BC78-4AFFED8E262F>(System Requirements Lab) — http://www.nvidia.com/content/DriverDownload/srl/3.0.0.4/srl_bin/sysreqlab_nvd.cab
Ø16 — DPF: <6824D897-F7E1-4E41-B84B-B1D3FA4BF1BD>(PCPitstop AntiVirus) — http://utilities.pcpitstop.com/Exterminate2/pcpitstopAntiVirus.dll
Ø16 — DPF: <6E32070A-766D-4EE6-879C-DC1FA91D2FC3>(MUWebControl Class) — http://www.update.microsoft.com/microsoftupdate/v6/V5Controls/en/x86/client/muweb_site.cab?131135804.
Ø16 — DPF: <7417F730-7BAB-409E-8BB7-6936D361B869>(MLauncher class) — http://csweb.netgame.com/main/MLauncher.cab
Ø16 — DPF: <99CAAA27-FA0C-4FA4-B88A-4AB1CC7A17FE>(MGLaunch_v1004 Class) — http://www.netgame.com/mplugin/mglaunch_USAv1005.cab
Ø16 — DPF:
Ø16 — DPF:
Ø16 — DPF:
Ø16 — DPF:
Ø16 — DPF:
O18 — Protocol: linkscanner —
O18 — Protocol: viprotocol —
O22 — SharedTaskScheduler: Preloader Browseui — <438755C2-A8BA-11D1-B96B-00A0C90312E1>— C:\WINDOWS\system32\browseui.dll
O22 — SharedTaskScheduler: component categories — <8C7461EF-2B13-11d2-BE35-3078302C2030>— C:\WINDOWS\system32\browseui.dll cache daemon
O23 — Service: Adobe Active File Monitor V7 (AdobeActiveFileMonitor7.0) — Adobe Systems Incorporated — C:\Program Adobe Photoshop elements 7.0\PhotoshopElementsFileAgent.exe
O23 — Service: Ati HotKey Poller — ATI Technologies Inc. — C:\WINDOWS\system32\Ati2evxx.exe
O23 — Service: AVG Firewall (avgfws) — AVG Technologies CZ, s.r.o. — C:\Program Files\AVG\AVG2012\avgfws.exe
O23 — Service: AVGIDSAgent — AVG Technologies CZ, s.r.o. — C:\Program Files\AVG\AVG2012\AVGIDSAgent.exe
O23 — Service: AVG WatchDog (avgwd) — AVG Technologies CZ, s.r.o. — C:\Program Files\AVG\AVG2012\avgwdsvc.exe
O23 — Service: Creative engine Audio Licensing Service — Creative Labs — C:\Program Files\Fichiers Creative Labs Shared\Service\CTAELicensing.exe
O23 — Service: Service creation of CD-ROM Access — Creative Technology Ltd — C:\WINDOWS\system32\CTsvcCDA.EXE
O23 — Service: creative Audio Service (CTAudSvcService) — Creative Technology Ltd — C:\Program Files Files\CTAudSvc.exe
O23 — Service: FLEXnet Licensing Service — Macrovision Europe Ltd. — C:\Program Files\Common Macrovision FLEXnet Publisher\FNPLicensingService.exe
O23 — Service: Google Update Service (gupdate) (gupdate) — Google Inc. — C:\Program Files\Google\Update\GoogleUpdate.exe
O23 — Service: Google Update Service (gupdatem) (gupdatem) — Google Inc. — C:\Program Files\Google\Update\GoogleUpdate.exe
O23 — Service: Google Software Updater (gusvc) — Google — C:\Program Google Updater\GoogleUpdaterService.exe
O23 — Service: Intel(r) Matrix Storage Event Monitor (IAANTMON) — Intel Corporation — C:\Program Intel Intel Matrix Storage Manager\Iaantmon.exe
O23 — Service: InstallDriver Table Manager (IDriverT) — Macrovision Corporation — C:\Program Files\Fichiers Files\InstallShield\Driver\1150\Intel 32\IDriverT.exe
O23 — Service: Java Quick Starter (JavaQuickStarterService) — Sun Microsystems, Inc. — C:\Program Files\Java\jre6\bin\jqs.exe
O23 — Service: Logitech Bluetooth Service (LBTServ) — Logitech, Inc. — C:\Program Files\Fichiers Files\LogiShrd\Bluetooth\lbtserv.exe
O23 — Service: vToolbarUpdater — Unknown owner — C:\Program Files\Fichiers AVG Secure Search\vToolbarUpdater\10.0.6\ToolbarUpdater.exe
O23 — Service: Yahoo! Updater (YahooAUService) — Yahoo! Inc. — C:\Program Files\Yahoo!\SoftwareUpdate\YahooAUService.exe
—
End of file — 14104 bytes
If the printer is connected USB to the Windows 7 computer, what you can do is share the network (assuming that the XP computer is also connected to the same network). In this way the XP machine can see the printer on Windows 7 computer and install it. The only downside is that the Windows 7 computer must be on for the XP computer can view and print to it. I’ve linked to a site of third party below for instructions on how to do it.
Maybe you are looking for
I have a need to do some very specialized data acquisition that may require special hardware for the building. I would still use LabVIEW as the front end and maybe even wear parts of the interface of the final product. However, I can’t find the docum
How to develop an MDI application as the editor of Visual studio with the MULTI TAB that can be dragged from parent window? I used EnableMDITabbedGroups (true, CMDITabInfo) which creates a multi tabs, but does NOT allow to drag the tab of the window
Hello I developed an application that makes repeated voice calls every 10 seconds. Here’s the code- Import mypackage. MyScreen;Import net.rim.blackberry.api.phone.Phone;Import net.rim.device.api.system.RadioException;Import net.rim.device.api.ui.UiAp
I had Vista installed when I bought the computer, but when I installed my free copy of Windows 7 upgrade it have not migrated user to the new operating system files, and the old files are still there. How can I remove the old files without damaging t
I have some old pc programs cd-rom that will not play on win 7 pro 64-bit. Msg says error 32 bit will not play on my 64-bit computer. I spent hours looking on the net. Help please.
How To Uninstall Logishrd In PC ( Windows 7, 8, 10, and Mac )
Need Space in PC or only want to remove or uninstall Logishrd On PC ( Windows 7, 8, 10, and Mac )? but how to, after it still having files in C: drive? If the application run on the pc, windows 7, 8, & 10 so you can uninstall using Control Panel or CMD Or If this applicaion run in Mac so you know that how to uninstall in MAC. With this article, you will able to delete or kick out all of those files also after uninstalling the Logishrd.
Are you bored, or tired of using Logishrd? Now, wanna kick-off this software from your PC ( Windows 7, 8, 10, and Mac )? There is no condition to follow up before installing, so, you can remove it without getting any confusion about it.
How to uninstall Logishrd In pc ( windows 7, 8, 10, and mac )
There are 10 methods that users can adapt if they want to uninstall Logishrd :
Method #1
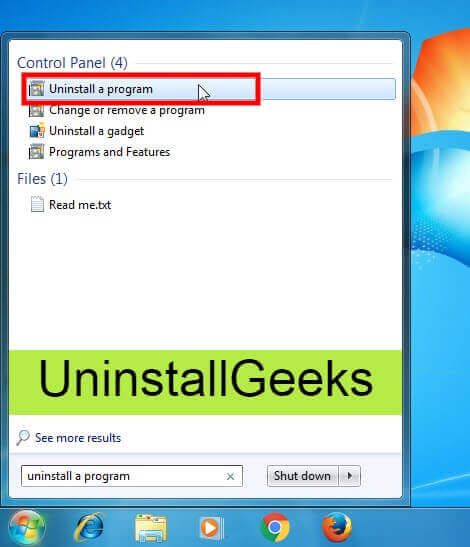
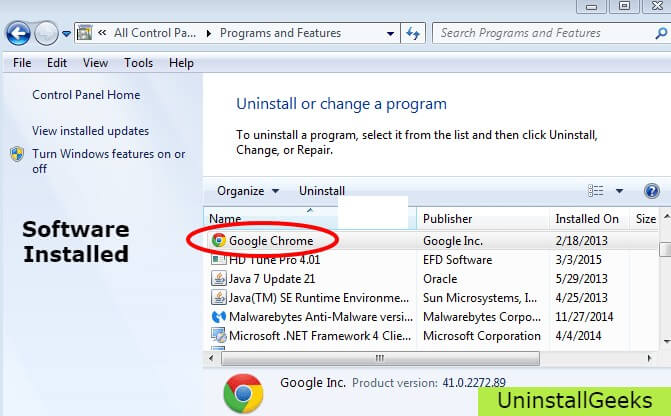
- Go to Start Menu, then click on the Control Panel.
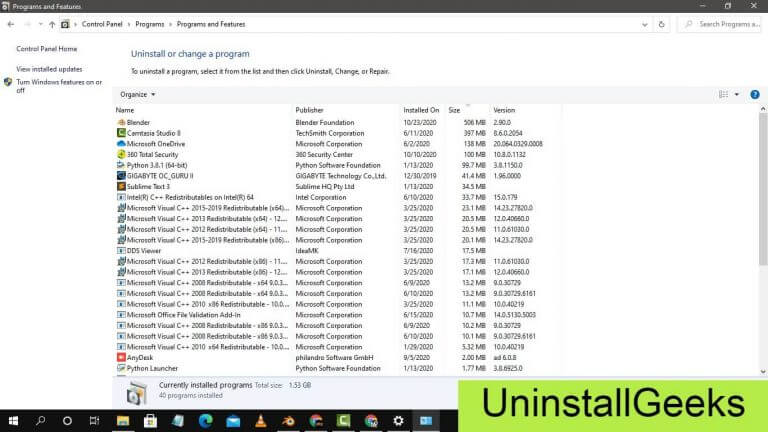
- In Control Panel, under programs, go through the list of the ones that are installed on your computer
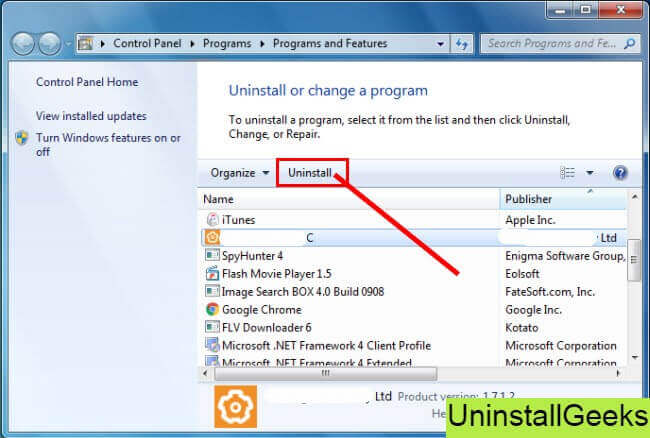
- Right-click on Logishrd, and then click on uninstall a program
- Follow the prompt on the screen, and you will get to see a progress bar that will take you to remove the Logishrd from the computer.
Method #2
The second method involves uninstaller.exe, through which Logishrd can be uninstalled. Just follow the instructions below to execute this step:
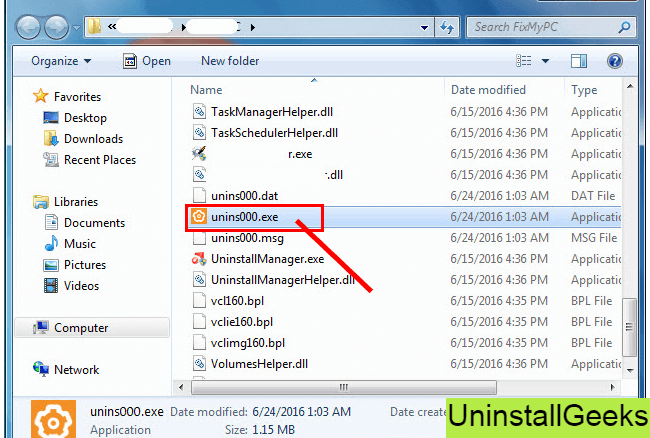
- Go to the installation folder of Logishrd.
- Find a file that is named uninstall.exe or unins000.exe
- Double click on the file, and then follow the instructions that appear on the screen.
Method #3
The third method involves System Restore. For those who don’t know, System Restore is a utility, which helps the user restore their system to its previous state. System Restore removes all those programs, which interfere with the operation and performance of the computer.
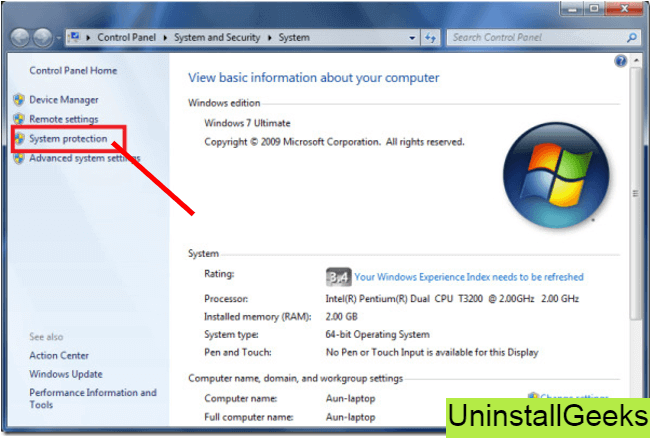
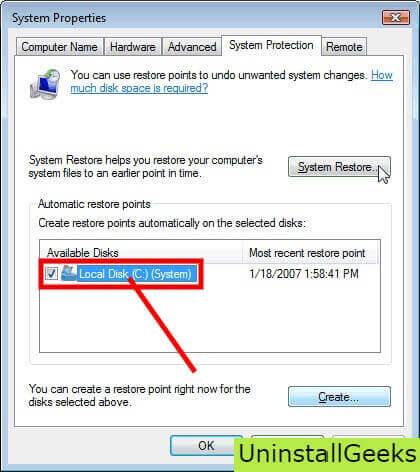
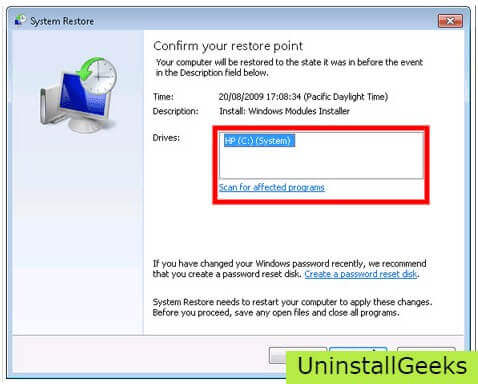
If you have created a system restore point before you installed Logishrd, then you can use this software to restore the system, and remove such unwanted programs. However, before you do so, make sure that you save all the important data.Follow the steps below to know more from this method:
- Close all the files and programs, which are currently running on your PC
- Open Computer from the desktop, and then select Properties
- System Window will open
- On the left side and click on System Protection
- System Properties will open.
- Then do click on the option of System Restore, and a new window will again open.
- Now, choose the ‘different restore point’ option, and click on Next.
- You have to select a date and time from the given options; when you select a date, the drivers that you installed after the chosen date won’t work.
- Click on Finish and then Confirm the ‘Restore Point’ on the screen.
- When you click Yes to confirm, the Logishrd would be uninstalled.
Method #4
If you have an antivirus, then you can use it to uninstall Logishrd.There is much malware or Logishrd software in the computer applications that we download nowadays. They have become very difficult to remove from the system, like Trojan and spyware.
- If you cannot remove Logishrd with the above methods.
- It means that there is malware or Logishrd in it, and only a good antivirus can be used for removing it.
You can either download Norton Antivirus or AVG antivirus, as these are reputable software and will surely remove the malware, Logishrd on the system. 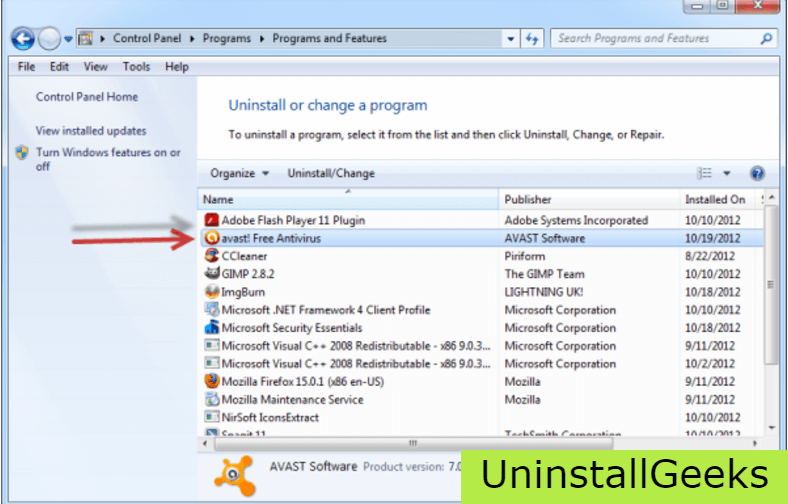
Method #5
If you want to uninstall Logishrd, then you can do so using Command Displayed in the Registry. A registry is a place where all the settings of Windows, along with information, are stored. This also includes the command to uninstall a software or program.
You can try this method with Logishrd as well, but it is a very risky method. If you make any mistake and delete the wrong information, then the system is most likely to crash. It would become difficult for you to bring it back from deletion.
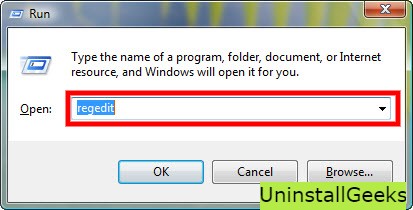
To execute this method, To follow the steps given below:
- Hold Windows + R together, and then Run command
- When the command box opens, type Regedit in the box and then click on OK
- You have to navigate and find the registry key for the Logishrd
- You will see an uninstall string on the next window; double click on it, and also copy ‘Value Data’
- Again hold Windows + R keys, and run the Command; paste the value data that you just copy and click on OK
Follow what comes on the screen and then uninstall Logishrd.
Method #6
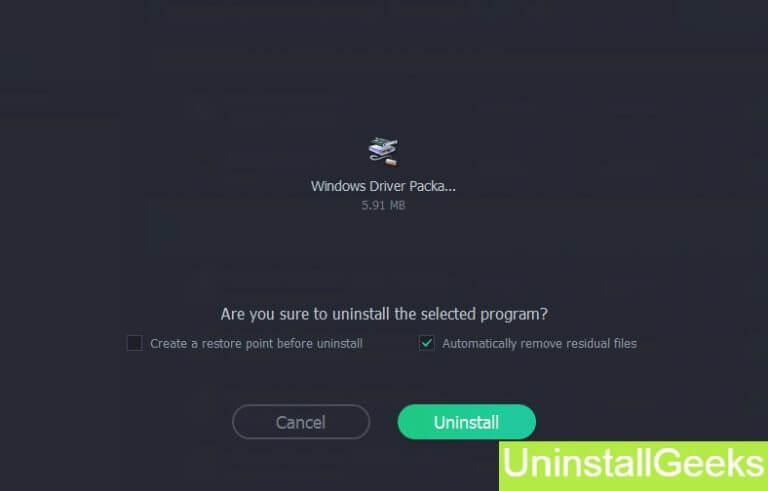
The seventh method is to uninstall the Logishrd using a third-party uninstaller.
At times, those who don’t have any knowledge of computer language, won’t be able to manually uninstall the software fully.
Many files occupy the hard disk of the computer, so it is best to use third-party software to uninstall them.
Method #7
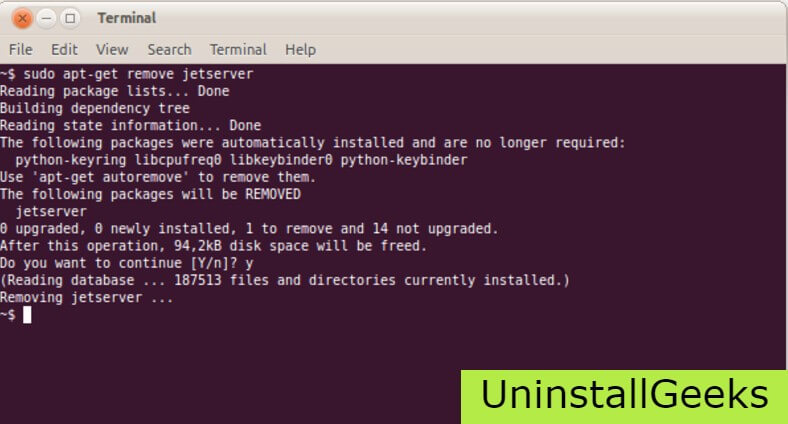
There are some codes that users can type into the command prompt, and they would be able to uninstall the Logishrd. For example, if they want to remove the package, then just type.
sudo apt-get remove Logishrd
If you want to uninstall Logishrd and its dependencies as well, then type:
sudo apt-get remove –auto-remove Logishrd
For those who don’t know, some of the dependencies of Logishrd are GCC-5, libc6, libgcc1, Logishrd dev, and gc++-5.
Method #8
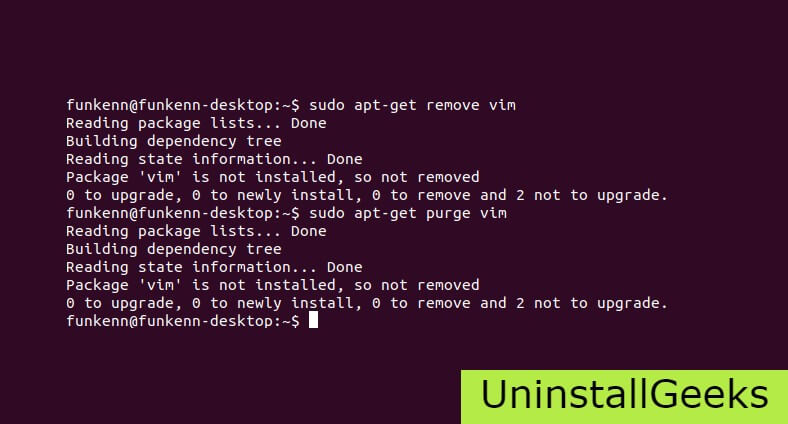
If the user wants to remove the configuration and data files of Logishrd, then they need to run the following code on the Command Prompt:
sudo apt-get purge Logishrd
Method # 9
It depends on you that are you willing to kick-out the data or you want to remove the configuration data or data files, along with the dependencies, then the following code is most likely to work for you:
sudo apt-get auto-remove -purge Logishrd
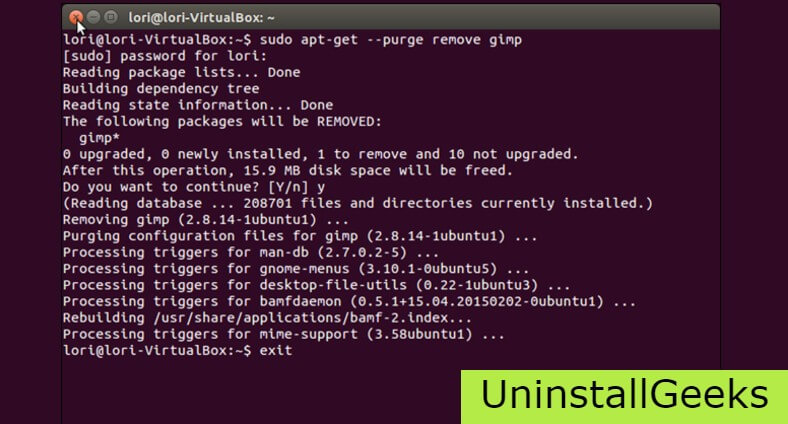
To uninstall Logishrd on mac because anytime we need space or only want to remove from pc due to some viruses and also many problems which are needed to remove or uninstall from pc.
So I will show you some steps of uninstalling Logishrd on the mac so follow my this step or method if you have still confusion so you may contact with us for uninstall of Logishrd on pc or mac.
How to Uninstall Logishrd on Mac?
For uninstalling Logishrd on the mac so as I told you that there is a simple method to uninstall apps on mac. As there are installed some apps on your Mac and now you want to remove or uninstall from your pc successfully and want to install some other apps on my mac so follow my these steps to uninstall Logishrd on mac.
Method #1
In method 1, you have to open mac on your pc as I’m showing in the image follow the images to uninstall Logishrd on your mac.
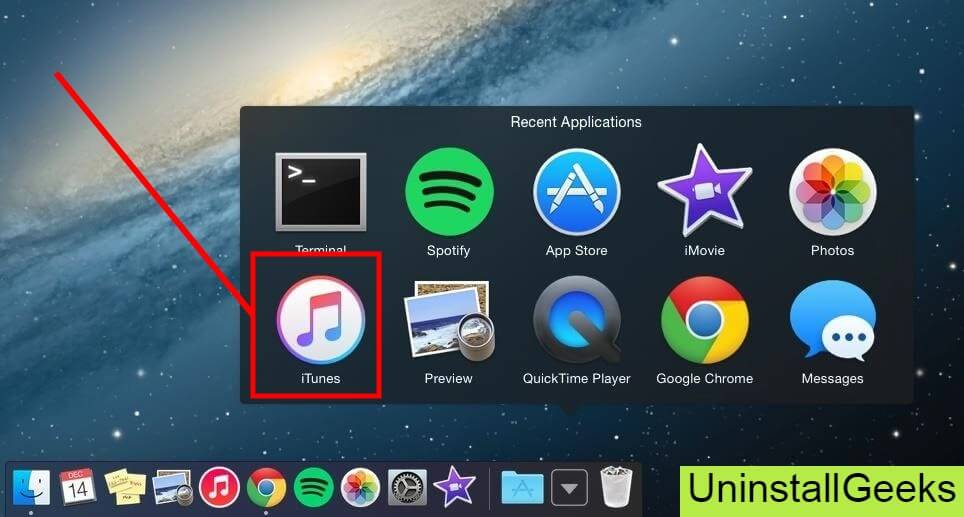
In the image, there is a Logishrd app on your mac dashboard and now we have to uninstall it from our mac we will uninstall this app and will remove it in of mac now double-click-on-app showing in the image.
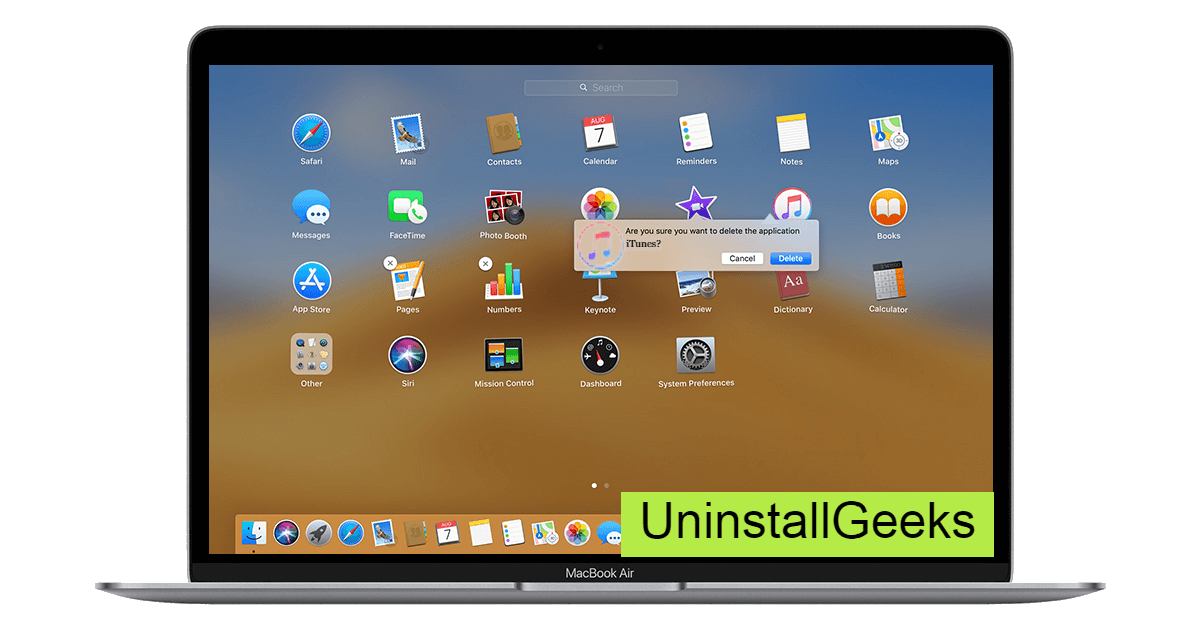
Now you double-clicked on the app mac will ask that are you sure to uninstall Logishrd click on the Delete button so go to Trash of mac to uninstall completely from mac. Showing in image trash bin click on trash bin and go inside there will be Logishrd which we had to delete before so have to uninstall completely from mac.
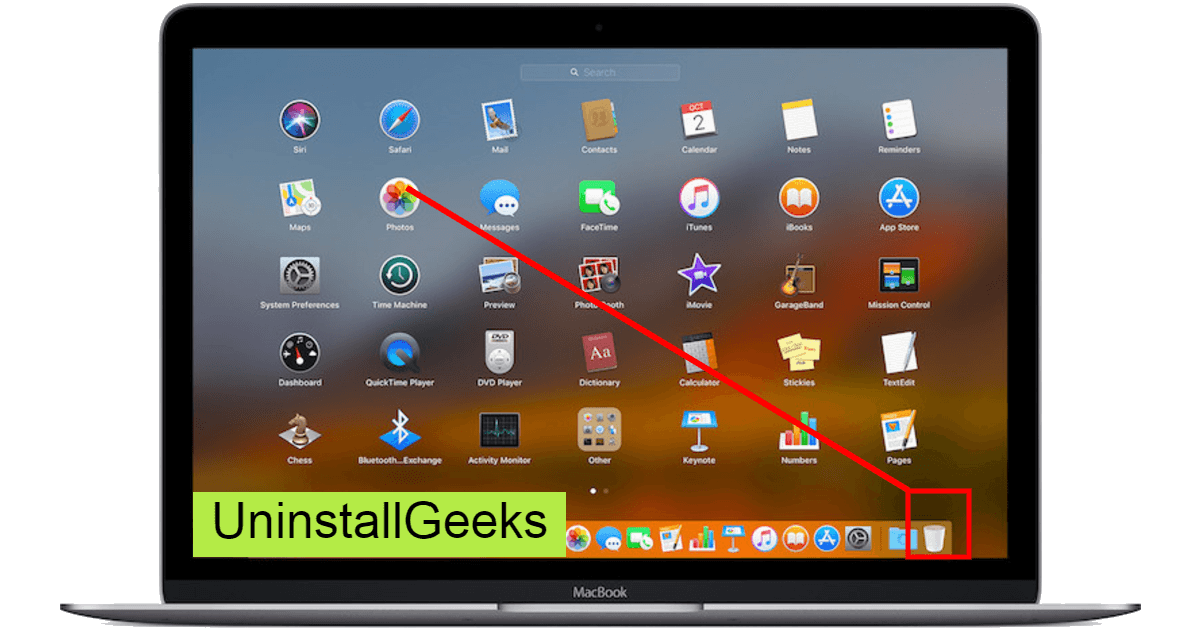
Not right-click on trash to remove all data or app which we had uninstalled before seeing in the image. Click on Empty Trash the whole data which is in the trash will auto remove successfully.
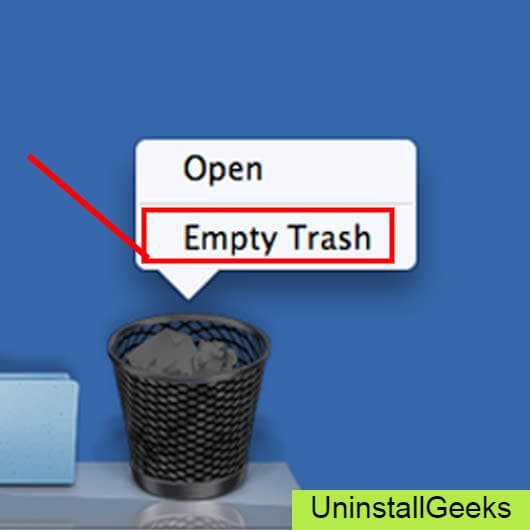
Now we uninstalled Logishrd on the mac so as you see that how to uninstall or remove any app on the mac so if you liked this so share once. This method doesn’t require any antivirus or uninstaller software from them we are to uninstall.
I described only a simple method of uninstalling Logishrd on mac. This method more people are using but some people take it is too hard uninstalling in mac but in this step, anyone can understand this simple method.
How To Install?
For those who don’t know much about Logishrd, they might lean more towards uninstalling it. These Logishrd create an environment, where users can create a high GPU-accelerated application. If you want to install this Logishrd, then make sure that your system is compatible with it.
Firstly, verify that the system you are using has a Logishrd capable GPU, and then download the Logishrd. Install it, and then test that the software runs smoothly on the system. If it doesn’t run smoothly, then it could be because its communication with the hardware is corrupted.
Conclusion
There are other methods of uninstalling the Logishrd as well as in pc or windows, but these could be difficult for those, who don’t have much technical expertise. Execute these methods, and they will surely work. These methods don’t require the user to have much knowledge of the technical side of an operating system. They can follow simple steps and uninstall Logishrd.
Что такое KHALMNPR.exe? Это безопасно или вирус? Как удалить или исправить это
KHALMNPR.exe это исполняемый файл, который является частью CDDRV_Installer Программа, разработанная Logitech Inc., Программное обеспечение обычно о 4.02 MB по размеру.
Расширение .exe имени файла отображает исполняемый файл. В некоторых случаях исполняемые файлы могут повредить ваш компьютер. Пожалуйста, прочитайте следующее, чтобы решить для себя, является ли KHALMNPR.exe Файл на вашем компьютере — это вирус или троянский конь, который вы должны удалить, или это действительный файл операционной системы Windows или надежное приложение.
KHALMNPR.exe безопасный или это вирус или вредоносное ПО?
Первое, что поможет вам определить, является ли тот или иной файл законным процессом Windows или вирусом, это местоположение самого исполняемого файла. Например, такой процесс, как KHALMNPR.exe, должен запускаться из C: \ Program Files \ Common Files \ Logishrd \ CDDRV2 \ KHALMNPR.exe и нигде в другом месте.
Для подтверждения откройте диспетчер задач, выберите «Просмотр» -> «Выбрать столбцы» и выберите «Имя пути к изображению», чтобы добавить столбец местоположения в диспетчер задач. Если вы обнаружите здесь подозрительный каталог, возможно, стоит дополнительно изучить этот процесс.
Еще один инструмент, который иногда может помочь вам обнаружить плохие процессы, — это Microsoft Process Explorer. Запустите программу (не требует установки) и активируйте «Проверить легенды» в разделе «Параметры». Теперь перейдите в View -> Select Columns и добавьте «Verified Signer» в качестве одного из столбцов.
Если статус процесса «Проверенная подписывающая сторона» указан как «Невозможно проверить», вам следует взглянуть на процесс. Не все хорошие процессы Windows имеют метку проверенной подписи, но ни один из плохих.
Наиболее важные факты о KHALMNPR.exe:
- Находится в C: \ Program Files \ Common Files \ Logishrd \ CDDRV2 \ вложенная;
- Издатель: Logitech Inc.
- Полный путь: C: \ Program Files \ Common Files \ Logishrd \ CDDRV2 \ KHALMNPR.exe
- Файл справки:
- URL издателя: www.logitech.com
- Известно, что до 4.02 MB по размеру на большинстве окон;
Если у вас возникли какие-либо трудности с этим исполняемым файлом, перед удалением KHALMNPR.exe вы должны определить, заслуживает ли он доверия. Для этого найдите этот процесс в диспетчере задач.
Найдите его местоположение (оно должно быть в C: \ Program Files \ Common Files \ Logishrd \ CDDRV2 \) и сравните размер и т. Д. С приведенными выше фактами.
Если вы подозреваете, что можете быть заражены вирусом, вы должны немедленно попытаться это исправить. Чтобы удалить вирус KHALMNPR.exe, необходимо Загрузите и установите приложение полной безопасности, например Malwarebytes., Обратите внимание, что не все инструменты могут обнаружить все типы вредоносных программ, поэтому вам может потребоваться попробовать несколько вариантов, прежде чем вы добьетесь успеха.
Кроме того, функциональность вируса может сама влиять на удаление KHALMNPR.exe. В этом случае вы должны включить Безопасный режим с загрузкой сетевых драйверов — безопасная среда, которая отключает большинство процессов и загружает только самые необходимые службы и драйверы. Когда вы можете запустить программу безопасности и полный анализ системы.
Могу ли я удалить или удалить KHALMNPR.exe?
Не следует удалять безопасный исполняемый файл без уважительной причины, так как это может повлиять на производительность любых связанных программ, использующих этот файл. Не забывайте регулярно обновлять программное обеспечение и программы, чтобы избежать будущих проблем, вызванных поврежденными файлами. Что касается проблем с функциональностью программного обеспечения, проверяйте обновления драйверов и программного обеспечения чаще, чтобы избежать или вообще не возникало таких проблем.
Согласно различным источникам онлайн, 9% людей удаляют этот файл, поэтому он может быть безвредным, но рекомендуется проверить надежность этого исполняемого файла самостоятельно, чтобы определить, является ли он безопасным или вирусом. Лучшая диагностика для этих подозрительных файлов — полный системный анализ с Защитить, Если файл классифицируется как вредоносный, эти приложения также удаляют KHALMNPR.exe и избавляются от связанных вредоносных программ.
Однако, если это не вирус, и вам нужно удалить KHALMNPR.exe, вы можете удалить CDDRV_Installer с вашего компьютера, используя его деинсталлятор, который должен находиться по адресу: MsiExec.exe / I <0C826C5B-B131-423A-A229-CUMNUMX-CUMNUMX-CUMNUMX >. Если вы не можете найти его деинсталлятор, то вам может потребоваться удалить CDDRV_Installer, чтобы полностью удалить KHALMNPR.exe. Вы можете использовать функцию «Установка и удаление программ» на панели управления Windows.
- 1. в Меню Пуск (для Windows 8 щелкните правой кнопкой мыши в нижнем левом углу экрана), нажмите Панель управления, а затем под Программы:
o Windows Vista / 7 / 8.1 / 10: нажмите Удаление программы.
o Windows XP: нажмите Установка и удаление программ.
- 2. Когда вы найдете программу CDDRV_Installerщелкните по нему, а затем:
o Windows Vista / 7 / 8.1 / 10: нажмите Удалить.
o Windows XP: нажмите Удалить or Изменить / Удалить вкладка (справа от программы).
- 3. Следуйте инструкциям по удалению CDDRV_Installer.
Распространенные сообщения об ошибках в KHALMNPR.exe
Наиболее распространенные ошибки KHALMNPR.exe, которые могут возникнуть:
• «Ошибка приложения KHALMNPR.exe.»
• «Ошибка KHALMNPR.exe».
• «Возникла ошибка в приложении KHALMNPR.exe. Приложение будет закрыто. Приносим извинения за неудобства».
• «KHALMNPR.exe не является допустимым приложением Win32».
• «KHALMNPR.exe не запущен».
• «KHALMNPR.exe не найден».
• «Не удается найти KHALMNPR.exe.»
• «Ошибка запуска программы: KHALMNPR.exe.»
• «Неверный путь к приложению: KHALMNPR.exe.»
Эти сообщения об ошибках .exe могут появляться во время установки программы, во время выполнения связанной с ней программы CDDRV_Installer, во время запуска или завершения работы Windows или даже во время установки операционной системы Windows. Отслеживание момента появления ошибки KHALMNPR.exe является важной информацией, когда дело доходит до устранения неполадок.
Как исправить KHALMNPR.exe
Аккуратный и опрятный компьютер — это один из лучших способов избежать проблем с CDDRV_Installer. Это означает выполнение сканирования на наличие вредоносных программ, очистку жесткого диска cleanmgr и ПФС / SCANNOWудаление ненужных программ, мониторинг любых автозапускаемых программ (с помощью msconfig) и включение автоматических обновлений Windows. Не забывайте всегда делать регулярные резервные копии или хотя бы определять точки восстановления.
Если у вас возникла более серьезная проблема, постарайтесь запомнить последнее, что вы сделали, или последнее, что вы установили перед проблемой. Использовать resmon Команда для определения процессов, вызывающих вашу проблему. Даже в случае серьезных проблем вместо переустановки Windows вы должны попытаться восстановить вашу установку или, в случае Windows 8, выполнив команду DISM.exe / Online / Очистка-изображение / Восстановить здоровье, Это позволяет восстановить операционную систему без потери данных.
Чтобы помочь вам проанализировать процесс KHALMNPR.exe на вашем компьютере, вам могут пригодиться следующие программы: Менеджер задач безопасности отображает все запущенные задачи Windows, включая встроенные скрытые процессы, такие как мониторинг клавиатуры и браузера или записи автозапуска. Единый рейтинг риска безопасности указывает на вероятность того, что это шпионское ПО, вредоносное ПО или потенциальный троянский конь. Это антивирус обнаруживает и удаляет со своего жесткого диска шпионское и рекламное ПО, трояны, кейлоггеры, вредоносное ПО и трекеры.
Обновлен сентябрь 2023:
Мы рекомендуем вам попробовать это новое программное обеспечение, которое исправляет компьютерные ошибки, защищает их от вредоносных программ и оптимизирует производительность вашего ПК. Этот новый инструмент исправляет широкий спектр компьютерных ошибок, защищает от таких вещей, как потеря файлов, вредоносное ПО и сбои оборудования.
- Шаг 1: Скачать PC Repair & Optimizer Tool (Windows 10, 8, 7, XP, Vista — Microsoft Gold Certified).
- Шаг 2: Нажмите «Начать сканирование”, Чтобы найти проблемы реестра Windows, которые могут вызывать проблемы с ПК.
- Шаг 3: Нажмите «Починить все», Чтобы исправить все проблемы.
(дополнительное предложение для Fortect)