[РЕШЕНО] Trojan:Win64/DisguisedXMRigMiner
Подскажите, пожалуйста, как удалить вирус HEUR:Trojan.Win32.Miner.gen?
При запуске KVRT или dr web Curlet, обнаруживается вирус, но после перезагрузки все возвращается обратно. Также пробовал загружать из безопасного режима, ничего не меняется.
Каким-то образом на совершенно новом компе поймала майнер. Либо при активации винды через KMS Auto, либо вероятнее при установке драйверов (Win Defender нашел Realtek HD, который маскируется под звуковую карту?).
Изначально самопроизвольно закрывалась папка Program Data, файл hosts, браузер при попытке захода на сайты антивирусов или с описаниями вирусов. Через безопасный режим установила Kaspersky Virus Removal Tool и через него удалила вирусы.
После еще прогоняла DrWeb’ом и другими утилитами, тоже что-то удалили. Попробовала поставить Аваст, но он не устанавливается, выдает «ошибку 5 отказано в доступе» и Ошибка 5 ae_unknown.
Прилагаю логи с FRST и скан с Касперского
Trojan:Win64/DisguisedXMRigMiner – XMRig Trojan
If you encounter a message indicating the presence of the Trojan:Win64/DisguisedXMRigMiner on your PC or if your computer is noticeably slow and causing you numerous frustrations, it is crucial to take action and scan your system for the Disguised XMRig Miner. I will now guide you on how to proceed with the scanning and cleaning process in an effective manner.
The majority of Disguised XMRig Miners are used to earn a profit on you. The criminals elaborate the range of dangerous programs to take your credit card information, online banking credentials, as well as various other facts for deceptive purposes.
Trojan:Win64/DisguisedXMRigMiner Summary
- Creates RWX memory;
- Reads data out of its own binary image;
- A process created a hidden window;
- Drops a binary and executes it;
- Unconventionial language used in binary resources: Russian;
- Creates an autorun.inf file;
- Uses Windows utilities for basic functionality;
- Installs itself for autorun at Windows startup;
- Network activity detected but not expressed in API logs;
- Attempts to disable Windows Defender;
- Anomalous binary characteristics;
- Ciphering the documents situated on the target’s disk drive — so the target can no more use the data;
- Preventing regular access to the target’s workstation;
File details
Trojan:Win64/DisguisedXMRigMiner also known as:
| GridinSoft | Trojan.XMRMiner |
| K7AntiVirus | Trojan ( 00560c521 ) |
| DrWeb | Tool.Nssm.6 |
| Cynet | Malicious (score: 99) |
| CAT-QuickHeal | Trojan.Win32 |
| ALYac | Trojan.Miner.DZ |
| Cylance | Unsafe |
| Sangfor | Trojan.Win32.Miner.gen |
| CrowdStrike | win/malicious_confidence_60% (W) |
| Alibaba | Trojan:Win64/Miners.d33b97b1 |
| K7GW | Trojan ( 00560c521 ) |
| Cybereason | malicious.decee3 |
| Cyren | W64/Application.FTAD-2956 |
| Symantec | ML.Attribute.HighConfidence |
| ESET-NOD32 | a variant of Win64/CoinMiner.PO potentially unwanted |
| APEX | Malicious |
| Avast | Win64:CoinminerX-gen [Trj] |
| ClamAV | Win.Trojan.Miner-9843125-0 |
| Kaspersky | HEUR:Trojan.Win32.Miner.gen |
| BitDefender | Trojan.Miner.DZ |
| NANO-Antivirus | Trojan.Win64.Miner.iiogib |
| MicroWorld-eScan | Trojan.Miner.DZ |
| Tencent | Win32.Trojan.Miner.Lpbd |
| Ad-Aware | Trojan.Miner.DZ |
| Sophos | Generic PUA KE (PUA) |
| Comodo | ApplicUnwnt@#31tr98nuo1hwg |
| BitDefenderTheta | Gen:NN.ZelphiCO.34294.cnKfaehV8aci |
| VIPRE | Trojan.Win32.Generic!BT |
| TrendMicro | TROJ_GEN.R002C0WDJ21 |
| McAfee-GW-Edition | BehavesLike.Win32.BadFile.vc |
| FireEye | Generic.mg.ab919222dd0d6f41 |
| Emsisoft | Trojan.Miner.DZ (B) |
| SentinelOne | Static AI – Malicious PE |
| Jiangmin | Trojan.Miner.ouv |
| Webroot | W32.Trojan.Miner |
| Avira | HEUR/AGEN.1136970 |
| eGambit | Unsafe.AI_Score_99% |
| Antiy-AVL | Trojan/Generic.ASMalwS.315D6B9 |
| Microsoft | Trojan:Win64/DisguisedXMRigMiner |
| GData | Trojan.Miner.DZ |
| McAfee | Artemis!AB919222DD0D |
| MAX | malware (ai score=89) |
| VBA32 | Trojan.Miner |
| Malwarebytes | Malware.AI.1121623471 |
| Panda | Trj/CI.A |
| TrendMicro-HouseCall | TROJ_GEN.R002C0WDJ21 |
| Yandex | Trojan.Miner!yZ/k+zfelIw |
| Ikarus | Trojan.Win64.CoinMiner |
| MaxSecure | Trojan-Ransom.Win32.Crypmod.zfq |
| Fortinet | W32/CoinMiner.FQ!tr |
| AVG | Win64:CoinminerX-gen [Trj] |
| Paloalto | generic.ml |
Does your antivirus regularly report about the “Disguised XMRig Miner”?
If you have actually seen a message suggesting the “Trojan:Win64/DisguisedXMRigMiner found”, then it’s an item of good news! The pc virus “Trojan:Win64/DisguisedXMRigMiner” was identified and also, most likely, erased. Such messages do not suggest that there was an actually active Disguised XMRig Miner on your tool. You might have simply downloaded a data that contained Trojan:Win64/DisguisedXMRigMiner, so your antivirus software program instantly erased it prior to it was introduced and created the difficulties. Conversely, the malicious script on the infected site could have been spotted and also stopped before triggering any kind of problems.
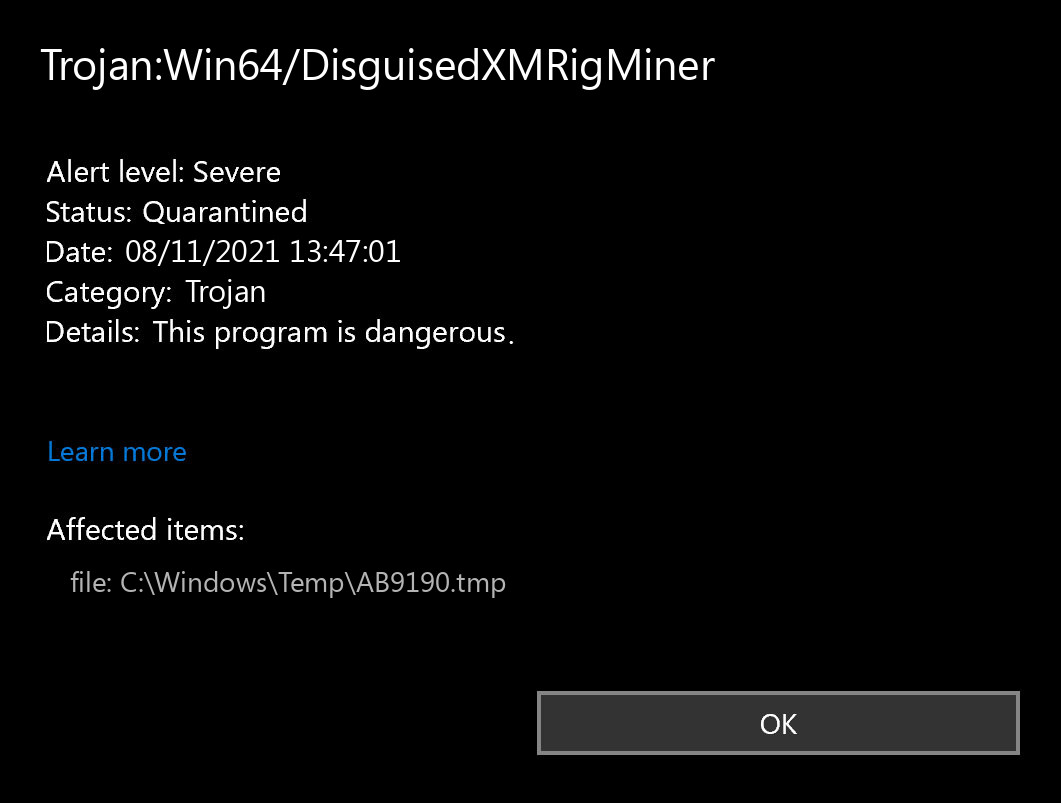
Microsoft Defender: “Trojan:Win64/DisguisedXMRigMiner”
When your computer system displays the message “Trojan:Win64/DisguisedXMRigMiner Found,” it does not necessarily mean that the Disguised XMRig Miner has successfully achieved its objective. Instead, it indicates that you may have visited an infected webpage or downloaded a malicious file. It is advisable to avoid such situations in the future, but there is no need to panic excessively. You can take the following steps to gather more information and address the issue:
1. Open your antivirus program and check the detection log file for Trojan:Win64/DisguisedXMRigMiner. This log file will provide you with additional details about the specific Disguised XMRig Miner that was detected and the actions taken by your antivirus software.
2. If you are still unsure or want to be more thorough, perform a manual scan using your antivirus software. This will help in further identifying and addressing any potential threats.
How to scan for malware, spyware, ransomware, adware, and other threats.
If your computer is operating unusually slow, websites are opening in a strange manner, or you’re encountering unexpected advertisements, it is possible that your computer has been infected and a virus is actively causing these issues. Spyware can track your activities and redirect your search or home pages to undesired locations. Adware can infect your browser and even the entire Windows OS, while ransomware attempts to lock your system and extort a significant ransom for your own files.
Regardless of the nature of the problem with your PC, the first step is to scan it using Gridinsoft Anti-Malware. This powerful tool is designed to detect and remove various threats from your computer. It goes beyond the capabilities of a simple antivirus software, specifically targeting modern threats. Gridinsoft Anti-Malware is currently the only application available that can effectively clean your PC from spyware and other viruses that often go undetected by regular antivirus programs.
To get started, download and install Gridinsoft Anti-Malware from their official website. Once installed, launch the program and perform a thorough scan of your computer. The software will guide you through the system cleanup process. It’s important to note that you don’t need to purchase a license to clean your PC, as the initial license provides a six-day fully functional free trial. However, if you want to protect yourself from future threats, it is recommended to consider purchasing a license. This will ensure that your computer remains free from infections in the long run.
How to scan your PC for Trojan:Win64/DisguisedXMRigMiner?
To check your system for Disguised XMRig Miner as well as to get rid of all identified malware, you need to find an antivirus. The current versions of Windows include Microsoft Defender — the integrated antivirus by Microsoft. Microsoft Defender is typically fairly great, nonetheless, it’s not the only point you need to get. In our point of view, the very best antivirus software is to use Microsoft Defender in combination with Gridinsoft.
In this manner, you may obtain facility defense versus the selection of malware. To check for viruses in Microsoft Defender, open it and start a new examination. It will completely check your PC for infections. And also, obviously, Microsoft Defender operates in the background by default. The tandem of Microsoft Defender and also Gridinsoft will certainly set you free of most of the malware you might ever before encounter. Consistently arranged scans may likewise secure your system in the future.
Use Safe Mode to fix the most complex Trojan:Win64/DisguisedXMRigMiner issues.
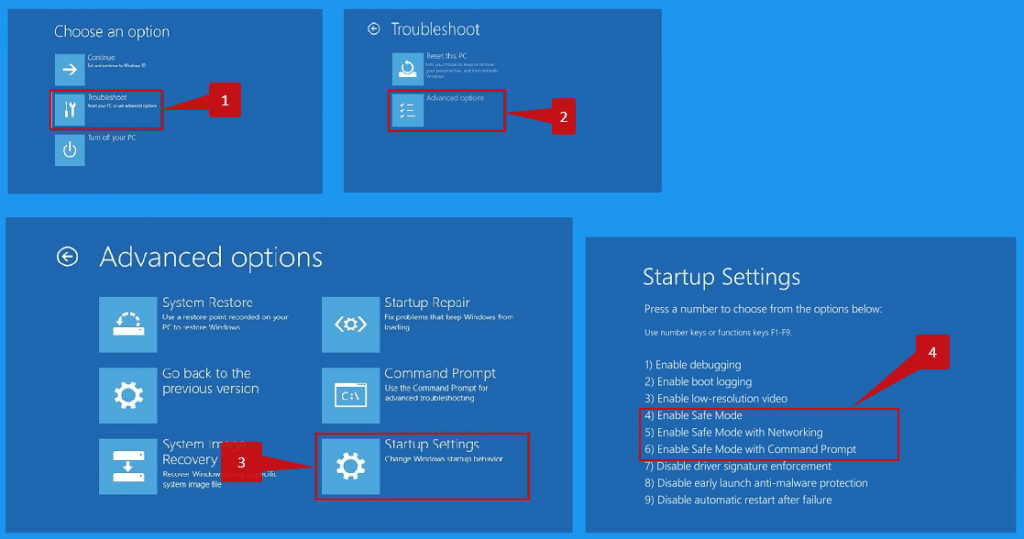
If you have Trojan:Win64/DisguisedXMRigMiner type that can barely be eliminated, you might require to think about scanning for malware past the typical Windows functionality. For this objective, you need to start Windows in Safe Mode, therefore avoiding the system from loading auto-startup items, potentially including malware. Start Microsoft Defender examination and after that scan with Gridinsoft in Safe Mode. This will help you uncover the viruses that can not be tracked in the routine mode.
Use Gridinsoft to remove Disguised XMRig Miner and other junkware.
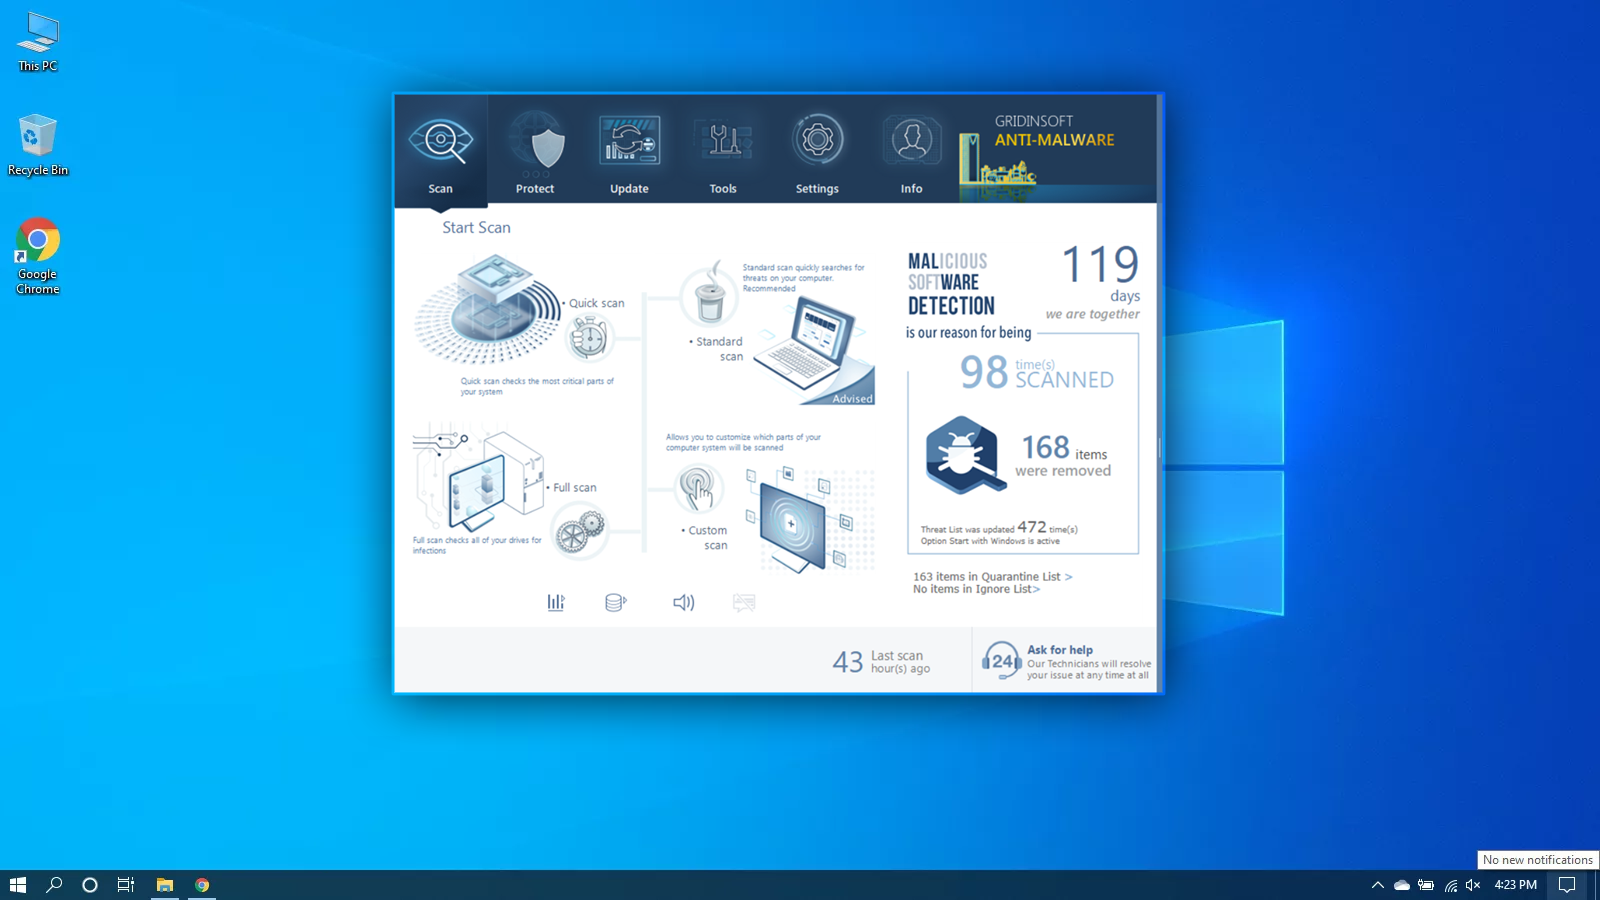
It’s not enough to simply use the antivirus for the safety and security of your device. You need to have an extra comprehensive antivirus solution. Not all malware can be detected by typical antivirus scanners that primarily look for virus-type hazards. Your system may be full of “junk”, for example, toolbars, internet browser plugins, dubious online search engines, bitcoin-miners, as well as other types of unwanted software used for generating income on your lack of experience. Beware while downloading and install software on the web to avoid your device from being filled with unwanted toolbars as well as various other junk data.
Nonetheless, if your system has already got a particular unwanted application, you will make your mind to delete it. Most of the antivirus programs are do not care concerning PUAs (potentially unwanted applications). To eliminate such programs, I suggest purchasing Gridinsoft Anti-Malware. If you use it occasionally for scanning your computer, it will assist you to get rid of malware that was missed by your antivirus program.
Frequently Asked Questions
�� How Do I Know My Windows 10 PC Has Trojan:Win64/DisguisedXMRigMiner?
- Computer is very slow.
- Applications take too long to start.
- Computer keeps crashing.
- Your friends receive spam messages from you on social media.
- You see a new extension that you did not install on your Chrome browser.
- Internet connection is slower than usual.
- Your computer fan starts up even when your computer is on idle.
- You are now seeing a lot of pop-up ads.
- You receive antivirus notifications.
Take note that the symptoms above could also arise from other technical reasons. However, just to be on the safe side, we suggest that you proactively check whether you do have malicious software on your computer. One way to do that is by running a malware scanner.
�� How to scan my PC with Microsoft Defender?
- Open Windows Settings. The easiest way is to click the start button and then the gear icon. Alternately, you can press the Windows key + i on your keyboard.
- Click on Update & Security
- From here, you can see if your PC has any updates available under the Windows Update tab. This is also where you will see definition updates for Windows Defender if they are available.
- Select Windows Security and then click the button at the top of the page labeled Open Windows Security.
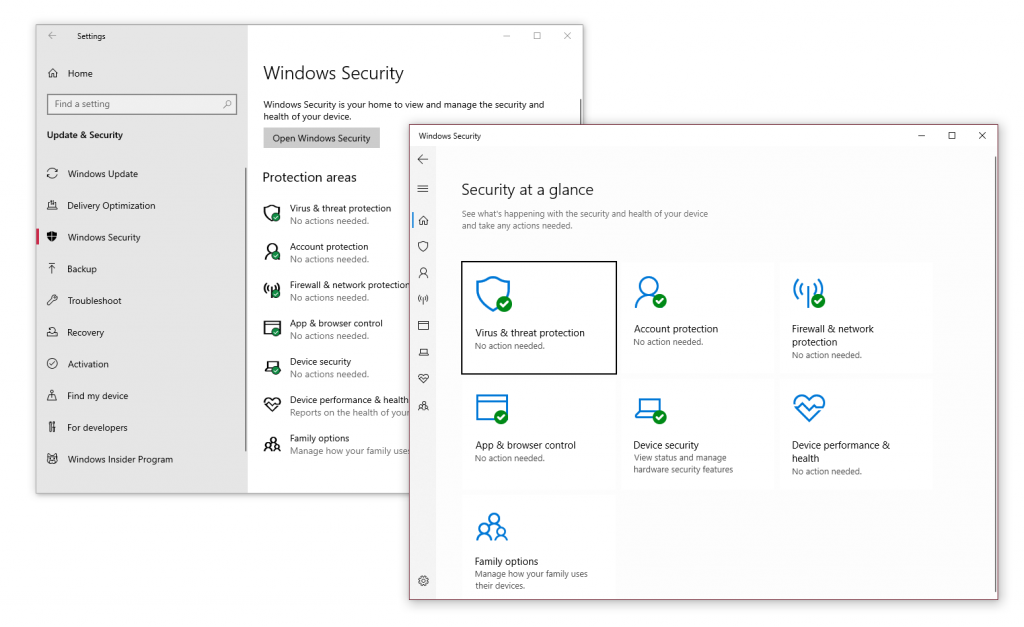
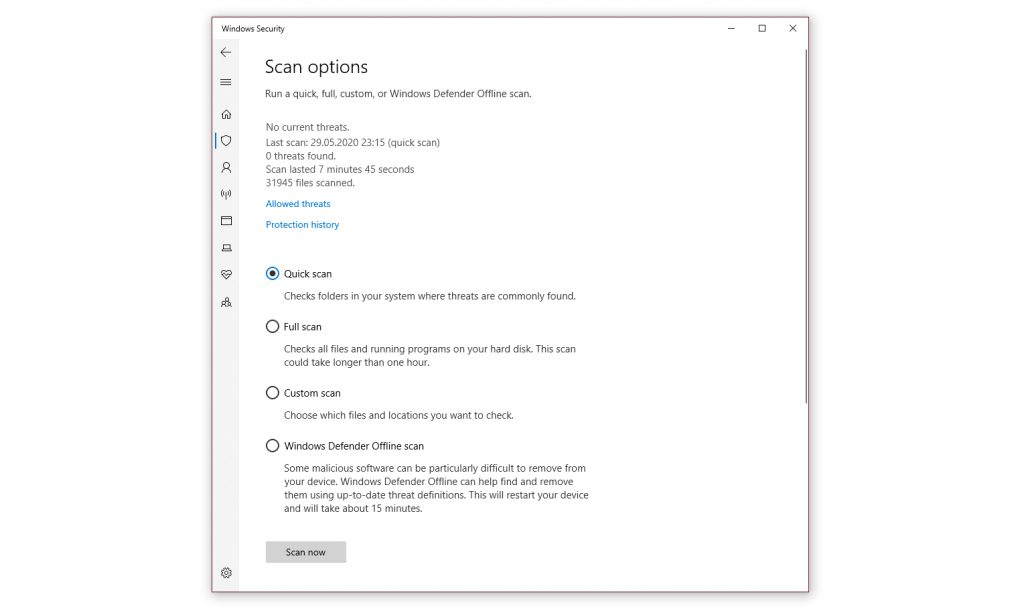
If you want to save some time or your start menu isn’t working correctly, you can use Windows key + R on your keyboard to open the Run dialog box and type “windowsdefender” and then pressing enter.
From the Virus & protection page, you can see some stats from recent scans, including the latest type of scan and if any threats were found. If there were threats, you can select the Protection history link to see recent activity.
If the guide doesn’t help you to remove Trojan:Win64/DisguisedXMRigMiner infection, please download the GridinSoft Anti-Malware that I recommended. Also, you can always ask me in the comments for getting help.
Как удалить XMRig CPU miner
Криптовалютный бум 2017 года привёл не только к существенному подорожанию видеокарт и основанию многих криптоферм и бирж. Негативное влияние на широкие массы пользователей выразилось в том, что на них, а конкретно, на вычислительных мощностях их ПК без ведома самих юзеров решили зарабатывать хакеры и создатели вредоносного программного обеспечения. В рамках данной статьи мы рассмотрим, как бороться с одним из популярных вирусных майнеров.
Удаляем XMRig CPU miner
Изначально сама программа XMRig CPU miner была и остаётся вполне добросовестным майнером, с помощью которого пользователи добывают валюту Monero, однако существует и одноимённый майнинговый вирус, использующий мощность процессора компьютера неосторожного пользователя для скрытой добычи криптовалюты сторонними лицами. Разобраться с ним можно двумя основными способами, которые доступны для комбинирования.
Способ 1: Автоматическое удаление
Майнинговые вирусы – очень скрытные и живучие, поэтому не факт, что даже установленный у вас антивирус сможет вовремя среагировать на заражённый файл, пока тот не укоренился в доверенных системных процессах Windows и реестре. Кроме того, часто обычного удаления не хватает, потому как вирус переписывает стандартное поведение ОС. Вследствие этого, при очередной проверке системных файлов, не найдя нужных элементов, ПК попытается их восстановить из-за того, что майнер создал такую инструкцию в реестре, позаботившись о своём выживании и возвращении при попытке от него избавиться.
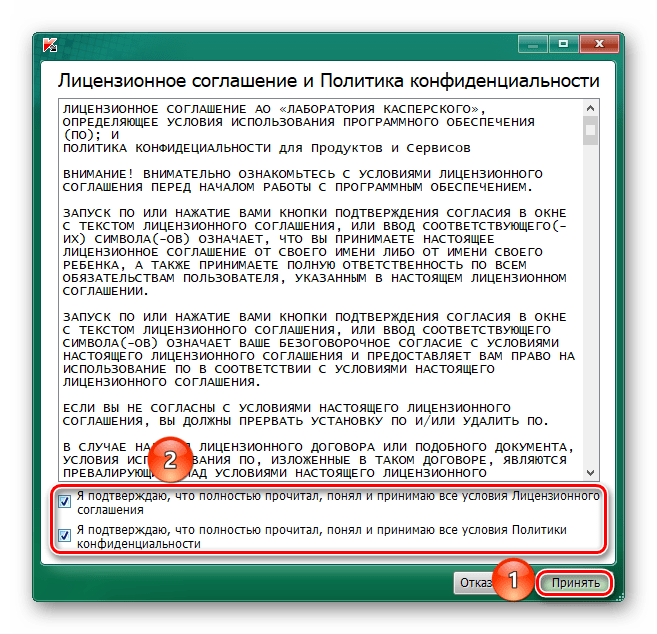
Для того чтобы удалить вирус и возможности его «реинкарнации», воспользуйтесь программами-сканерами, которые можно использовать параллельно с вашим антивирусным софтом, потом найдите проблемы реестра и, если какие-либо установки будут ссылаться на удалённые майнинговые файлы, исправьте их. Поиск и удаление вирусов с помощью Kaspersky Virus Removal Tool производится так:
-
После открытия исполняемого файла примите условия «Лицензионного соглашения», а также «Политики конфиденциальности», кликнув по соответствующим галочкам, иначе сканер не запустится, после чего нажмите на кнопку «Принять».
Kaspersky Virus Removal Tool – крайне дотошный сканер, особенно в случаях, когда нужно проверить все элементы системы, поэтому диагностика может занять около десяти минут и даже больше.
Лечащая утилита Kaspersky Virus Removal Tool прекрасно справляется с удалением майнинговых вирусов, и XMRig CPU miner — не исключение, единственным неудобством может стать то, что если заражённому файлу удастся хорошо спрятаться, в таком случае на его поиск уйдёт несколько десятков минут вашего времени.
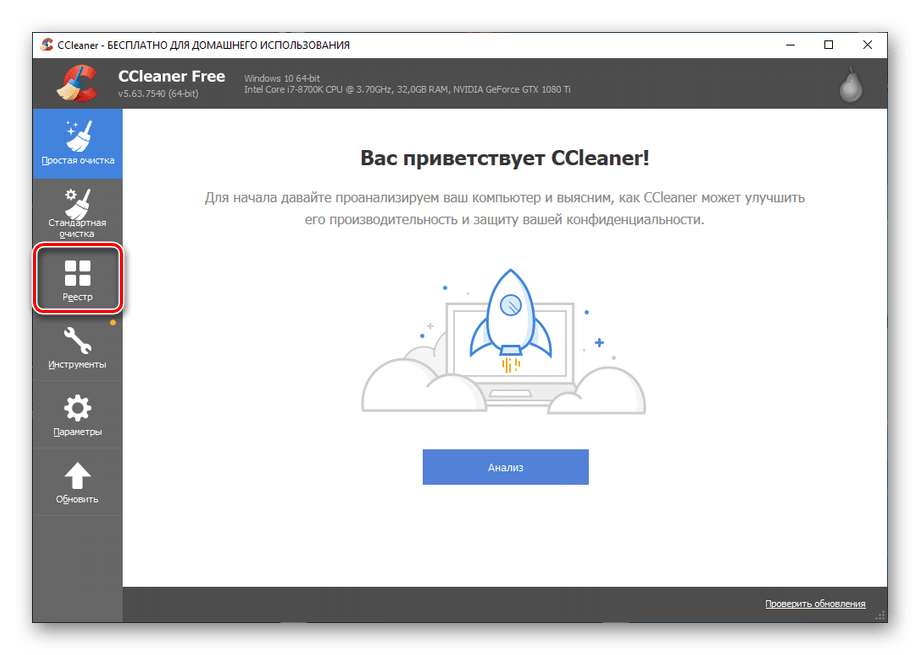
Эффективно использовать лечащую утилиту в комбинации с оптимизатором для того, чтобы очистить реестр ОС от остатков вредоносного ПО и гарантировать невозвращение вируса. Мы рекомендуем вам воспользоваться CCleaner и произвести такие действия:
- Выберите раздел «Реестр».
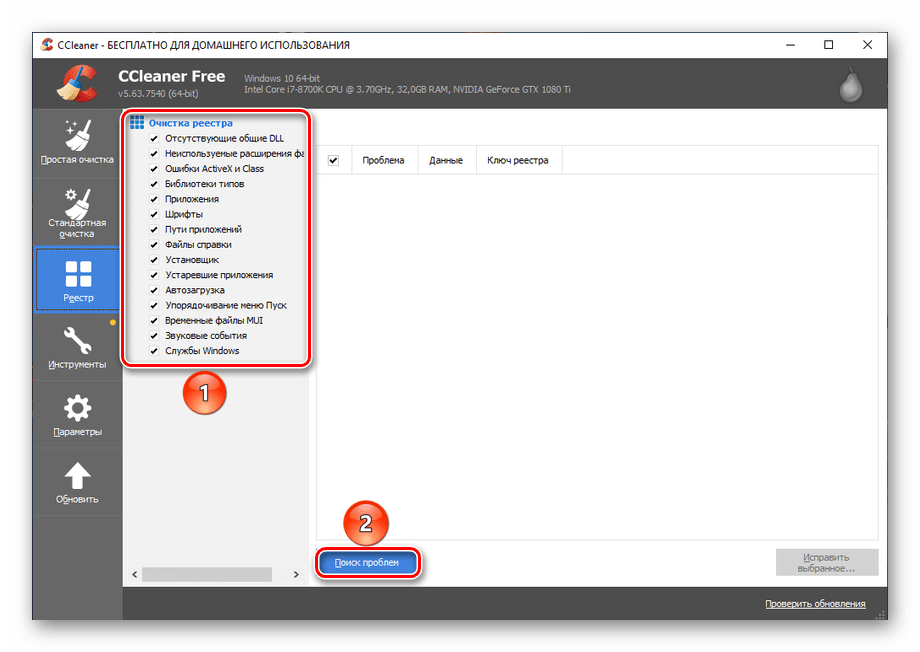
- Пометьте все возможные варианты неполадок галочками и нажмите «Поиск проблем».
- Подождите, пока приложение ищет сбои.
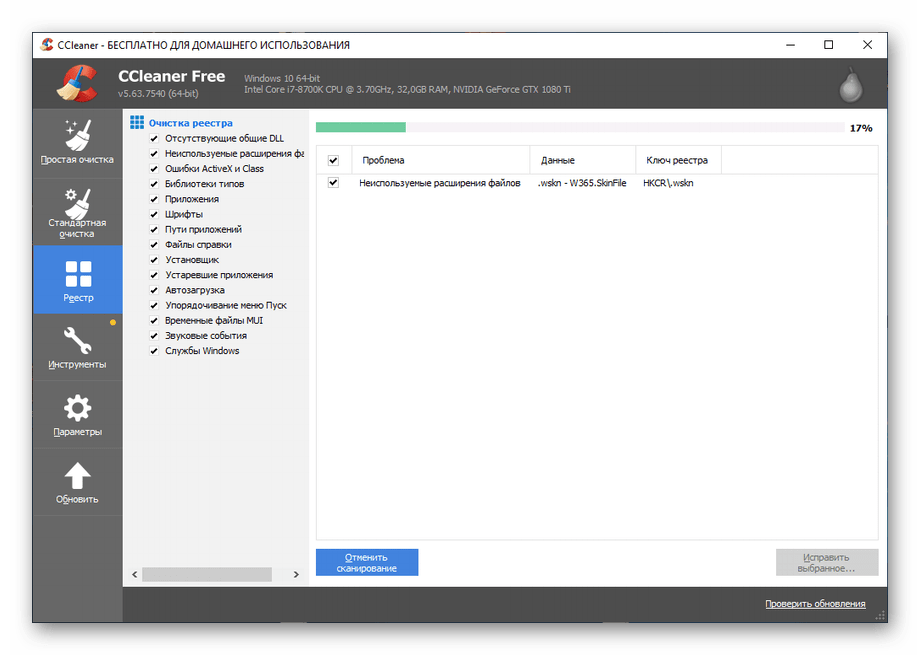
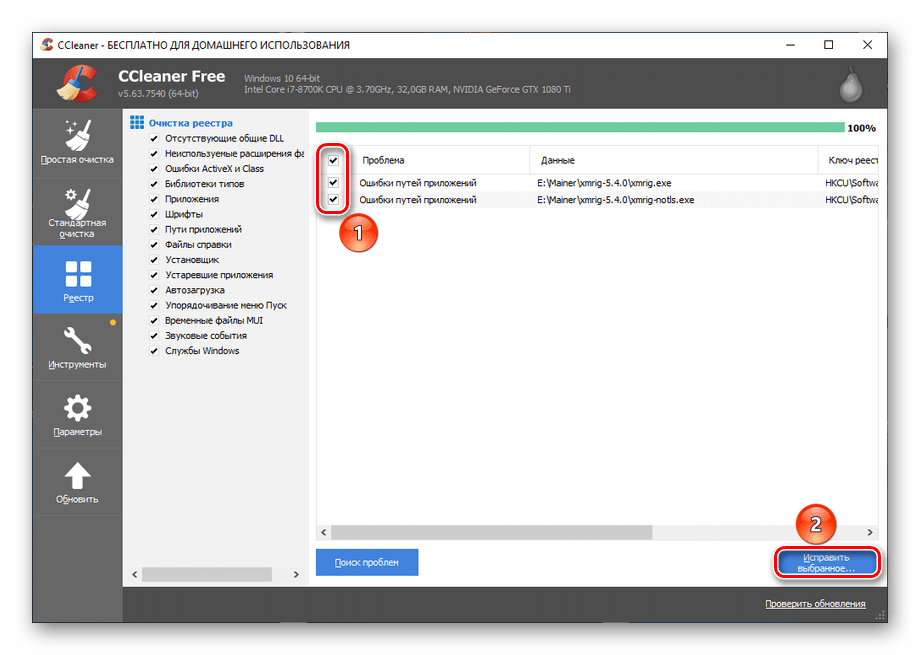
- Выделите все найденные проблемы реестра и нажмите «Исправить выбранное».
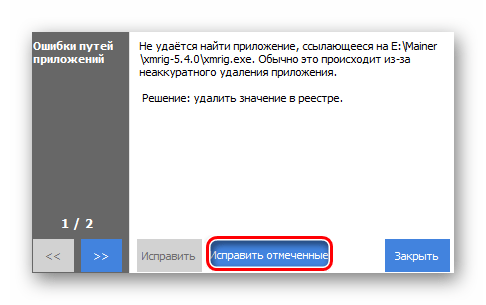
- Нажмите на «Исправить отмеченные», чтобы сразу разобраться со всем найденным.
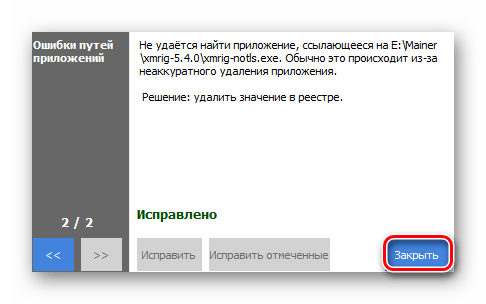
- Завершите работу с программой, кликнув по «Закрыть».
Хоть это и не обязательно, но мы настоятельно рекомендуем перезагрузить компьютер, чтобы изменения системы вступили в полную силу.
Использование лечащей утилиты и оптимизатора является эффективной мерой против всего вредоносного программного обеспечения и майнинговых вирусов в частности. Таким образом, вы очищаете систему и не оставляете возможности зловредному ПО переустановиться.
Способ 2: Ручное удаление
Отсутствие возможности или нежелание по какой-либо причине использовать специализированный софт для поиска и вредоносного программного обеспечения и починки реестра не станет преградой для удаления вируса, хотя будет несколько сложнее. Производить всю процедуру в ручном режиме необходимо в 3 последовательных этапа, о которых и пойдет речь далее на примере Windows 10.
- Найдите через меню «Пуск» приложение «Установка и удаление программ» и откройте его.
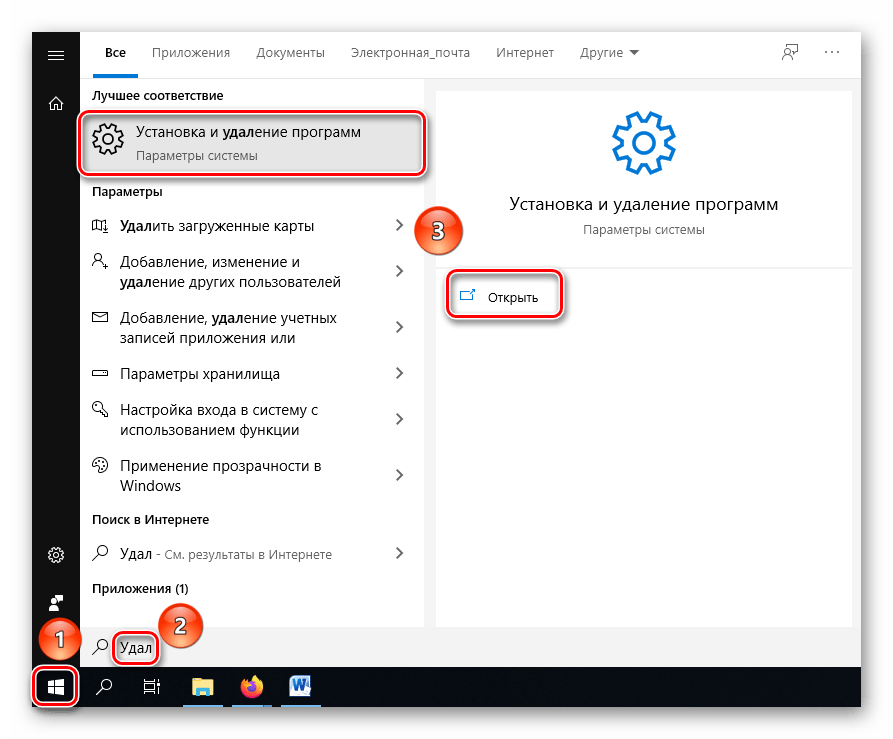
- В строке поиска найдите приложение, которое вы подозреваете во вредоносности, или отсортируйте их все по категории «Дата установки», чтобы найти недавно установленные, если вы не уверены в том, какая именно программа грузит систему. После определения приложения удалите его, нажав на кнопку «Удалить».
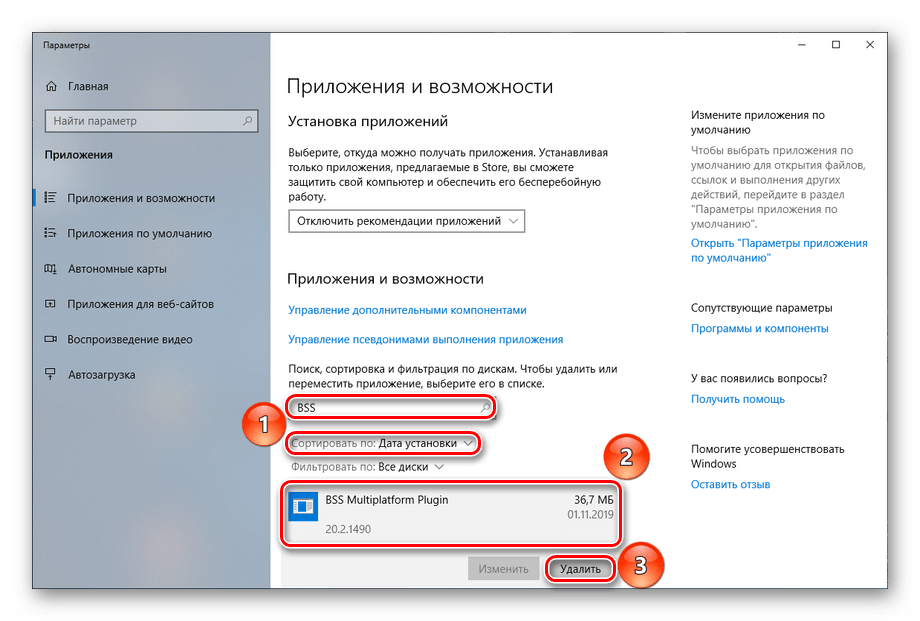
Такой способ удаления хоть не отличается оригинальностью, однако может сработать, если причиной заражения стала установка стороннего приложения. При этом вредоносное ПО может замаскироваться, и тогда придётся пойти на некоторые ухищрения, чтобы его удалить, о чём подробно рассказано в нижеприведённых статьях.
Шаг 2: Отключение автозагрузки
Когда «тело» загружающей программы удалено, осталось ликвидировать возможности восстановления, для этого необходимо очистить его параметры автозагрузки, если таковые еще имеются (а с вирусами такое часто бывает). Выполните следующие действия:
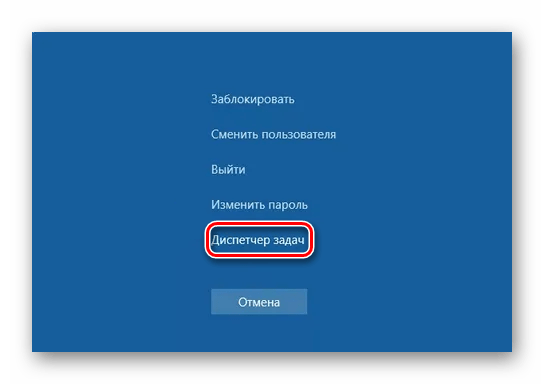
- Нажмите комбинацию клавиш «Ctrl+Alt+Delete» и кликните по «Диспетчер задач».
- Перейдите на вкладку «Автозагрузка», выберите процесс, который вызывает у вас сомнения, кликните по нему правой кнопкой мыши и нажмите «Отключить».
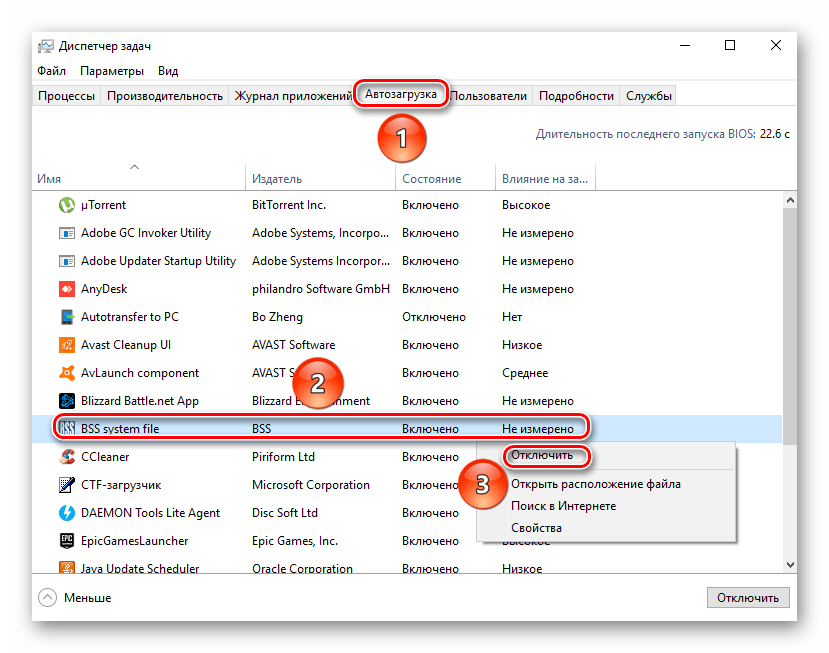
Отключив опасному ПО возможность автозагрузки, вы предотвратите его возвращение на ПК и восстановление вредоносной функциональности.
Вероятно, что у вас не будет никакого схожего процесса после удаления программы и это действие можно пропустить. Но если одноимённый с вирусом процесс всё же присутствует, воспользуйтесь пунктом «Открыть расположение файла», кликнув по нему ПКМ, и вручную зачистить остатки подозрительного приложения.
Шаг 3: Очистка реестра
Когда само ПО и инструкции по его автозагрузке удалены, следующим шагом станет очистка реестра от вредоносных элементов.
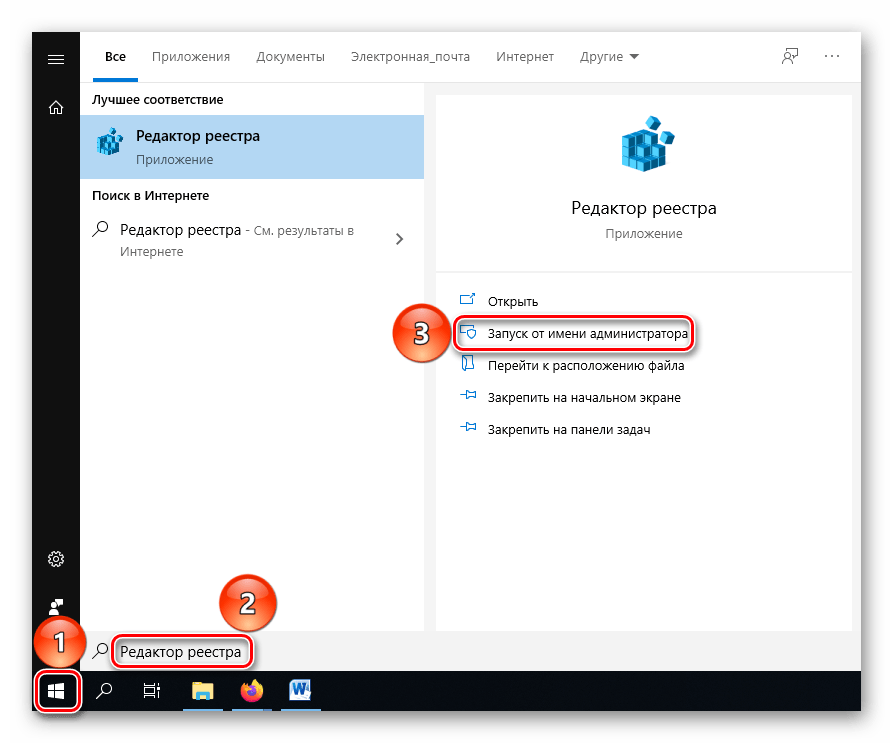
- Отыщите с помощью поиска меню «Пуск» приложение «Редактор реестра» и произведите «Запуск от имени администратора», чтобы система точно не запретила вам вносить изменения в реестр.
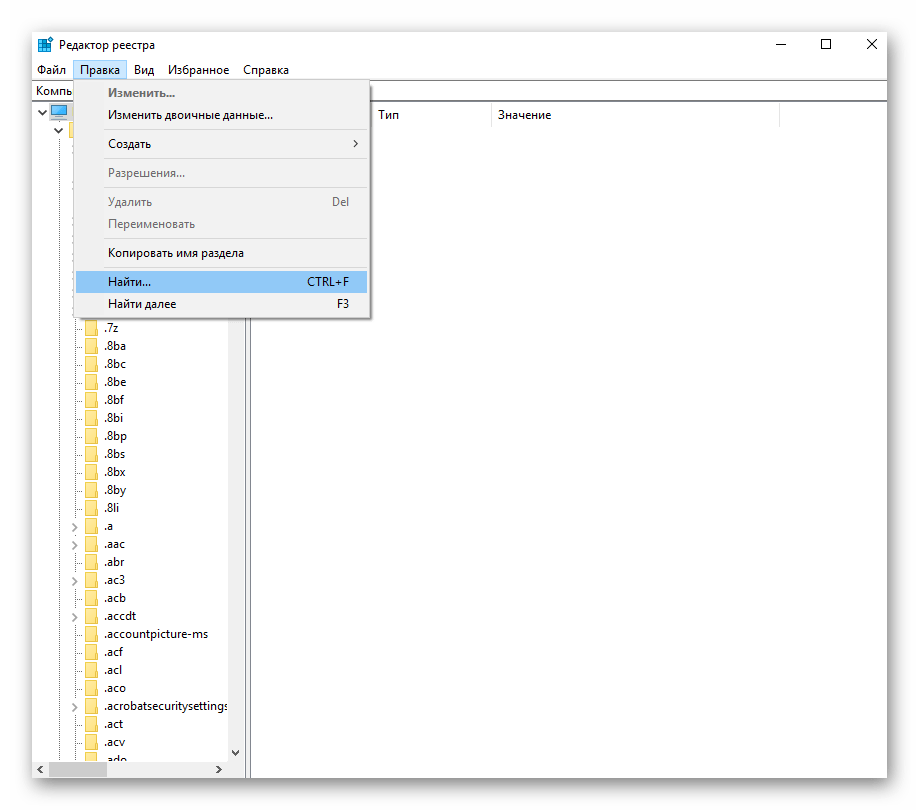
- Кликните по «Правка», а после нажмите на «Найти…», но также можно воспользоваться комбинацией клавиш «Ctrl+F».
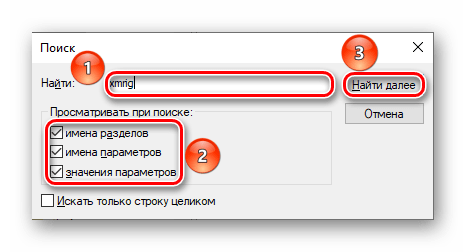
- Введите в строку поиска xmrig , проставьте все галочки под строкой «Просматривать при поиске», для максимального охвата и нажмите «Найти далее».
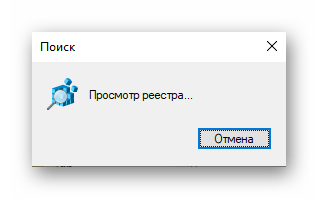
- Подождите, пока система не просмотрит реестр.
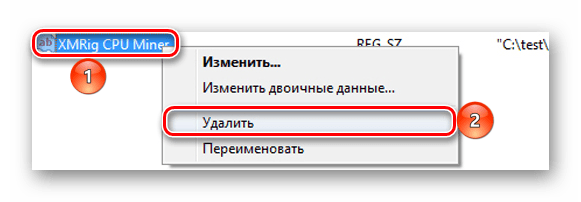
- Кликните по найденной записи реестра правой кнопкой мыши и выберите в контекстном меню пункт «Удалить».
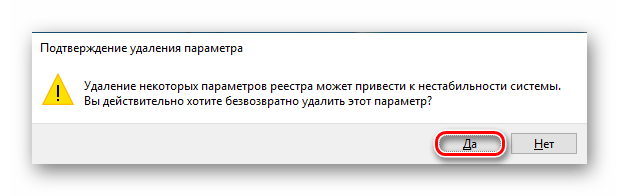
- Подтвердите удаление элемента реестра, нажав «Да».
Отныне от влияния вируса свободен и реестр, а риск встретить его вновь из-за автоматического восстановления ликвидирован.
Последним аккордом в чистке ОС станет восстановление повреждённых файлов, ведь если вирус мимикрировал под полезный софт и взаимодействовал с системой длительное время, то велика вероятность, что он своей деятельностью нанёс некоторый урон компонентам Windows. Этот ущерб можно определить и восполнить, произведя следующие действия:
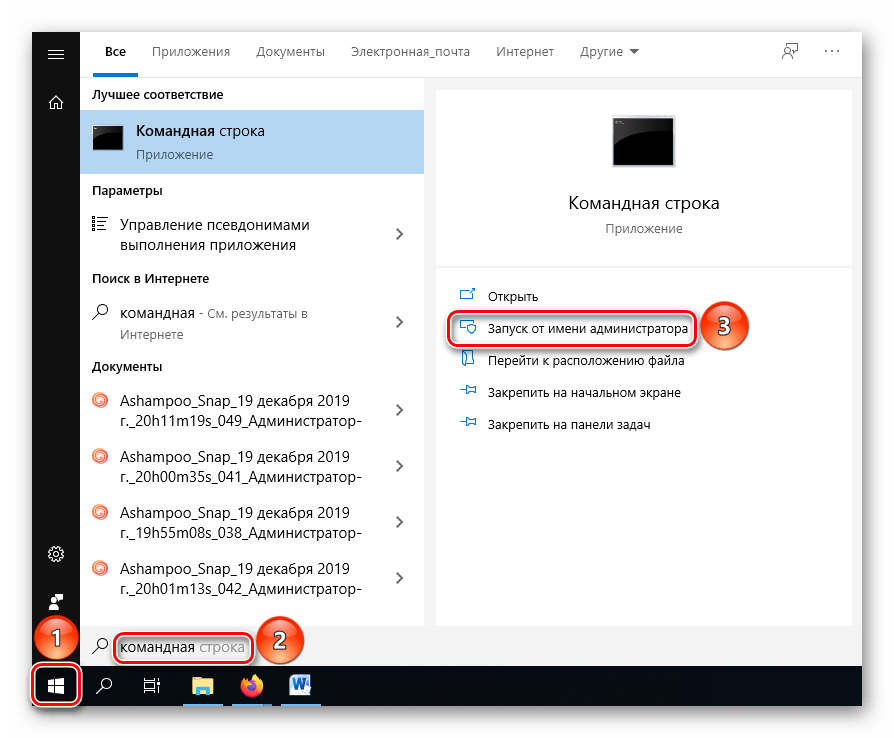
- Найдите и откройте приложение «Командная строка» в поиске меню «Пуск», инициируйте «Запуск от имени администратора», чтобы строка восприняла нужную команду, чего может не случиться в обычном режиме.
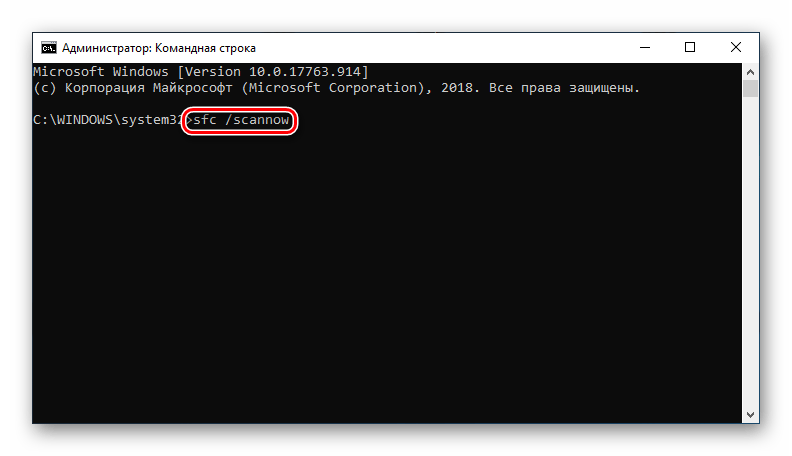
- Введите команду sfc /scannow , это приведёт к началу сканирования системы и автоматического исправления повреждённых файлов, что может занять приличное количество времени.
- Подождите, пока ПК проверяет систему, не ожидайте быстрого прекращения процесса.
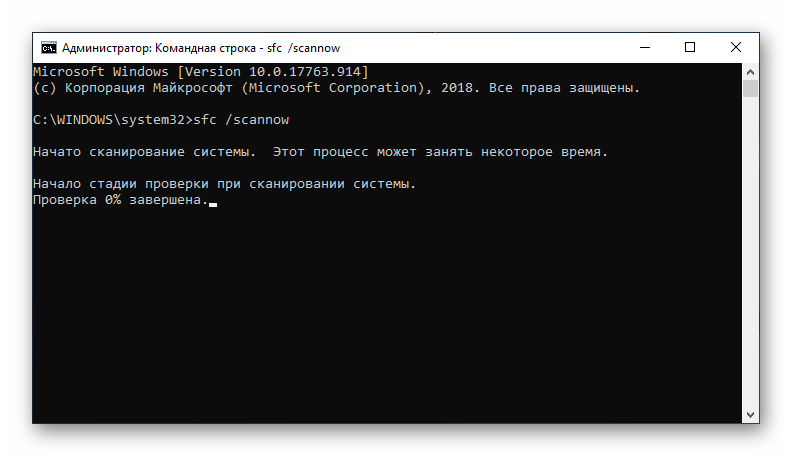
- Просмотрите результат сканирования и восстановления файлов.
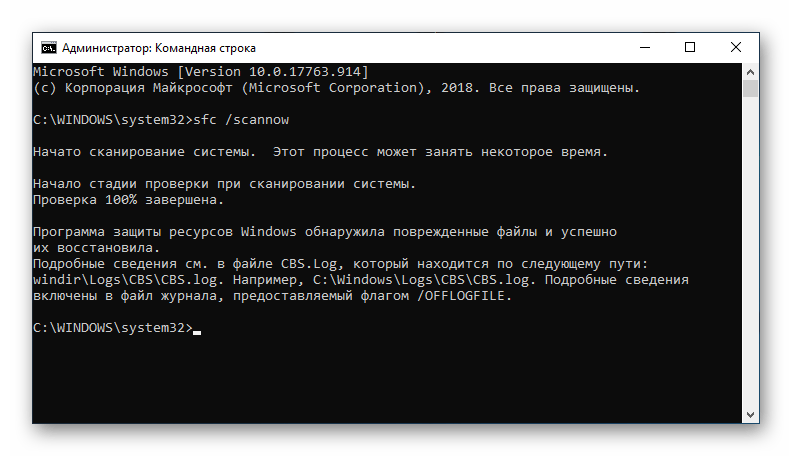
Постарайтесь не щёлкать левой кнопкой мыши по интерфейсу «Командной строки» во время проверки или восстановления файлов. Это может привести к подвисанию и приостановке выполняемой команды. При подозрении приложения в зависании, нажмите на кнопку «Enter», для того чтобы проверить статус исполняемого процесса.
Таким образом, вы устранили последствия пребывания майнингового вируса на вашем компьютере. Остаётся перезагрузить ПК и довольствоваться проделанной вручную работой. И не стоит забывать, что описанные выше методы можно комбинировать, сначала выполнив автоматическую проверку, а после самостоятельно избавиться от следов. В таком случае вы можете быть полностью уверены, что вредоносное программное обеспечение исчезло с вашего компьютера.
How to remove DisguisedXMRigMiner Trojan from PC?

 The name of this type of malware is an allusion to a widely known tale regarding Trojan Horse, which was utilized by Greeks to get in the city of Troy and win the war. Like a fake horse that was made for trojans as a gift, DisguisedXMRigMiner trojan virus is distributed like something legit, or, at least, effective. Harmful apps are concealing inside of the DisguisedXMRigMiner trojan virus, like Greeks inside of a big wooden dummy of a horse. 1
Trojan viruses are among the leading malware types by its injection rate for quite a very long time. And currently, throughout the pandemic, when malware got significantly active, trojan viruses boosted their activity, too. You can see a number of messages on different websites, where users are grumbling about the DisguisedXMRigMiner trojan virus in their computers, as well as requesting aid with DisguisedXMRigMiner trojan virus removal.
Trojan DisguisedXMRigMiner is a sort of virus that injects into your computer, and then performs different harmful functions. These functions depend upon a sort of DisguisedXMRigMiner trojan: it may serve as a downloader for additional malware or as a launcher for an additional malicious program which is downloaded along with the DisguisedXMRigMiner trojan virus. During the last two years, trojans are also dispersed via email add-ons, and most of cases utilized for phishing or ransomware injection.
DisguisedXMRigMiner 2 also known as
| Lionic | Trojan.Win32.Miner.4!c |
| Elastic | malicious (high confidence) |
| Cynet | Malicious (score: 99) |
| ALYac | Trojan.GenericKDZ.73199 |
| Cylance | Unsafe |
| Sangfor | CoinMiner.Win32.Miner.gen |
| CrowdStrike | win/malicious_confidence_60% (D) |
| Alibaba | Trojan:Win64/Miners.82cf5ad5 |
| Cybereason | malicious.41dc69 |
| Cyren | W64/Trojan.HYFP-1547 |
| Symantec | Trojan.Gen.MBT |
| ESET-NOD32 | a variant of Win64/CoinMiner.CY potentially unwanted |
| APEX | Malicious |
| Avast | Win64:CoinminerX-gen [Trj] |
| ClamAV | Win.Trojan.Miner-9835754-0 |
| Kaspersky | HEUR:Trojan.Win32.Miner.gen |
| BitDefender | Trojan.GenericKDZ.73199 |
| NANO-Antivirus | Trojan.Win64.Miner.iuzmfc |
| MicroWorld-eScan | Trojan.GenericKDZ.73199 |
| Tencent | Win32.Trojan.Miner.Lmky |
| Ad-Aware | Trojan.GenericKDZ.73199 |
| Sophos | Generic PUA LG (PUA) |
| VIPRE | Trojan.Win32.Generic!BT |
| TrendMicro | TROJ_GEN.R002C0WK321 |
| McAfee-GW-Edition | BehavesLike.Win64.Fake.gc |
| FireEye | Generic.mg.38c43f741dc69d30 |
| Emsisoft | Trojan.GenericKDZ.73199 (B) |
| Jiangmin | Trojan.Miner.odb |
| Avira | HEUR/AGEN.1137162 |
| Antiy-AVL | Trojan/Generic.ASBOL.C5E3 |
| Kingsoft | Win32.Troj.Undef.(kcloud) |
| Microsoft | Trojan:Win64/DisguisedXMRigMiner |
| GData | Trojan.GenericKDZ.73199 |
| AhnLab-V3 | Trojan/Win64.CoinMiner.C4344951 |
| McAfee | GenericRXAA-AA!38C43F741DC6 |
| MAX | malware (ai score=83) |
| VBA32 | Trojan.Miner |
| Malwarebytes | Trojan.BitCoinMiner |
| Panda | Trj/CI.A |
| Yandex | Trojan.GenAsa!hNDKU9hr3EM |
| Ikarus | Trojan.Win64.CoinMiner |
| MaxSecure | Trojan.Malware.11387115.susgen |
| Fortinet | Adware/Miner |
| AVG | Win64:CoinminerX-gen [Trj] |
| Paloalto | generic.ml |
| Qihoo-360 | Win64/Miner.Coinminer.H8oANncA |
What are the symptoms of DisguisedXMRigMiner trojan?
- The binary likely contains encrypted or compressed data.;
- The executable is compressed using UPX;
The typical indicator of the DisguisedXMRigMiner trojan virus is a steady appearance of a wide range of malware – adware, browser hijackers, and so on. As a result of the activity of these malicious programs, your computer ends up being extremely sluggish: malware uses up substantial amounts of RAM and CPU abilities.
One more noticeable effect of the DisguisedXMRigMiner trojan virus visibility is unknown operations displayed in task manager. Frequently, these processes may attempt to simulate system processes, but you can recognize that they are not legit by looking at the genesis of these processes. Pseudo system applications and DisguisedXMRigMiner trojan’s processes are always specified as a user’s programs, not as a system’s.
How to remove DisguisedXMRigMiner trojan virus?
- Download and install Loaris Trojan Remover.
- Open Loaris and perform a “Standard scan“.
- “Move to quarantine” all items.
- Open “Tools” tab – Press “Reset Browser Settings“.
- Approve the reset pressing “Yes” button in the appeared window.
- Restart your computer.
To clean up DisguisedXMRigMiner trojan and also ensure that all added malware, downloaded with the help of this trojan, will be wiped out, too, I’d recommend you to use Loaris Trojan Remover.
 DisguisedXMRigMiner trojan virus is very tough to remove manually. Its paths are very hard to track, as well as the changes executed by the DisguisedXMRigMiner trojan are concealed deeply within the system. So, the possibility that you will make your system 100% clean of trojans is extremely low. And also don’t ignore malware that has been downloaded with the help of the DisguisedXMRigMiner trojan virus. I feel these arguments are enough to assure that eliminating the trojan virus manually is an awful idea.
DisguisedXMRigMiner removal guide
To spot and remove all malware on your PC using Loaris, it’s better to make use of Standard or Full scan. Removable scan, as well as Custom, will check only specified directories, so these scans cannot provide the full information.

You can spectate the detects during the scan process goes. However, to execute any actions against spotted malicious programs, you need to wait until the scan is finished, or to stop the scan.

To choose the specific action for each detected malicious items, choose the button in front of the detection name of detected malicious programs. By default, all malicious items will be sent to quarantine.

How to remove DisguisedXMRigMiner Trojan?

Name: DisguisedXMRigMiner
Description: Trojan DisguisedXMRigMiner is a kind of virus that infiltrates into your computer, and after that performs different destructive functions. These features depend upon a type of DisguisedXMRigMiner trojan: it can act as a downloader for many other malware or as a launcher for another destructive program which is downloaded in addition to the DisguisedXMRigMiner trojan. During the last two years, trojans are also dispersed via e-mail attachments, and most of situations utilized for phishing or ransomware infiltration.